Black Friday Speed Sale: Save 75% on Every Exam Bundle! Use coupon code below now! - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

GUARD CyberArk Guardian Exam Free Practice Exam Questions (2026 Updated)

Prepare effectively for your CyberArk GUARD CyberArk Guardian Exam certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 1 / 1
Total 60 questions

The Active Directory manager asks you to temporarily enable Object Level Access Control (OLAC) on a Safe they own so they can control which users may use a particular Domain Admin account.

What OLAC limitation should you explain to them?

A.

OLAC does not enable granular control of which users can use a specific object.

B.

Once enabled, object level access control cannot be disabled.

C.

With object level access control enabled, PSM operations on the managed accounts are not supported.

D.

New accounts cannot be added to the safe, once OLAC is enabled.

At which stage is it appropriate to incorporate the C3 Alliance integrations?

A.

Since we already have integrations available and little development is required, they should all be completed in Stage 1.

B.

Integrate the security tools in Stage 1 and other tools such as RPA in Stage 2.

C.

They are less of a risk, so we should leave them until Stage 3 and focus on other privileged accounts first.

D.

They should all be integrated prior to the actual ’go-live' of CyberArk PAM.

A new Vault is to be deployed in a highly regulated environment. Regulations require that every operating system on the network be updated regularly.

How does CyberArk recommend automatically updating hardened Vaults?

A.

Using a dedicated WSUS server and install patches monthly.

B.

Vaults do not require OS updates.

C.

Manually install updates whenever CyberArk notifies you.

D.

Integrate the Vault with the domain for monthly updates.

The customer currently has a Primary and DR vault. They have heard that another DR vault can be deployed for additional redundancy, so they order a physical server and rack and stack it in a Co-Iocation.

However, when installing the DR module on the new vault, the installation fails. What is the most likely cause?

A.

None of the PVWAs can communicate with the new vault.

B.

The customer does not have enough DR licenses.

C.

The vault has not been hardened correctly.

D.

Unless the configuration is using the Distributed Vault architecture, you can only have 2 total vault servers.

A financial institution uses CyberArk Privileged Session Manager (PSM) to monitor privileged access to production servers.

The security team requires authorized auditors to terminate suspicious privileged sessions immediately when potentially malicious administrative activity is detected.

An auditor can view active sessions in PVWA but cannot terminate them. The administrator confirms that session monitoring is enabled and the PSM infrastructure is functioning correctly.

What configuration should be implemented to allow the auditor to terminate active privileged sessions?

A.

Add the auditor to the Vault Administrators group and grant full administrative access to all Recording Safes.

B.

Enable the Require Dual Control Password Access Approval rule in the Master Policy and assign the auditor as an approver.

C.

Add the auditor to the PSMLiveSessionTerminators group and ensure that this group has the required membership in the Safes containing the managed accounts.

D.

Assign the auditor the Retrieve Accounts permission on the relevant Safes and enable automatic password reconciliation.

You need to implement a solution that requires users to verify they have run an application.

Which solution is best?

A.

EPM Step-up authentication.

B.

Accounts with Least Privilege configured.

C.

Ad Hoc Access and Ad Hoc Connections.

D.

PTA Risky Commands.

You are deploying PAM for a globally distributed organization with locations in England (UK), Boston (USA), and Hong Kong (ROC).

Each location has two physically separated data centers for disaster mitigation. England DC 1 has been designated as the Primary DC. Components will be scaled horizontally where needed in later phases, and all DCs can communicate with one another.

The solution must provide:

• Resilient access to target systems

• A highly resilient primary location

• Recovery from all locations

• Global resilience to outages

• A single Master Policy governing the solution

Load balancing is possible between DCs in the same region.

What is the minimum required to meet these requirements?

A.

UK DC 1 :- Vault, PVWA, PSM, CPM, PTA

UK DC 2 :- DR Vault, PVWA, PSM, DR PTA

US DC 1 :- DR Vault, PVWA, PSM, CPM

US DC 2 :- PVWA, PSM

ROC DC 1 :- DR Vault, PVWA, PSM, CPM

ROC DC 2 :- PVWA, PSM

B.

UK DC 1 :- Vault, PVWA, PSM, CPM, PTA

UK DC 2 :- PVWA, PSM, DR PTA

US DC 1 :- DR Vault, PVWA, PSM, CPM

US DC 2 :- PVWA, PSM

ROC DC 1 :- DR Vault, PVWA, PSM, CPM

ROC DC 2 :- PVWA, PSM

C.

UK DC 1 :- Vault, PVWA, PSM, CPM, PTA

UK DC 2 :- DR Vault, PVWA, PSM, CPM, PTA

US DC 1 :- Vault, PVWA, PSM, CPM, PTA

US DC 2 :- DR Vault, PVWA, PSM, CPM, PTA

ROC DC 1 :- Vault, PVWA, PSM, CPM, PTA

ROC DC 2 :- DR Vault, PVWA, PSM, CPM, PTA

D.

UK DC 1 :- Vault, PVWA, PSM, CPM, PTA

UK DC 2 :- DR Vault, PVWA, PSM, CPM, DR PTA

US DC 1 :- DR Vault, PVWA, PSM, CPM

US DC 2 :- DR Vault, PVWA, PSM, CPM

ROC DC 1 :- DR Vault, PVWA, PSM, CPM

ROC DC 2 :- DR Vault, PVWA, PSM, CPM

During phase 1 of the CyberArk Blueprint, what action is recommended for managing service accounts?

A.

Create new accounts specifically for the services and then swap them over.

B.

Identify and remove unnecessary privilege's in AD or in local account.

C.

Onboard the account to CyberArk and identify all usages, start rotation.

D.

Create a safe design to onboard the Service accounts to and create platforms for usages.

What are the three Guiding Principles of the CyberArk Blueprint?

A.

Credential Theft, Lateral and Vertical Movement, Privilege Escalation and Abuse.

B.

Identity Security, Credential Theft, Lateral and Vertical Movement.

C.

Attack and Defend capability, Credential Theft, Least Privilege.

D.

Quick return on investment, Password Management, Credential Theft.

What level of support is a customer entitled to with 24x7 support?

A.

Enables customers to call the after hours Support hotline for all issues.

B.

Enables customers to call the after hours Support hotline for all Critical issues where no work can be completed in a Production environment.

C.

Enables customers to call the after hours Support hotline for all Critical or Serious issues where no work can be completed in a Production environment.

D.

Enables customers to call the after hours Support hotline for all Critical or Serious issues where no work can be completed in any environment.

In CyberArk Remote Access, when you want to copy files in PSM sessions and have more than one Remote Access Connector server, you must:

A.

Configure the load balancer with sticky sessions and use a standalone HTML5 gateway server.

B.

Configure the load balancer for round-robin load balancing and use a standalone HTML5 gateway server.

C.

Configure the load balancer with sticky sessions and deploy a PSM server instead of an HTML5 gateway server.

D.

Configure the load balancer with sticky sessions and go directly to the PSM server without an HTML5 gateway.

A customer has a hybrid infrastructure that spans multiple cloud vendors and privately owned data centers. They deployed CyberArk PAM in AWS by using CyberArk-provided scripts. Eighty percent of the customer’s infrastructure is located in privately owned data centers. The customer is concerned about availability between the cloud provider and the data center. They are cloud-first and are gradually migrating their servers to the cloud.

Active Master Policy settings:

• Require dual-control approval for password access

• Enforce exclusive check-in/check-out access

• Require password changes every 25 days

• Require password verification every 7 days

What is the most appropriate recommendation for the customer?

A.

Keep the deployment as is in AWS.

B.

Deploy an active CPM to the privately owned Data Center.

C.

Deploy a separate infrastructure in another cloud vendor.

D.

Migrate the CPM to the privately owned Data Center.

Which components are required to configure external recording storage for PSM?

A.

SMB 3.0 supported storage, A Windows Privileged Account, Storage-level Tampering Protection.

B.

SMB 3.1 supported storage, A Domain Administrator Account, Storage-level Tampering Protection.

C.

NAS Storage, a private SSH Key, Azure Key Vault.

D.

SAN Storage, AWS Access Key, AWS KMS.

What type of attack can CyberArk mitigate?

A.

Pass-the-Hash

B.

SQL Injection

C.

DDOS

D.

Phishing

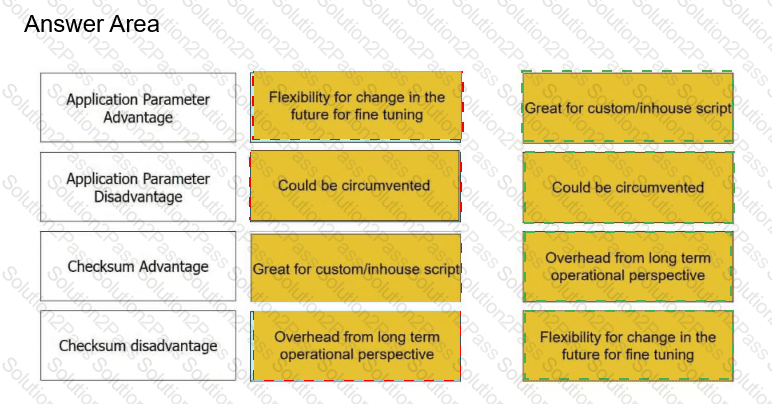
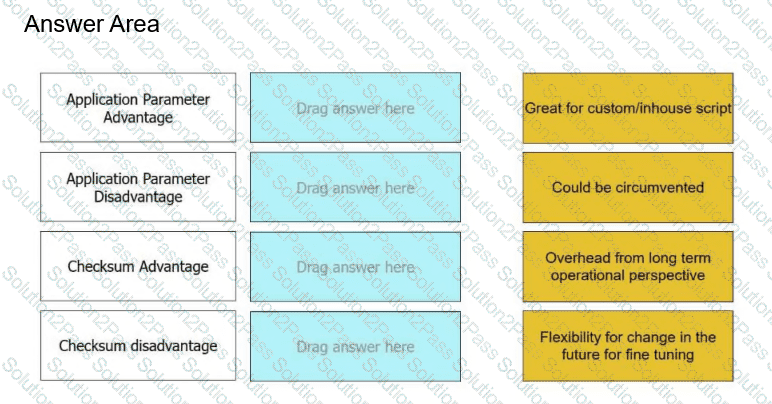
Customer ACME Corp has deployed EPM SaaS and is moving toward Advanced Application Policies.

As a Senior Consultant, help the customer understand the advantages and disadvantages of application parameters versus checksums.

Match the options to the correct category.
What is the greatest number of Conjur Standbys that can be deployed within an Auto-Failover cluster?

A.

3

B.

4

C.

5

D.

6

When Dual Control is enabled for a platform in the Master Policy, exceptions may be configured in the following two locations.

Choose two

A.

Exceptions can be configured in the safe permissions for specific users or groups.

B.

Exceptions can be configured in the object level of individual vaulted accounts associated with that platform.

C.

Exceptions can be configured for PSM connectivity at the platform level.

D.

Exceptions can be configured for specific users or groups at the master policy level.

E.

Exceptions can be configured in vault level permissions for specific users and groups.

You deployed your Primary Vault on a CyberArk-supported cloud platform by using a CyberArk-provided image, and deployed a DR Vault in a privately owned data center.

What is the best method for securing the Server Key on the DR Vault?
A.

Use KMS.

B.

Use HSM.

C.

Mount Operator CD every time Vault is started.

D.

Use Azure Key Vault.

Page: 1 / 1
Total 60 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved