Winter Sale Special - Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: xmaspas7

Easiest Solution 2 Pass Your Certification Exams

NSE6_EDR_AD-7.0 Fortinet NSE 6 - FortiEDR 7.0 Administrator Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Fortinet NSE6_EDR_AD-7.0 Fortinet NSE 6 - FortiEDR 7.0 Administrator certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 1 / 1
Total 35 questions

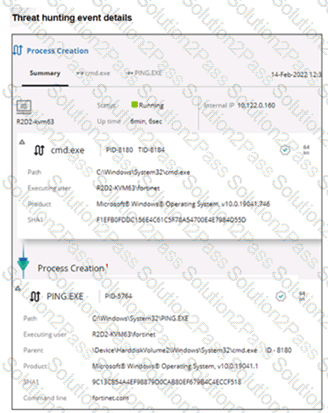
Refer to the exhibit.

Based on the threat hunting event details shown in the exhibit, which two statements about the event are true? (Choose two answers)

A.

There are no MITRE details available for this event.

B.

The activity event is associated with the file action.

C.

The PING.EXE process was blocked.

D.

The user fortinet has executed a ping command.

Which two criteria are required for integrating FortiEDR with the Fortinet Security Fabric? (Choose two answers)

A.

Central manager connected to FCS

B.

A Forensics add-on license

C.

A valid API user with access to connectors

D.

Core with core-only functionality

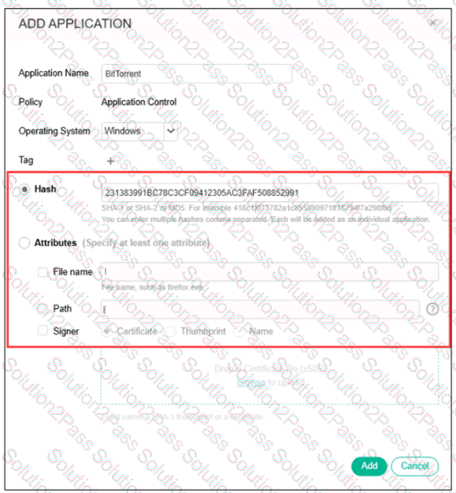
Refer to the exhibit:

You are asked to block applications based on hash attributes. Which two factors must you consider when applying the hash value? (Choose two answers)

A.

Hashes must be line-separated.

B.

Hashes must be used with at least one attribute, such as a filename or path.

C.

Hashes must be unique to each application.

D.

Hashes must follow supported formats.

Within the FortiEDR architecture, which component needs JumpBox capabilities to enable authenticated and controlled communication with FortiAnalyzer? (Choose one answer)

A.

Core

B.

Central manager

C.

Aggregator

D.

Reputation Server

You discovered that a newly installed collector does not display on the Inventory tab in the central manager. Which two troubleshooting steps must you perform? (Choose two answers)

A.

Verify that the central manager can resolve the collector hostname through DNS.

B.

Verify that TCP ports 8081 and 555 are open between the collector and the central manager.

C.

Check whether the FortiEDR services are running on the collector device.

D.

Export and review the collector logs from the Central Manager for connection errors.

You added three new applications to FortiEDR using only the Path attribute. What are two expected outcomes of this configuration? (Choose two answers)

A.

These applications will be disabled until explicitly enabled.

B.

Only applications in the specified directory paths will be blocked.

C.

These applications will be blocked only if the file name also matches.

D.

All instances of these applications will be blocked, regardless of location.

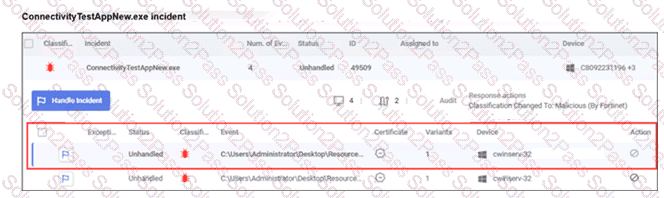
Refer to the exhibit.

What observation can you make about the ConnectivityTestAppNew.exe incident? (Choose one answer)

A.

A rule assigned action is set to block but the policy is in simulation mode.

B.

The incident has not been handled by a console administrator.

C.

The incident was archived from the console unhandled.

D.

The incident was handled automatically by the communication control policy.

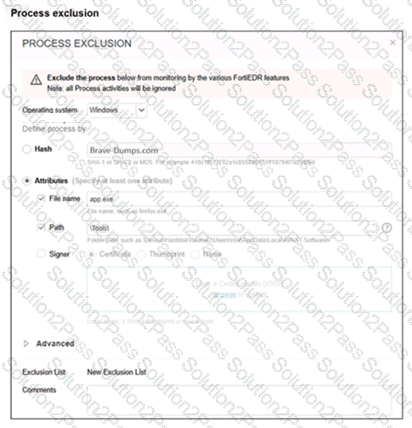
Refer to the exhibit:

You configured an execution prevention exclusion with both File Name = app.exe and Path = C:\Tools. What will FortiEDR do? (Choose one answer)

A.

Exclude only signed versions of app.exe.

B.

Exclude only app.exe when it is running from C:\Tools.

C.

Exclude app.exe whenever it appears.

D.

Exclude all files in C:\Tools.

What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)

A.

Ignores them until manually updated

B.

Stores them locally and waits for endpoint input

C.

Requests the missing hashes from the cloud reputation service

D.

Automatically blocks applications with unknown hashes

You are asked to create a playbook to isolate a device with a collector. Which action category does isolating a device with a collector fall under? (Choose one answer)
A.

Investigation

B.

Remediation

C.

Custom

D.

Notifications

Page: 1 / 1
Total 35 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved