NSE6_FSM_AN-7.4 Fortinet NSE 6 - FortiSIEM 7.4 Analyst Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Fortinet NSE6_FSM_AN-7.4 Fortinet NSE 6 - FortiSIEM 7.4 Analyst certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Refer to the exhibit.
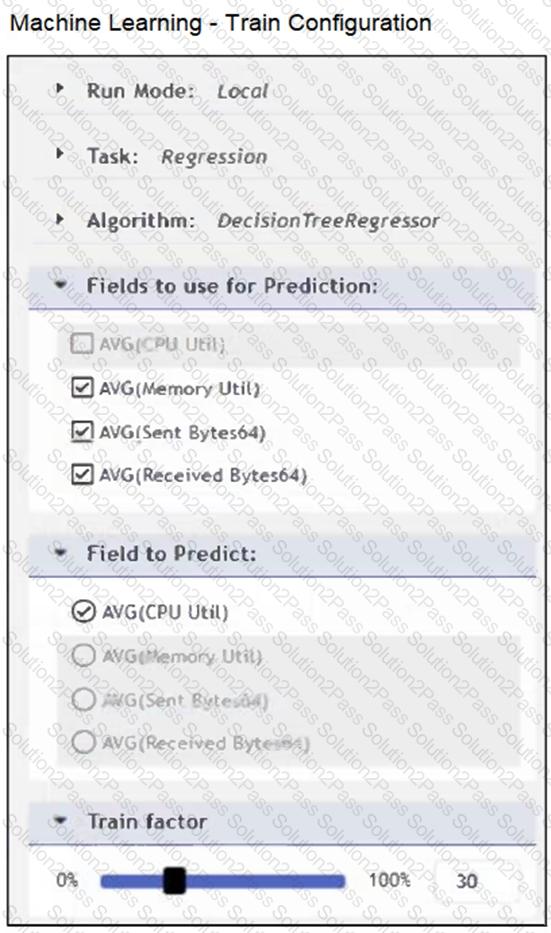
The configuration shown in the exhibit is incorrect.
What must you change to allow this configuration to be successfully applied to FortiSIEM?
You want to create a rule with multiple subpatterns but trigger an incident only if three different subpatterns are matched over a 24-hour period.
Where must you define the time period that the rule uses to evaluate all the subpatterns? (Choose one answer)
Refer to the exhibit.
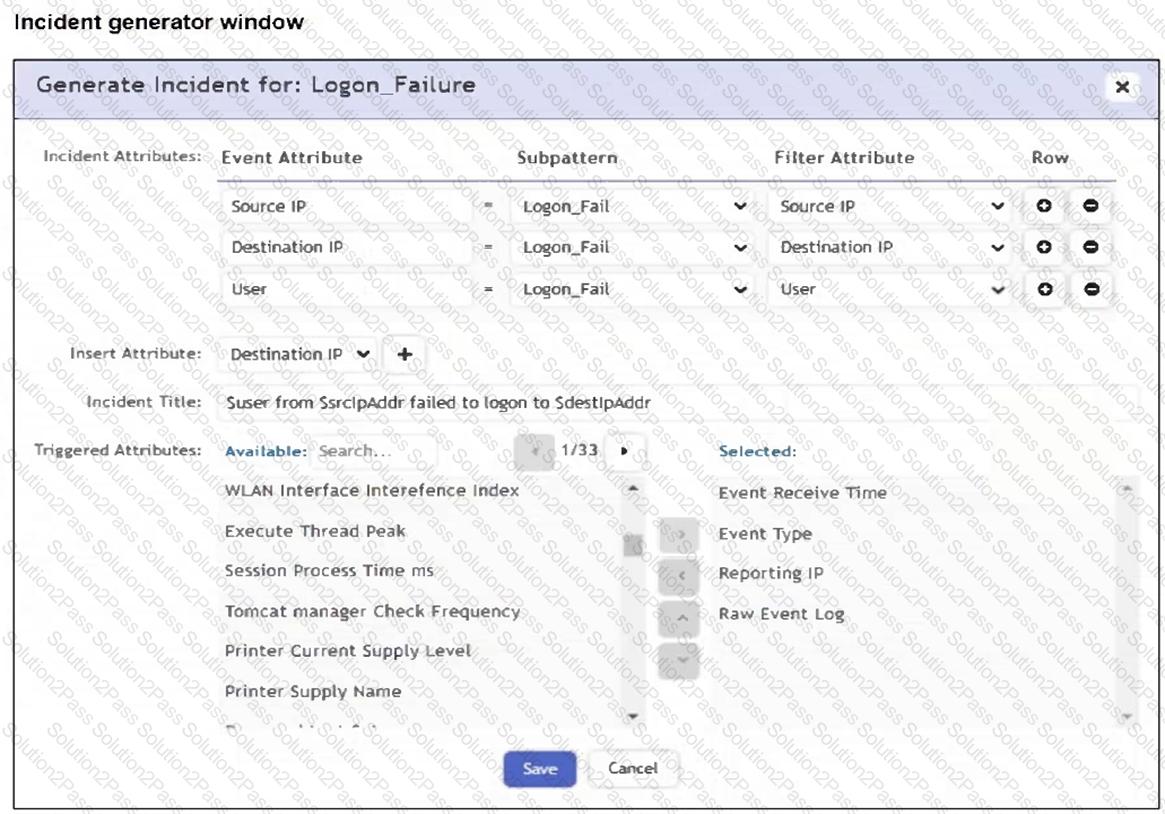
An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add Destination Host Name as an incident attribute.
What must be changed to allow the analyst to select Destination Host Name as an attribute?
Refer to the exhibit.
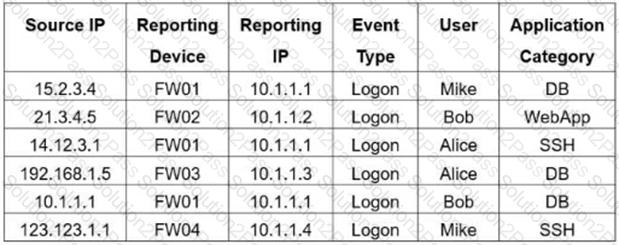
If you group the events by Reporting Device , Reporting IP , and Application Category , how many results will FortiSIEM display?
Refer to the exhibit.
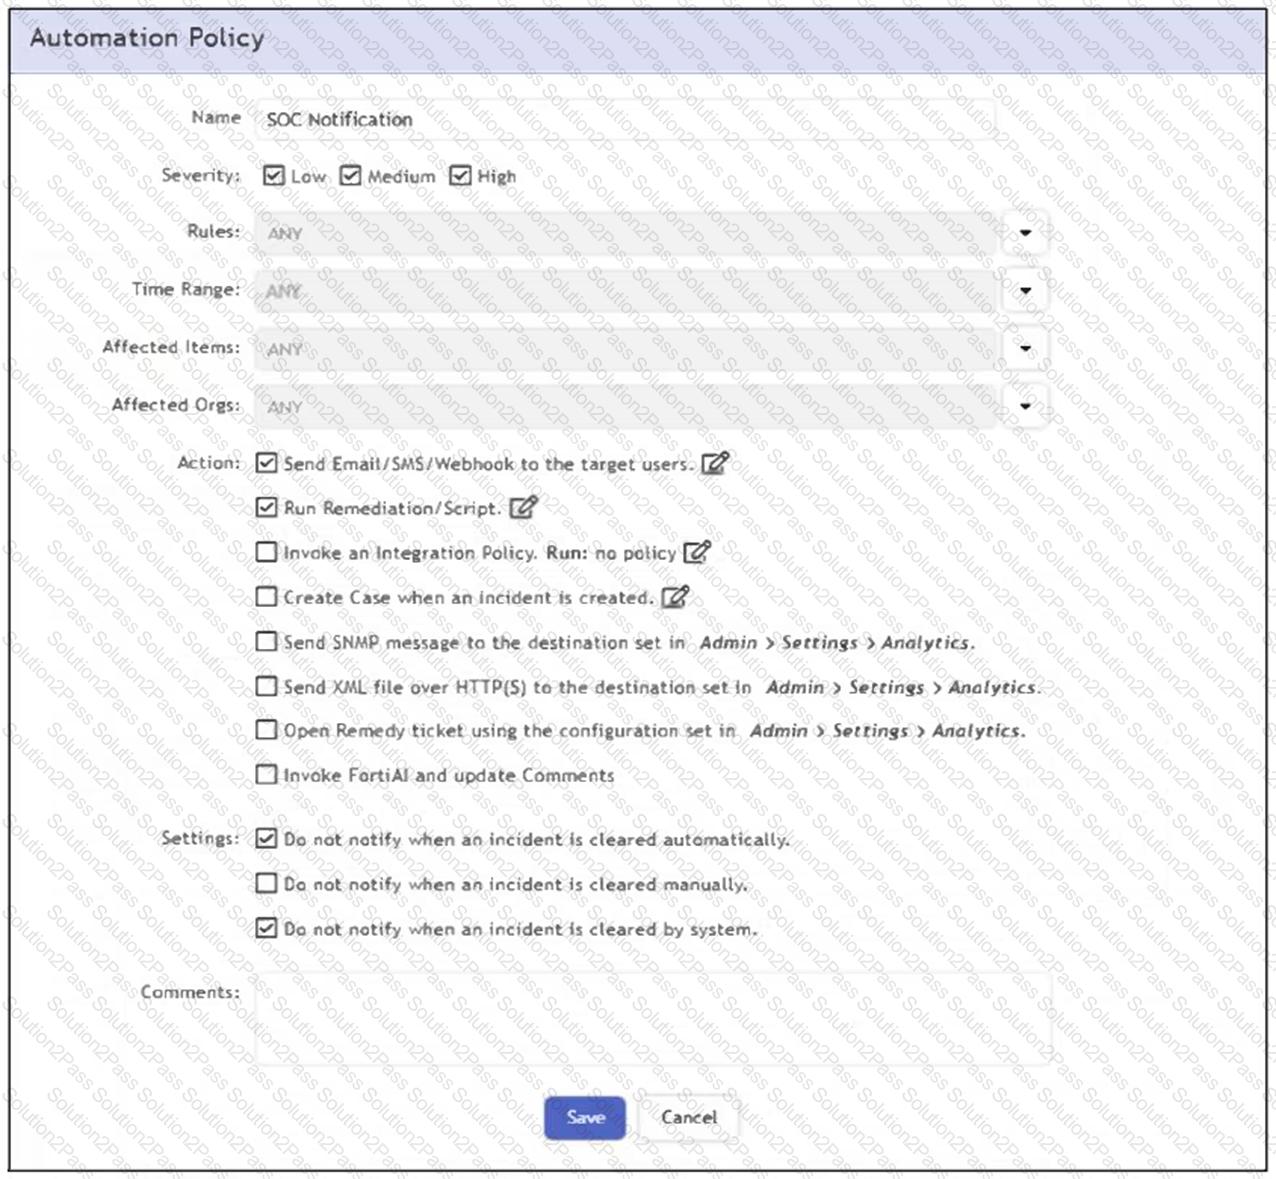
What happens when an analyst clears an incident generated by a rule containing the automation policy shown in the exhibit?
Refer to the exhibit.
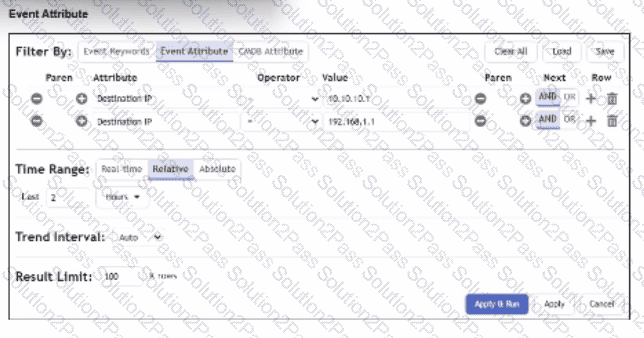
A FortiSIEM analyst is investigating an issue by examining events to two destination IP addresses. However, the analyst is not getting any results from the search.
Based on the selected filter shown in the exhibit, why is the search returning no results?
Refer to the exhibit.

Which section contains the subpattern configuration that determines how many matching events are needed to trigger the rule?
Which analytics search can be used to apply a user and entity behavior analytics (UEBA) tag to an event for a failed login by the user JSmith?
Which statement about thresholds is true?
Which two data areas can you use for user and entity behavior analytics (EBA) machine learning models? (Choose two.)
Refer to the exhibit.
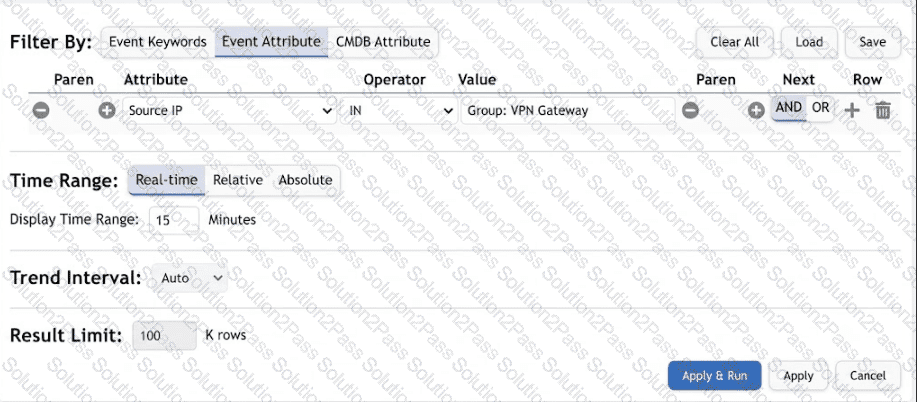
What is the Group: VPN Gateway value a reference to? (Choose one answer)
Which items are used to define a subpattern?
Which run mode takes the most time to perform machine learning tasks?
Refer to the exhibit.
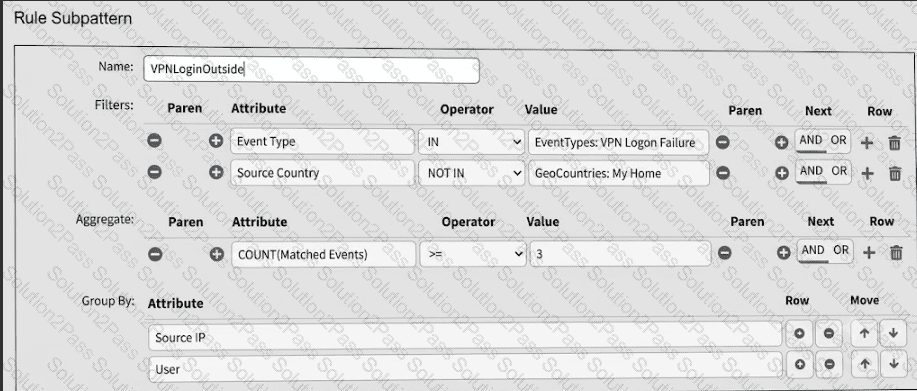
What is this rule attempting to match? (Choose one answer)