NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Fortinet NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Refer to the exhibit.
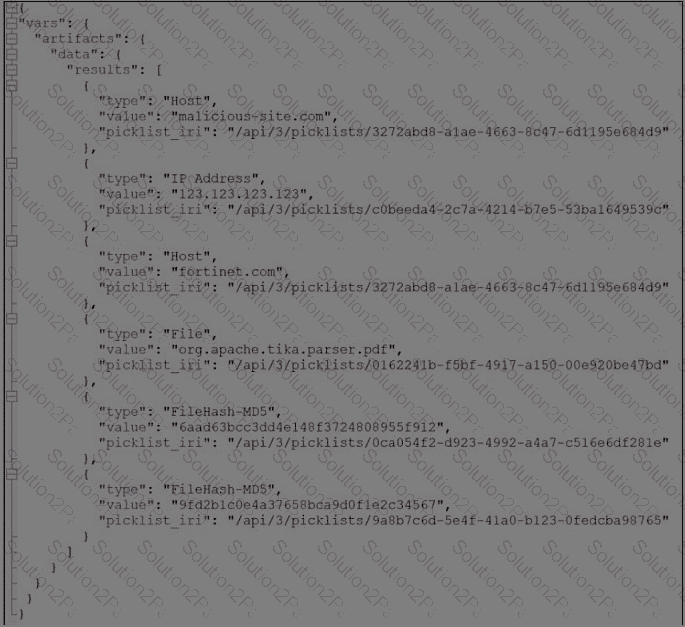
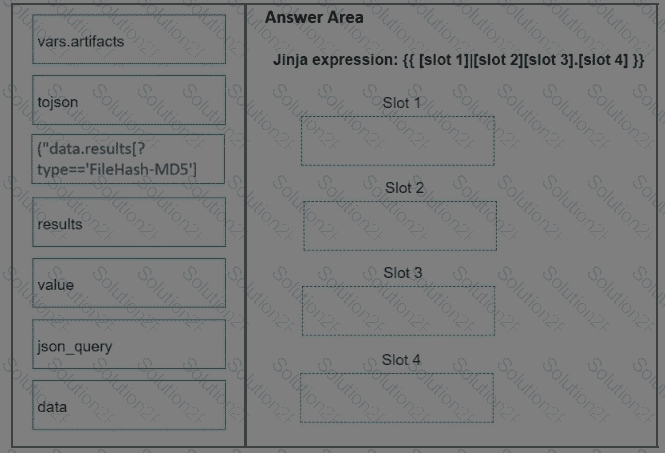
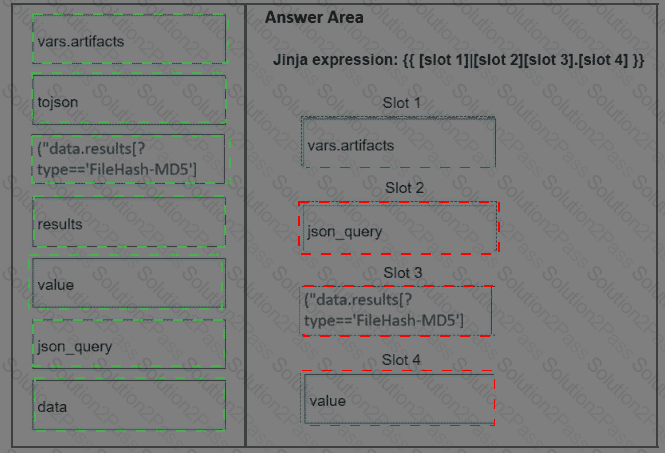
What is the correct Jinja expression to filter the results to show only the MD5 hash values?
{{ [slot 1]|[slot 2] [slot 3].[slot 4] }}
Select the jinja expression in the left column, hold and drag it to a blank position on the right. Place the four correct steps in order, placing the first
step in the first slot. Once you place an expression, you can move it again if you want to change your answer before moving to the next question. You
need to drop four jinja expressions in the work area.
Select and drag the screen divider to change the viewable area of the source and work areas.
Refer to the exhibits.
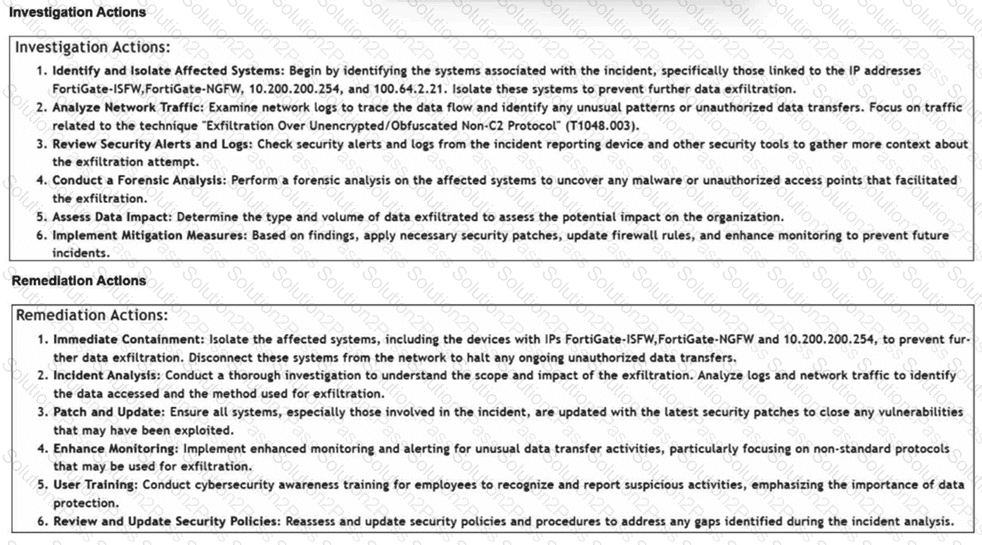
How is the investigation and remediation output generated on FortiSIEM? (Choose one answer)
Refer to the exhibit.
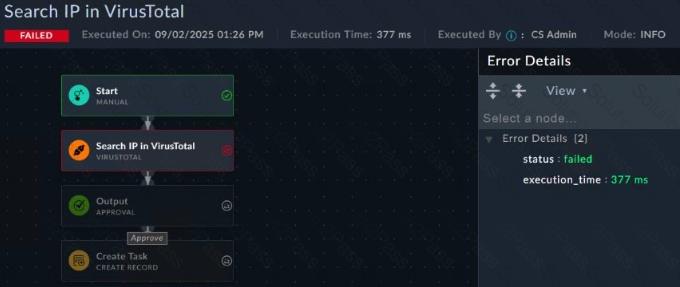
You created a new playbook and executed it as a test. However, it failed to run. You want to investigate, but you do not see details about the error. What is the reason for the lack of details?
Which two statements accurately describe the Custom API Endpoint playbook trigger? Choose two answers.
Refer to Exhibits:
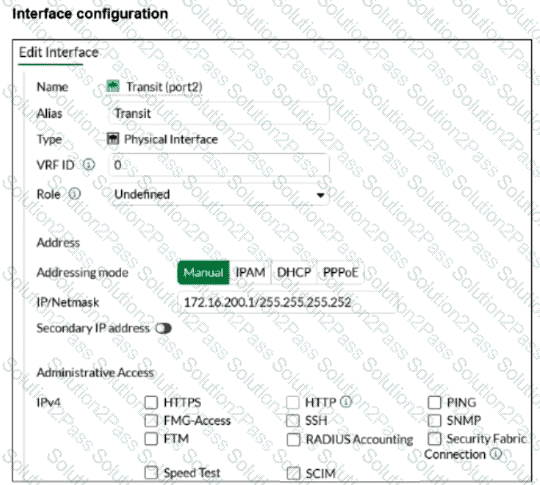
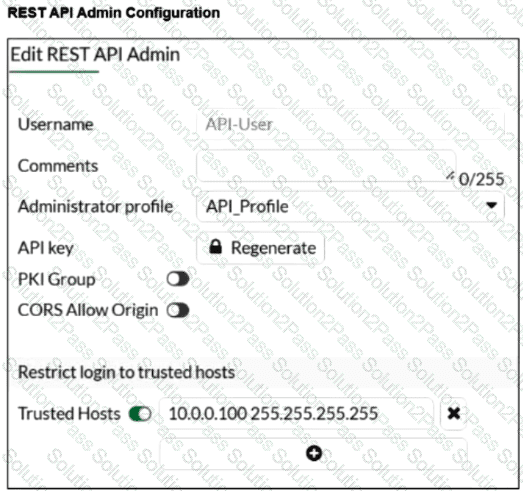
You configured the FortiGate connector on FortiSOAR. You want to allow FortiSOAR 10.200.200.160 to perform actions on FortiGate 172.16.200.1. However, the connection attempt fails. Assume that the FortiGate connector is configured correctly on the FortiSOAR side.
Which two configurations are required on FortiGate? Choose two answers.
When you use a manual trigger to save user input as a variable, what is the correct Jinja expression to reference the variable? (Choose one answer)
While monitoring your network, you discover that one FortiGate device is sending significantly more logs to FortiAnalyzer than all of the other FortiGate devices in the topology.
Additionally, the ADOM that the FortiGate devices are registered to consistently exceeds its quota.
What are two possible solutions? (Choose two.)
Review the incident report:
An attacker identified employee names, roles, and email patterns from public press releases, which were then used to craft tailored emails.
The emails were directed to recipients to review an attached agenda using a link hosted off the corporate domain.
Which two MITRE ATT & CK tactics best fit this report? (Choose two answers)
Which three end user logs does FortiAnalyzer use to identify possible IOC compromised hosts? (Choose three.)
Refer to the exhibit.
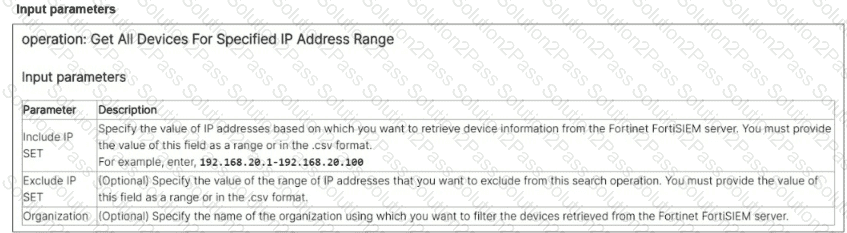
A list of FortiSIEM connector actions is shown. You want to create a playbook on FortiSOAR that allows you to accomplish the following:
Manually input a range of IP addresses.
Use the connector action in the exhibit to retrieve a list of devices from the FortiSIEM configuration management database (CMDB) within that IP address range.
For each returned result, create an asset record based on the IP address of the device.
Which combination and order of step operations fulfills the requirements with the fewest required playbook steps?
Which three end user logs does FortiAnalyzer use to identify possible IOC compromised hosts? (Choose three answers)
Refer to the exhibit.
Assume that all devices in the FortiAnalyzer Fabric are shown in the image.
Which two statements about the FortiAnalyzer Fabric deployment are true? (Choose two.)
Review the incident report. A fake HR login page was sent to several employees through email. The page copied the company’s branding and captured usernames and passwords. The attacker later used the stolen credentials to sign in through the company’s web VPN. Which two MITRE ATT & CK tactics best characterize this report? Choose two answers.
You configured a new module named Users. Next, you want to configure a playbook that creates users from ingested data. When new records are created, you want to ensure that duplicate users do not overwrite existing user records and their fields. However, you also want the playbook to continue running even if duplicates are encountered so that any non-duplicate records are still created. Which two actions fulfill the requirements? Choose two answers.
Which three are threat hunting activities? (Choose three answers)
Refer to the exhibit.
Which two options describe how the Update Asset and Identity Database playbook is configured? (Choose two.)
You wish to use FortiAI to help you design playbooks. Which two configurations on FortiSOAR are required? Choose two answers.
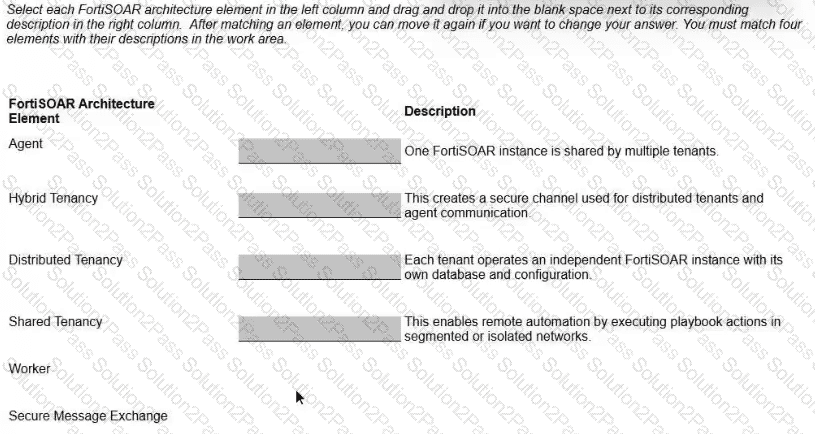
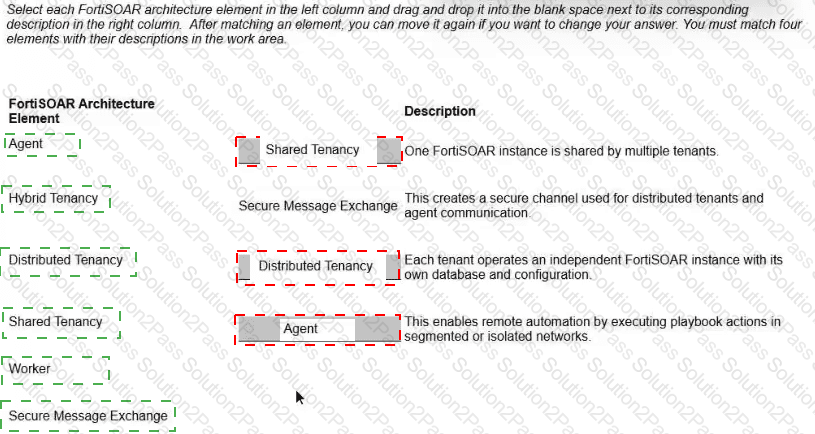
Match the FortiSOAR architecture element to its description.
Select each FortiSOAR architecture element in the left column and drag and drop it into the blank space next to its corresponding description in the right column. After matching an element, you can move it again if you want to change your answer. You must match four elements with their descriptions in the work area.
Which two statements about the FortiAnalyzer Fabric topology are true? (Choose two.)
Which role does a threat hunter play within a SOC?
