Winter Sale Special - Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: xmaspas7

Easiest Solution 2 Pass Your Certification Exams

Professional-Cloud-Architect Google Certified Professional - Cloud Architect (GCP) Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Google Professional-Cloud-Architect Google Certified Professional - Cloud Architect (GCP) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

You have an application deployed on Kubernetes Engine using a Deployment named echo-deployment. The deployment is exposed using a Service called echo-service. You need to perform an update to the application with minimal downtime to the application. What should you do?

A.

Use kubect1 set image deployment/echo-deployment < new-image >

B.

Use the rolling update functionality of the Instance Group behind the Kubernetes cluster

C.

Update the deployment yaml file with the new container image. Use kubect1 delete deployment/

echo-deployment and kubect1 create –f < yaml-file >

D.

Update the service yaml file which the new container image. Use kubect1 delete service/echoservice

and kubect1 create –f < yaml-file >

You are designing the architecture for a stateless, public-facing, containerized web application. The marketing department uses this web application to run unpredictable flash sales that cause sudden, massive spikes in user traffic. The application is a critical revenue driver and must always be available and responsive to users. Your design must automatically handle high traffic fluctuations and allow for new application versions to be deployed with zero downtime and a safe, fast rollback capability. What should you do?

A.

Deploy the application to a regional Managed Instance Group (MIG). Configure a CPU-based autoscaling policy and use the MIG ' s rolling update feature for deployments.

B.

Deploy the application as a Cloud Run service. Configure request-based auto-scaling and use gradual rollouts by splitting traffic between revisions.

C.

Deploy the application to a single, large Compute Engine instance and use a startup script to pull and run the latest container image on boot.

D.

Deploy the application to a Google Kubernetes Engine (GKE) cluster. Use the Recreate deployment strategy to roll out new application versions.

Your company is building a new architecture to support its data-centric business focus. You are responsible for setting up the network. Your company’s mobile and web-facing applications will be deployed on-premises, and all data analysis will be conducted in GCP. The plan is to process and load 7 years of archived .csv files totaling 900 TB of data and then continue loading 10 TB of data daily. You currently have an existing 100-MB internet connection.

What actions will meet your company’s needs?

A.

Compress and upload both achieved files and files uploaded daily using the qsutil –m option.

B.

Lease a Transfer Appliance, upload archived files to it, and send it, and send it to Google to transfer

archived data to Cloud Storage. Establish a connection with Google using a Dedicated Interconnect or

Direct Peering connection and use it to upload files daily.

C.

Lease a Transfer Appliance, upload archived files to it, and send it, and send it to Google to transfer

archived data to Cloud Storage. Establish one Cloud VPN Tunnel to VPC networks over the public internet, and compares and upload files daily using the gsutil –m option.

D.

Lease a Transfer Appliance, upload archived files to it, and send it to Google to transfer archived data to Cloud Storage. Establish a Cloud VPN Tunnel to VPC networks over the public internet, and compress and upload files daily.

You are a cloud architect for a global financial services company. Your primary production environment is in a VPC network in Google Cloud. Your company also operates a secondary VPC network in Google Cloud and a separate, smaller analytics workload in another major cloud provider. You need to design a network architecture that provides reliable, high-bandwidth connectivity between all three environments. Your goal is to use Google ' s private backbone as much as possible for all intercloud and inter-VPC traffic to ensure low latency and simplify network management. What should you do?

A.

Configure Cross-Cloud Interconnect to connect your primary VPC network to the other cloud provider ' s VPC. Configure Network Connectivity Center in your primary Google Cloud project. Create spokes for the Cross-Cloud Interconnect connection and the secondary VPC network.

B.

Establish a Dedicated Interconnect connection with a 99.99% SLA to the other cloud provider. Use VPC Network Peering to connect the primary and secondary VPC networks. Configure BGP sessions to exchange routes.

C.

Create dedicated HA VPN tunnels from your primary VPC network to both the secondary VPC network and the other cloud provider ' s VPC. Configure dynamic routing with Cloud Router to manage traffic between the environments.

D.

Configure VPC Network Peering between the primary and secondary VPC networks. Establish a Cross-Cloud Interconnect connection from the primary VPC network to the other cloud provider ' s VPC. Configure routes to direct traffic from the secondary VPC network through the primary VPC to the other cloud.

You are developing a retail application on Vertex AI that uses a large language model to give customers real-time product recommendations. The app uses text, code, images, audio, and video prompts to communicate with customers. You need to minimize the application ' s latency to ensure a responsive and delightful user experience. What should you do?

A.

Enable streaming responses from the model to process the output in real time.

B.

Increase the temperature parameter.

C.

Avoid using the max_output_tokens parameter to prevent overly long responses.

D.

Avoid using system instructions to prevent overly long responses.

Your company has a networking team and a development team. The development team runs applications on Compute Engine instances that contain sensitive data. The development team requires administrative permissions for Compute Engine. Your company requires all network resources to be managed by the networking team. The development team does not want the networking team to have access to the sensitive data on the instances. What should you do?

A.

1. Create a project with a standalone VPC and assign the Network Admin role to the networking team.

2. Create a second project with a standalone VPC and assign the Compute Admin role to the development team.

3. Use Cloud VPN to join the two VPCs.

B.

1. Create a project with a standalone Virtual Private Cloud (VPC), assign the Network Admin role to the networking team, and assign the Compute Admin role to the development team.

C.

1. Create a project with a Shared VPC and assign the Network Admin role to the networking team.

2. Create a second project without a VPC, configure it as a Shared VPC service project, and assign the Compute Admin role to the development team.

D.

1. Create a project with a standalone VPC and assign the Network Admin role to the networking team.

2. Create a second project with a standalone VPC and assign the Compute Admin role to the development team.

3. Use VPC Peering to join the two VPCs.

You are the cloud architect for a team developing a new application that integrates with the Gemini API. You observe a sudden, massive spike in API costs and usage. An investigation reveals that a developer accidentally committed a service account key with Gemini API access to a public GitHub repository, and a malicious actor is using it. The on-call SRE immediately disabled the key, stopping the unauthorized usage. Your responsibility is to lead the post-incident review to prevent future credential leaks. What should you do?

A.

Initiate a formal disciplinary review for the developer who committed the key. Mandate that all future pull requests must be manually approved by a security team member before being merged.

B.

Immediately migrate all applications to use Workload Identity Federation to access Google Cloud APIs from GitHub Actions, eliminating all service account keys from your CI/CD process.

C.

Write a report detailing the financial impact of the unauthorized use of the service account key. Work with the finance department to track the costs and create a policy to bill the responsible team for any future cost overruns caused by credential leaks.

D.

Schedule a blameless postmortem with the engineering team to map the incident timeline. Collaboratively identify gaps in the development workflow, and assign action items to implement automated pre-commit hooks and a CI/CD pipeline stage for secret scanning.

For this question, refer to the TerramEarth case study

You analyzed TerramEarth ' s business requirement to reduce downtime, and found that they can achieve a majority of time saving by reducing customers ' wait time for parts You decided to focus on reduction of the 3 weeks aggregate reporting time Which modifications to the company ' s processes should you recommend?

A.

Migrate from CSV to binary format, migrate from FTP to SFTP transport, and develop machine learning analysis of metrics.

B.

Migrate from FTP to streaming transport, migrate from CSV to binary format, and develop machine learning analysis of metrics.

C.

Increase fleet cellular connectivity to 80%, migrate from FTP to streaming transport, and develop machine learning analysis of metrics.

D.

Migrate from FTP to SFTP transport, develop machine learning analysis of metrics, and increase dealer local inventory by a fixed factor.

For this question, refer to the Dress4Win case study. Dress4Win is expected to grow to 10 times its size in 1 year with a corresponding growth in data and traffic that mirrors the existing patterns of usage. The CIO has set the target of migrating production infrastructure to the cloud within the next 6 months. How will you configure the solution to scale for this growth without making major application changes and still maximize the ROI?

A.

Migrate the web application layer to App Engine, and MySQL to Cloud Datastore, and NAS to Cloud Storage. Deploy RabbitMQ, and deploy Hadoop servers using Deployment Manager.

B.

Migrate RabbitMQ to Cloud Pub/Sub, Hadoop to BigQuery, and NAS to Compute Engine with Persistent Disk storage. Deploy Tomcat, and deploy Nginx using Deployment Manager.

C.

Implement managed instance groups for Tomcat and Nginx. Migrate MySQL to Cloud SQL, RabbitMQ to Cloud Pub/Sub, Hadoop to Cloud Dataproc, and NAS to Compute Engine with Persistent Disk storage.

D.

Implement managed instance groups for the Tomcat and Nginx. Migrate MySQL to Cloud SQL, RabbitMQ to Cloud Pub/Sub, Hadoop to Cloud Dataproc, and NAS to Cloud Storage.

For this question, refer to the Dress4Win case study. Which of the compute services should be migrated as –is and would still be an optimized architecture for performance in the cloud?

A.

Web applications deployed using App Engine standard environment

B.

RabbitMQ deployed using an unmanaged instance group

C.

Hadoop/Spark deployed using Cloud Dataproc Regional in High Availability mode

D.

Jenkins, monitoring, bastion hosts, security scanners services deployed on custom machine types

For this question, refer to the Dress4Win case study. Considering the given business requirements, how would you automate the deployment of web and transactional data layers?

A.

Deploy Nginx and Tomcat using Cloud Deployment Manager to Compute Engine. Deploy a Cloud SQL server to replace MySQL. Deploy Jenkins using Cloud Deployment Manager.

B.

Deploy Nginx and Tomcat using Cloud Launcher. Deploy a MySQL server using Cloud Launcher. Deploy Jenkins to Compute Engine using Cloud Deployment Manager scripts.

C.

Migrate Nginx and Tomcat to App Engine. Deploy a Cloud Datastore server to replace the MySQL server in a high-availability configuration. Deploy Jenkins to Compute Engine using Cloud Launcher.

D.

Migrate Nginx and Tomcat to App Engine. Deploy a MySQL server using Cloud Launcher. Deploy Jenkins to Compute Engine using Cloud Launcher.

For this question, refer to the TerramEarth case study

Your development team has created a structured API to retrieve vehicle data. They want to allow third parties to develop tools for dealerships that use this vehicle event data. You want to support delegated authorization against this data. What should you do?

A.

Build or leverage an OAuth-compatible access control system.

B.

Build SAML 2.0 SSO compatibility into your authentication system.

C.

Restrict data access based on the source IP address of the partner systems.

D.

Create secondary credentials for each dealer that can be given to the trusted third party.

For this question, refer to the TerramEarth case study.

To speed up data retrieval, more vehicles will be upgraded to cellular connections and be able to transmit data to the ETL process. The current FTP process is error-prone and restarts the data transfer from the start of the file when connections fail, which happens often. You want to improve the reliability of the solution and minimize data transfer time on the cellular connections. What should you do?

A.

Use one Google Container Engine cluster of FTP servers. Save the data to a Multi-Regional bucket. Run the ETL process using data in the bucket.

B.

Use multiple Google Container Engine clusters running FTP servers located in different regions. Save the data to Multi-Regional buckets in us, eu, and asia. Run the ETL process using the data in the bucket.

C.

Directly transfer the files to different Google Cloud Multi-Regional Storage bucket locations in us, eu, and asia using Google APIs over HTTP(S). Run the ETL process using the data in the bucket.

D.

Directly transfer the files to a different Google Cloud Regional Storage bucket location in us, eu, and asia using Google APIs over HTTP(S). Run the ETL process to retrieve the data from each Regional bucket.

For this question refer to the TerramEarth case study

Operational parameters such as oil pressure are adjustable on each of TerramEarth ' s vehicles to increase their efficiency, depending on their environmental conditions. Your primary goal is to increase the operating efficiency of all 20 million cellular and unconnected vehicles in the field How can you accomplish this goal?

A.

Have your engineers inspect the data for patterns, and then create an algorithm with rules that make operational adjustments automatically.

B.

Capture all operating data, train machine learning models that identify ideal operations, and run locally to make operational adjustments automatically.

C.

Implement a Google Cloud Dataflow streaming job with a sliding window, and use Google Cloud Messaging (GCM) to make operational adjustments automatically.

D.

Capture all operating data, train machine learning models that identify ideal operations, and host in Google Cloud Machine Learning (ML) Platform to make operational adjustments automatically.

Your agricultural division is experimenting with fully autonomous vehicles.

You want your architecture to promote strong security during vehicle operation.

Which two architecture should you consider?

Choose 2 answers:

A.

Treat every micro service call between modules on the vehicle as untrusted.

B.

Require IPv6 for connectivity to ensure a secure address space.

C.

Use a trusted platform module (TPM) and verify firmware and binaries on boot.

D.

Use a functional programming language to isolate code execution cycles.

E.

Use multiple connectivity subsystems for redundancy.

F.

Enclose the vehicle ' s drive electronics in a Faraday cage to isolate chips.

For this question, refer to the TerramEarth case study.

The TerramEarth development team wants to create an API to meet the company ' s business requirements. You want the development team to focus their development effort on business value versus creating a custom framework. Which method should they use?

A.

Use Google App Engine with Google Cloud Endpoints. Focus on an API for dealers and partners.

B.

Use Google App Engine with a JAX-RS Jersey Java-based framework. Focus on an API for the public.

C.

Use Google App Engine with the Swagger (open API Specification) framework. Focus on an API for the public.

D.

Use Google Container Engine with a Django Python container. Focus on an API for the public.

E.

Use Google Container Engine with a Tomcat container with the Swagger (Open API Specification) framework. Focus on an API for dealers and partners.

For this question refer to the TerramEarth case study.

Which of TerramEarth ' s legacy enterprise processes will experience significant change as a result of increased Google Cloud Platform adoption.

A.

Opex/capex allocation, LAN changes, capacity planning

B.

Capacity planning, TCO calculations, opex/capex allocation

C.

Capacity planning, utilization measurement, data center expansion

D.

Data Center expansion, TCO calculations, utilization measurement

For this question, refer to the TerramEarth case study.

TerramEarth ' s CTO wants to use the raw data from connected vehicles to help identify approximately when a vehicle in the development team to focus their failure. You want to allow analysts to centrally query the vehicle data. Which architecture should you recommend?

A)
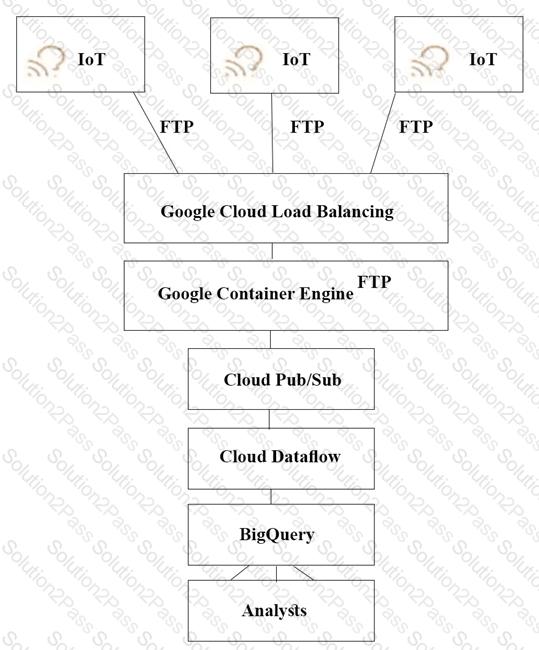
B)
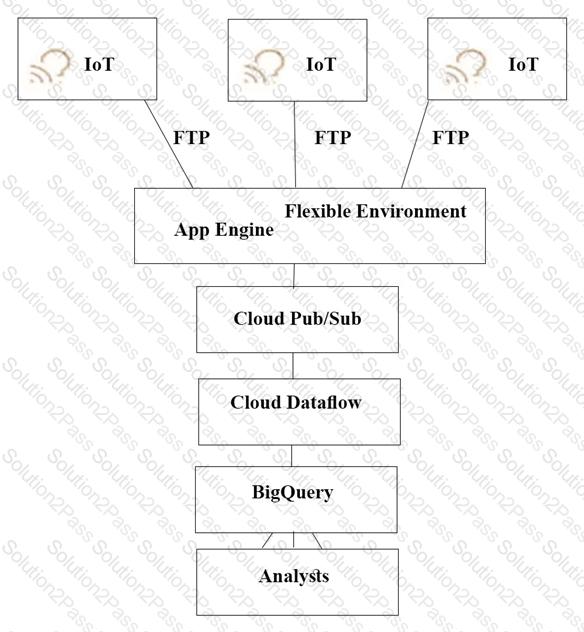
C)
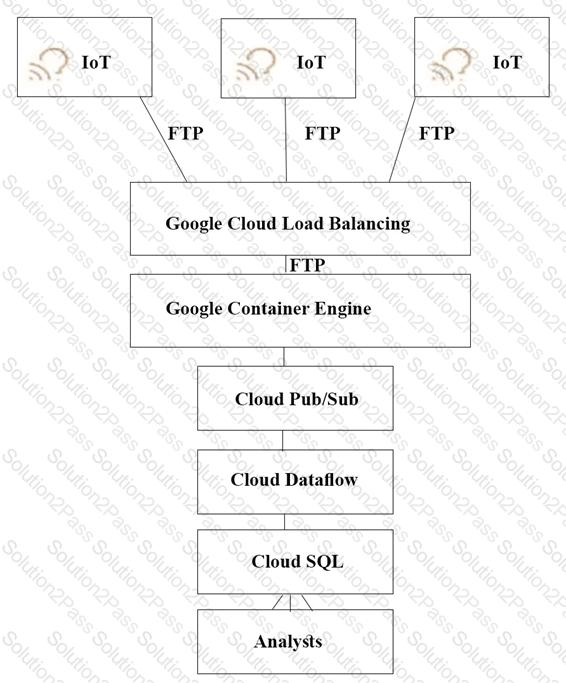
D)
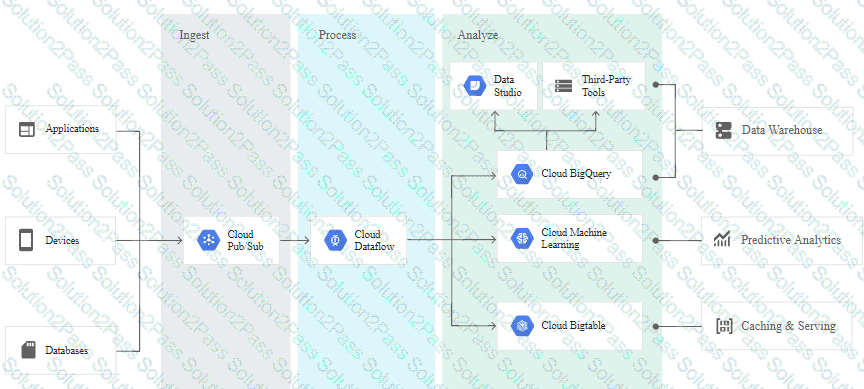
A.

Option A

B.

Option B

C.

Option C

D.

Option D

For this question, refer to the EHR Healthcare case study. You are responsible for ensuring that EHR ' s use of Google Cloud will pass an upcoming privacy compliance audit. What should you do? (Choose two.)

A.

Verify EHR ' s product usage against the list of compliant products on the Google Cloud compliance page.

B.

Advise EHR to execute a Business Associate Agreement (BAA) with Google Cloud.

C.

Use Firebase Authentication for EHR ' s user facing applications.

D.

Implement Prometheus to detect and prevent security breaches on EHR ' s web-based applications.

E.

Use GKE private clusters for all Kubernetes workloads.

For this question, refer to the EHR Healthcare case study. You need to define the technical architecture for securely deploying workloads to Google Cloud. You also need to ensure that only verified containers are deployed using Google Cloud services. What should you do? (Choose two.)

A.

Enable Binary Authorization on GKE, and sign containers as part of a CI/CD pipeline.

B.

Configure Jenkins to utilize Kritis to cryptographically sign a container as part of a CI/CD pipeline.

C.

Configure Container Registry to only allow trusted service accounts to create and deploy containers from the registry.

D.

Configure Container Registry to use vulnerability scanning to confirm that there are no vulnerabilities before deploying the workload.

Copyright © 2014-2026 Solution2Pass. All Rights Reserved