300-710 Cisco Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Cisco 300-710 Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
An organization is configuring a new Cisco Firepower High Availability deployment. Which actionmust be taken to ensure that failover is as seamless as possible to end users?
An engineer must change the mode of a Cisco Secure Firewall Threat Defense (FTD) firewall in the Cisco Secure Firewall Management Center (FMC) inventory. The engineer must take these actions:
• Register Secure FTD with Secure FMC.
• Change the firewall mode.
• Deregister the Secure FTD device from Secure FMC.
How must the engineer take FTD take the actions?
Encrypted Visibility Engine (EVE) is enabled under which lab on an access control policy in Cisco Secure Firewall Management Centre?
Which limitation applies to Cisco Firepower Management Center dashboards in a multidomain environment?
An engineer must configure an ERSPAN passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:
Configure the passive interface.
Configure the ERSPAN IP address.
Which two additional settings must be configured to complete the configuration? (Choose two.)
When using Cisco Threat Response, which phase of the Intelligence Cycle publishes the results of the investigation?
In which two places can thresholding settings be configured? (Choose two.)
An engineer must deploy URL filtering in Cisco Secure Firewall Management Center Version 7.0. The engineer is configuring a URL condition for an access control rule to filter websites that display bad behavior or are malicious or undesirable. Which reputation level must be configured?
An engineer has been tasked with providing disaster recovery for an organization ' s primary Cisco FMC. What must be done on the primary and secondary Cisco FMCs to ensure that a copy of the original corporate policy is available if the primary Cisco FMC fails?
Which Firepower feature allows users to configure bridges in routed mode and enables devices to perform Layer 2 switching between interfaces?
A network engineer is logged into the Cisco AMP for Endpoints console and sees a malicious verdict for an identified SHA-256 hash. Which configuration is needed to mitigate this threat?
A mid-sized company is experiencing higher network bandwidth utilization due to a recent acquisition The network operations team is asked to scale up their one Cisco FTD appliance deployment to higher capacities due to the increased network bandwidth. Which design option should be used to accomplish this goal?
Which two considerations must be made when deleting and re-adding devices while managing them via Cisco FMC (Choose two).
Refer to the exhibit.
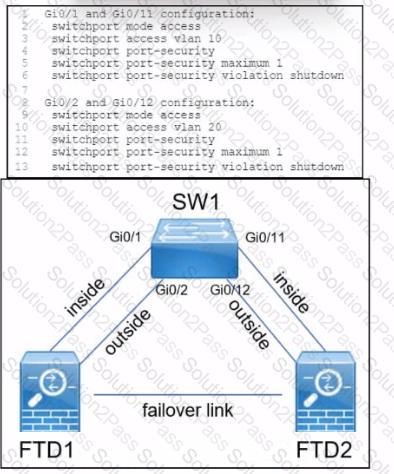
A company is deploying a pair of Cisco Secure Firewall Threat defence devices named FTD1 and FTD2. FTD1 and FTD2 have been configured as an active/standby pair with a failover link but without a stateful link. What must be implemented next to ensure that users on the internal network still communicate with outside devices if FTD1 fails?
A security administrator must configure Cisco Secure Firewall Management Center so that certain intrusion rules are active only during specified times. Which action must the administrator take?
A network engineer wants to disable the HTTP response page and interactive blocking of the entire access control policy in Cisco Secure Firewall Management Center. What must be
selected in Block Response Page and Interactive Block Response Page?
A network administrator configured an access control rule named WEB05405_SRV06798_ALLOW that allows any source on the Internet to reach the public IP address of a web server on port 8080. The administrator also configured a NAT policy that translates the public IP address to the internal web server IP address. During testing, the web server is not reachable from the Internet on port 8080. Which configuration must the administrator apply to resolve the issue?
Refer to the exhibit.
What must be done to fix access to this website while preventing the same communication to all other websites?
What are two application layer preprocessors? (Choose two.)
Which firewall design allows a firewall to forward traffic at layer 2 and layer 3 for the same subnet?
