Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

300-710 Cisco Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Cisco 300-710 Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 2 / 7
Total 444 questions

Which firewall design will allow It to forward traffic at layers 2 and 3 for the same subnet?

A.

Cisco Firepower Threat Defense mode

B.

routed mode

C.

Integrated routing and bridging

D.

transparent mode

A network security engineer must replace a faulty Cisco FTD device in a high availability pair. Which action must be taken while replacing the faulty unit?

A.

Shut down the Cisco FMC before powering up the replacement unit.

B.

Ensure that the faulty Cisco FTD device remains registered to the Cisco FMC.

C.

Unregister the faulty Cisco FTD device from the Cisco FMC

D.

Shut down the active Cisco FTD device before powering up the replacement unit.

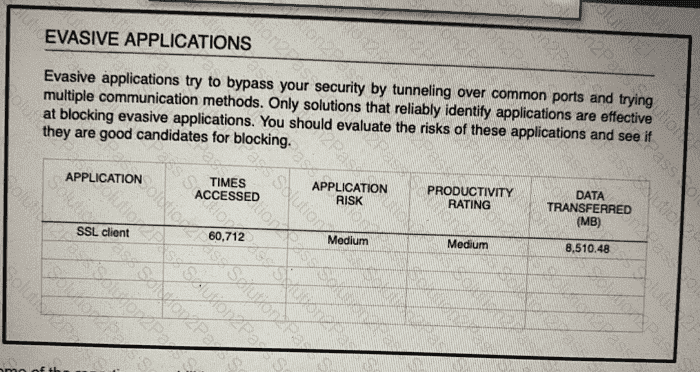
Refer to the exhibit.

An administrator is looking at some of the reporting capabilities for Cisco Firepower and noticed this section of the Network Risk report showing a lot of SSL activity that cloud be used for evasion. Which action will mitigate this risk?

A.

Use SSL decryption to analyze the packets.

B.

Use encrypted traffic analytics to detect attacks

C.

Use Cisco AMP for Endpoints to block all SSL connection

D.

Use Cisco Tetration to track SSL connections to servers.

An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration tasks must be performed to achieve this file lookup? (Choose two).

A.

The Cisco FMC needs to include a SSL decryption policy.

B.

The Cisco FMC needs to connect to the Cisco AMP for Endpoints service.

C.

The Cisco FMC needs to connect to the Cisco ThreatGrid service directly for sandboxing.

D.

The Cisco FMC needs to connect with the FireAMP Cloud.

E.

The Cisco FMC needs to include a file inspection policy for malware lookup.

A network engineer is logged into the Cisco AMP for Endpoints console and sees a malicious verdict for an identified SHA-256 hash. Which configuration is needed to mitigate this threat?

A.

Use regular expressions to block the malicious file.

B.

Add the hash from the infected endpoint to the network block list.

C.

Add the hash to the simple custom detection list.

D.

Enable a personal firewall in the infected endpoint.

An administrator configures a Cisco Secure Firewall Threat Defense device in transparent mode. To configure the BVI (Bridge Virtual Interface), the administrator must:

Add a bridge-group interface

Configure a bridge-group ID

Configure the bridge-group interface description

Add bridge-group member interfaces

How must the engineer perform these actions?

A.

Configure a name for the bridge-group interface

B.

Set a security zone for the bridge-group interface

C.

Set the bridge-group interface mode to transparent

D.

Configure an IP address for the bridge-group interface

Which two statements about deleting and re-adding a device to Cisco FMC are true? (Choose two.)

A.

An option to re-apply NAT and VPN policies during registration is available, so users do not need to re- apply the policies after registration is completed.

B.

Before re-adding the device in Cisco FMC, you must add the manager back in the device.

C.

No option to delete and re-add a device is available in the Cisco FMC web interface.

D.

The Cisco FMC web interface prompts users to re-apply access control policies.

E.

No option to re-apply NAT and VPN policies during registration is available, so users need to re-apply the policies after registration is completed.

In which two ways do access control policies operate on a Cisco Firepower system? (Choose two.)

A.

Traffic inspection can be interrupted temporarily when configuration changes are deployed.

B.

The system performs intrusion inspection followed by file inspection.

C.

They can block traffic based on Security Intelligence data.

D.

File policies use an associated variable set to perform intrusion prevention.

E.

The system performs a preliminary inspection on trusted traffic to validate that it matches the trusted parameters.

What is needed to start a threat investigation in Cisco XDR?

A.

indicator of compromise

B.

local IP address

C.

user name

D.

indicator of attack

A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface. What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?

A.

Only the UDP packet type is supported.

B.

The output format option for the packet logs is unavailable.

C.

The destination MAC address is optional if a VLAN ID value is entered.

D.

The VLAN ID and destination MAC address are optional.

An engineer is configuring Cisco Security Devices by using Cisco Secure Firewall Management Center. Which configuration command must be run to compare the CA certificate bundle on the local system to the latest CA bundle from the Cisco server?

A.

configure cert-update compare

B.

configure cert-update auto-update enable

C.

configure cert-update run-now

D.

configure cert-update test

Refer to the exhibit.

An engineer is modifying an access control policy to add a rule to Inspect all DNS traffic that passes it making the change and deploying the policy, they see that DNS traffic Is not being Inspected by the Snort engine. What is......

A.

The action of the rule is set to trust instead of allow.

B.

The rule must specify the security zone that originates the traffic.

C.

The rule Is configured with the wrong setting for the source port.

D.

The rule must define the source network for inspection as well as the port.

Which Cisco Rapid Threat Containment mitigation action is enabled by integrating pxGrid Adaptive Network Control with Cisco ISE and Cisco Secure Firewall Management Center?

A.

Block

B.

Terminate

C.

Suspend

D.

Reject

An engineer is implementing clustering in Cisco Secure Firewall Management Center. The configuration must ensure that the cluster has a designated control node with more resources than the other nodes. What must the engineer set for the priority value of that node?

A.

0

B.

A value lower than the values assigned to the other nodes in the cluster

C.

A value higher than the values assigned to the other nodes in the cluster

D.

255

What must be implemented on Cisco Firepower to allow multiple logical devices on a single physical device to have access to external hosts?

A.

Add at least two container instances from the same module.

B.

Set up a cluster control link between all logical devices

C.

Add one shared management interface on all logical devices.

D.

Define VLAN subinterfaces for each logical device.

An engineer must permit SSH on the inside interface of a Cisco Secure Firewall Threat Defense device. SSH is currently permitted only on the management interface. Which type of policy

must the engineer configure?

A.

platform policy

B.

access control policy

C.

NAT policy

D.

intrusion policy

With Cisco FTD software, which interface mode must be configured to passively receive traffic that passes through the appliance?

A.

ERSPAN

B.

IPS-only

C.

firewall

D.

tap

A network administrator is configuring an access control policy on a Secure Firewall Threat Defense device. The administrator wants to exclude traffic to a certain banking site from being decrypted. What must the rule include to specify the banking site?

A.

action of trust, specified protocol for SSL, and below the SSL decryption rule

B.

action of deny and for the HTTP and HTTPS access protocols

C.

action of block, specified protocol for SSL, and above the SSL decryption rule

D.

action of trust and above the SSL decryption rule

An engineer is setting up a new Cisco Secure Firewall Threat Defense appliance to replace the current firewall. The company requests that inline sets be used and that when one interface in

an inline set goes down, the second interface in the inline set goes down. What must the engineer configure to meet the deployment requirements?

A.

strict TCP enforcement

B.

propagate link state

C.

Snort fail open

D.

inline tap mode

What is a limitation to consider when running a dynamic routing protocol on a Cisco FTD device in IRB mode?

A.

Only link-stale routing protocols are supported.

B.

Only distance vector routing protocols are supported.

C.

Only EtherChannel interfaces are supposed.

D.

Only nonbridge interfaces are supported.

Page: 2 / 7
Total 444 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved