CS0-004 CompTIA Cybersecurity Analyst CySA+ V4 (New Version) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your CompTIA CS0-004 CompTIA Cybersecurity Analyst CySA+ V4 (New Version) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
An analyst prepares an after action report following an incident in which multiple systems were compromised over several days.
The analyst provides raw event logs from each compromised system in the report and determines that a patient-zero system cannot be found.
Which of the following should the analyst do to determine the patient-zero system?
Which of the following describes the main benefits of MITRE ATT & CK Navigator?
An analyst reviews a summarized vulnerability report through a governance, risk, and compliance (GRC) reporting tool.
The following report correlates asset information from the configuration management database (CMDB) against detected vulnerabilities:
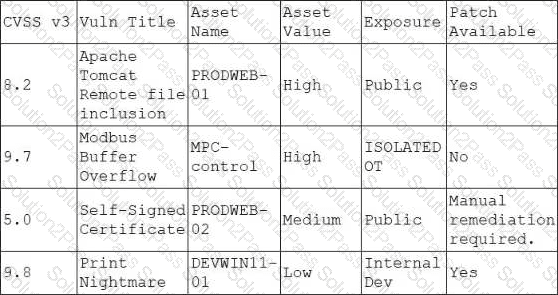
Which of the following servers should the analyst prioritize based on the target value, the risk, and the likelihood of exploitation?
A security analyst isolates a Windows 11 workstation from the network after known malware is detected. The list of security information and event management (SIEM) events during the malware installation and timeline does not identify a specific user who was logged in. The security analyst uses the local administrative account to log in and would like a list of logins to the machine.
Which of the following PowerShell commands should the analyst use?
An analyst reviews the following system logs from a recent breach attempt:
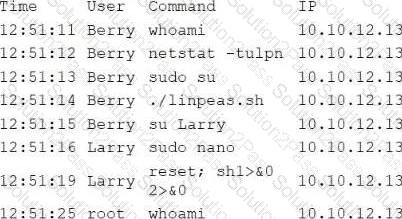
Which of the following techniques did the attacker attempt to use?
A Chief Information Security Officer (CISO) is notified of an ongoing incident.
Which of the following explains why the CISO instructs the Chief Executive Officer not to discuss the incident over email?
The Chief Information Security Officer wants to improve internal security measures by continuously validating and verifying access to the production environment.
Which of the following concepts best describes this practice?
A server was recently compromised. A security analyst needs to collect artifacts for further analysis before disconnecting the server from the network.
Which of the following artifacts should the analyst collect first?
An analyst must provide a visualization of data received from threat intelligence sources. The data includes the Internet Protocols, services, and tools used by threat actors.
Which of the following is the best framework for the analyst to follow to display this data?
Which of the following best explains why sensitive data should be encrypted at rest on laptops?
A vendor releases details of a new vulnerability. When an analyst reviews the scheduled scans, no vulnerabilities are identified. The vulnerability is only discovered after a configuration change.
Which of the following scan types did the analyst configure?
A security analyst reruns infrastructure as code (IaC) to tear down and rebuild a new environment after a ransomware attack.
Which of the following describes this phase?
A new security operations center (SOC) manager joins a team that struggles to meet service-level agreements (SLAs). The alert backlog continues to increase daily.
Which of the following will the manager most likely need to do?
Which of the following is the most comprehensive type of report associated with a closed incident?
Which of the following does a phishing campaign click rate measure?
An analyst receives the following output:
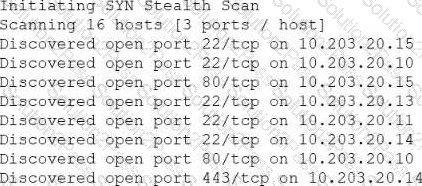
Which of the following is the correct number of discovered systems that are allowing unencrypted traffic?
An analyst is assigned to a new cybersecurity improvement project. The analyst wants to better understand the workflow processes and the skill set of the cybersecurity engineers on this task force. The analyst sets up a recurring, weekly conference call.
Which of the following best describes the purpose for the conference call?
A security operations center (SOC) manager reviews a document signed by the Chief Financial Officer (CFO), the sales director, and a customer to decide whether a contract breach occurred.
Which of the following best describes the document that includes key performance indicators (KPIs)?
Which of the following network architectures would best implement a perimeter-less network topology?
A team lead asks an analyst to integrate multiple security tools to provide an enhanced view into data that is not readily available in the tool console.
Which of the following will best meet this requirement?