Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

NSE5_SSE_AD-7.6 Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Fortinet NSE5_SSE_AD-7.6 Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 1 / 1
Total 50 questions

Which statement about FortiSASE CASB capabilities is true?

A.

FortiSASE provides both API-based CASB and inline CASB

B.

FortiSASE provides only API-based CASB

C.

FortiSASE provides only inline CASB

D.

FortiSASE provides CASB capabilities only through Security Fabric integration

Which FortiSASE feature monitors SaaS application performance and connectivity to points of presence (POPs)?

A.

Operations widgets

B.

FortiView dashboards

C.

Event logs

D.

Digital experience monitoring

Which configuration is a valid use case for FortiSASE features in supporting remote users?

A.

Enabling secure SaaS access through SD-WAN integration, protecting against web-based threats with data loss prevention, and monitoring user connectivity with shadow IT visibility.

B.

Monitoring SaaS application performance, isolating browser sessions for all websites, and integrating with SD-WAN for data loss prevention.

C.

Enabling secure web browsing to protect against threats, providing explicit application access with zero-trust or SD-WAN integration, and addressing shadow IT visibility with data loss prevention.

D.

Providing secure web browsing through remote browser isolation, addressing shadow IT with zero-trust access, and protecting data at rest only.

How does the FortiSASE security dashboard facilitate vulnerability management for FortiClient endpoints? (Choose one answer)

A.

It automatically patches all vulnerabilities without user intervention and does not categorize vulnerabilities by severity.

B.

It shows vulnerabilities only for applications and requires endpoint users to manually check for affected endpoints.

C.

It displays only critical vulnerabilities, requires manual patching for all endpoints, and does not allow viewing of affected endpoints.

D.

It provides a vulnerability summary, identifies affected endpoints, and supports automatic patching for eligible vulnerabilities.

Which secure internet access (SIA) use case minimizes individual endpoint configuration? (Choose one answer)

A.

Agentless remote user internet access

B.

SIA for FortiClient agent remote users

C.

Site-based remote user internet access

D.

SIA using ZTNA

Which two delivery methods are used for installing FortiClient on a user ' s laptop? (Choose two.)

A.

Use zero-touch installation through a third-party application store.

B.

Download the installer directly from the FortiSASE portal.

C.

Send an invitation email to selected users containing links to FortiClient installers.

D.

Configure automatic installation through an API to the user ' s laptop.

You have a FortiGate configuration with three user-defined SD-WAN zones and one or two members in each of these zones. One SD-WAN member is no longer used in health-check and SD-WAN rules. This member is the only member of its zone. You want to delete it.

What happens if you delete the SD-WAN member from the FortiGate GUI?

A.

FortiGate displays an error message. SD-WAN zones must contain at least one member.

B.

FortiGate accepts the deletion and removes static routes as required.

C.

FortiGate accepts the deletion with no further action.

D.

FortiGate accepts the deletion and places the member in the default SD-WAN zone.

Which two statements correctly describe what happens when traffic matches the implicit SD-WAN rule? (Choose two answers)

A.

Traffic is load balanced using the algorithm set for the v4-ecmp-mode setting.

B.

Traffic does not match any of the entries in the policy route table.

C.

FortiGate flags the session with may_dirty and vwl_default.

D.

The traffic is distributed, regardless of weight, through all available static routes.

E.

The session information output displays no SD-WAN service id.

What is a key use case for FortiSASE Secure Internet Access (SIA) in an agentless deployment? (Choose one answer)

A.

It provides secure web browsing by isolating browser sessions and enforcing data loss prevention for temporary employees.

B.

It acts as a secure web gateway (SWG) distributing a PAC file for explicit web proxy use, securing HTTP and HTTPS traffic with a full security stack, and is ideal for unmanaged endpoints like contractors.

C.

It distributes a PAC file to secure non-web traffic protocols and applies antivirus protection only for managed endpoints.

D.

It requires FortiClient endpoints and supports ZTNA tags to secure all network traffic for unmanaged endpoints.

Which authentication method overrides any other previously configured user authentication on FortiSASE?

A.

Local

B.

SSO

C.

RADIUS

D.

MFA

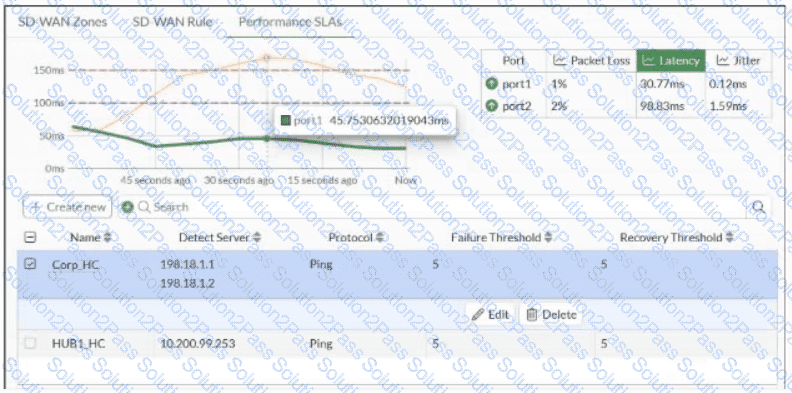
Refer to the exhibit.

Which conclusion can you draw from the exhibit?

A.

Over the past 60 seconds, the member port2 latency was temporarily above the latency criteria defined for HUB1_HC.

B.

The administrator configured the Corp_HC performance service-level agreement (SLA) with SLA targets for the three criteria: packet loss, latency, and jitter.

C.

Over the past 60 seconds, the member port1 was monitored healthy for both latency criteria of the Corp_HC definition.

D.

The administrator configured the packet loss threshold for Corp_HC and HUB1_HC to 5%.

An SD-WAN member is no longer used to steer SD-WAN traffic. You want to update the SD-WAN configuration and delete the unused member.

Which action should you take first? (Choose one answer)

A.

Move the SD-WAN member to the virtual-wan-link zone.

B.

Disable the interface.

C.

Remove the member from the performance service-level agreement (SLA) definitions.

D.

Delete static route definitions for that interface.

For a small site, an administrator plans to implement SD-WAN and ensure high network availability for business-critical applications while limiting the overall cost and the cost of pay-per-use backup connections.

Which action must the administrator take to accomplish this plan?

A.

Use a mid-range FortiGate device to implement standalone SD-WAN.

B.

Implement dynamic routing.

C.

Set up a high availability (HA) cluster to implement standalone SD-WAN.

D.

Configure at least two WAN links.

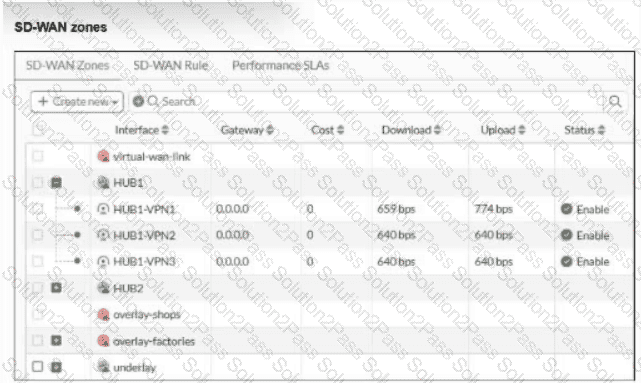
Refer to the exhibit.

An SD-WAN zone configuration on the FortiGate GUI is shown.

What can you conclude about the zone and member configuration on this device?

A.

You can delete the overlay-factories zone.

B.

You can delete the virtual-wan-link zone.

C.

The overlay-factories zone contains no member.

D.

You can move HUB1-VPN3 from the HUB1 zone to the virtual-wan-link zone.

You are configuring SD-WAN to load balance network traffic. Which two facts should you consider when setting up SD-WAN? (Choose two.)
A.

When applicable, FortiGate load balances traffic through all members that meet the SLA target.

B.

SD-WAN load balancing is possible only when using the manual and the best quality strategies.

C.

Only the manual and lowest cost (SLA) strategies allow SD-WAN load balancing.

D.

You can select the outsessions hash mode with all strategies that allow load balancing.

Page: 1 / 1
Total 50 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved