Terraform-Associate-004 HashiCorp Certified: Terraform Associate (004) (HCTA0-004) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your HashiCorp Terraform-Associate-004 HashiCorp Certified: Terraform Associate (004) (HCTA0-004) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
When should you write Terraform configuration files for existing infrastructure that you want to start managing with Terraform?
What is the provider for this resource?
You are updating a child module with the resource block shown in the exhibit below. The public_ip attribute of the resource needs to be accessible to the parent module.
Exhibit:
resource " aws_instance " " example " {
ami = " ami-0a123456789abcdef "
instance_type = " t3.micro "
}
How do you meet this requirement?
You have to initialize a Terraform backend before it can be configured.
You want to create a string that is a combination of a generated random_id and a variable, and reuse that string several times in your configuration.
What is the simplest correct way to implement this without repeating the random_id and variable?
Which of the following locations can Terraform use as aprivate sourcefor modules?(Pick 2 correct responses)
When you initialize Terraform, where does it cache modules from the public Terraform Registry?
What does terraform destroy do?
You are using a networking module in your Terraform configuration with the name label my-network. In your main configuration you have the following code:
When you run terraform validate, you get the following error:
What must you do to successfully retrieve this value from your networking module?
All modules published on the official Terraform Module Registry have been verified by HasihCorp.
Which are forbidden actions when the terraform state file is locked? Choose three correct answers.
Which of the following is not a key principle of infrastructure as code?
Your Terraform configuration manages a resource that requires maximum uptime. You need to update the resource, and when you run terraform plan, Terraform indicates that the update requires the resource to be destroyed and recreated.
Which lifecycle rule can you add to the resource to reduce downtime while still applying the update?
A Terraform backend determines how Terraform loads state and stores updates when you execute which command?
Which of the following is not a benefit of adopting infrastructure as code?
Terraform installs its providers during which phase?
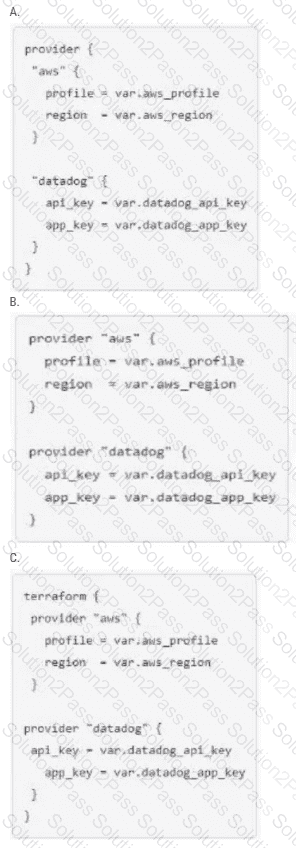
You ate creating a Terraform configuration which needs to make use of multiple providers, one for AWS and one for Datadog. Which of the following provider blocks would allow you to do this?
Which command should you run to check if all code in a Terraform configuration that references multiple modules is properly formatted without making changes?
How could you reference an attribute from the vsphere_datacenter data source for use with the datacenter_id argument within the vsphere_folder resource in the following configuration?
Only the user that generated a terraform plan may apply it.