SC-100 Microsoft Cybersecurity Architect Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Microsoft SC-100 Microsoft Cybersecurity Architect certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
You have a Microsoft 365 tenant. Your company uses a third-party software as a service (SaaS) app named App1. App1 supports authenticating users by using Azure AO credentials. You need to recommend a solution to enable users to authenticate to App1 by using their Azure AD credentials. What should you include in the recommendation?
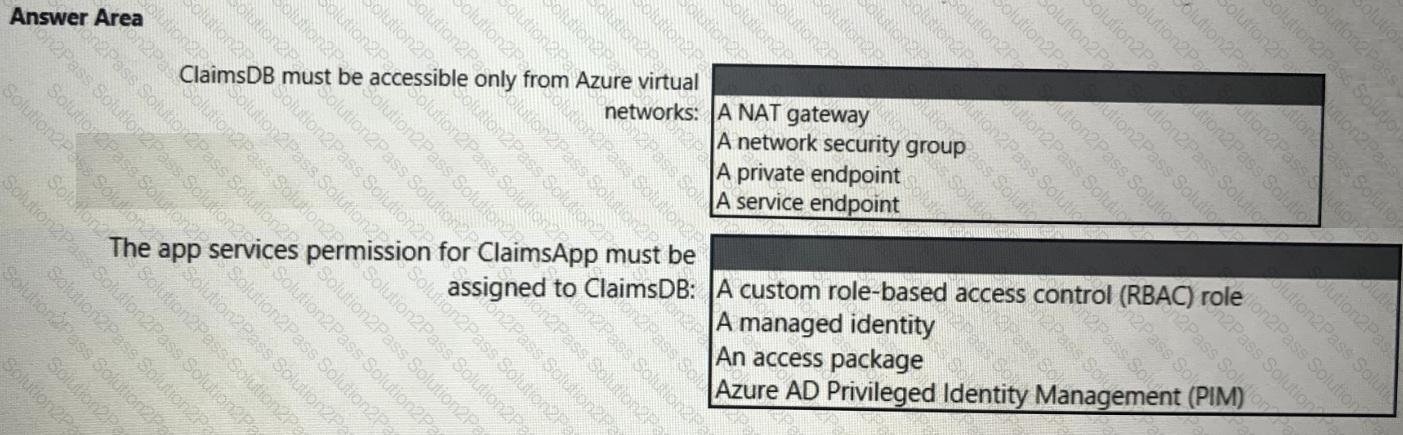
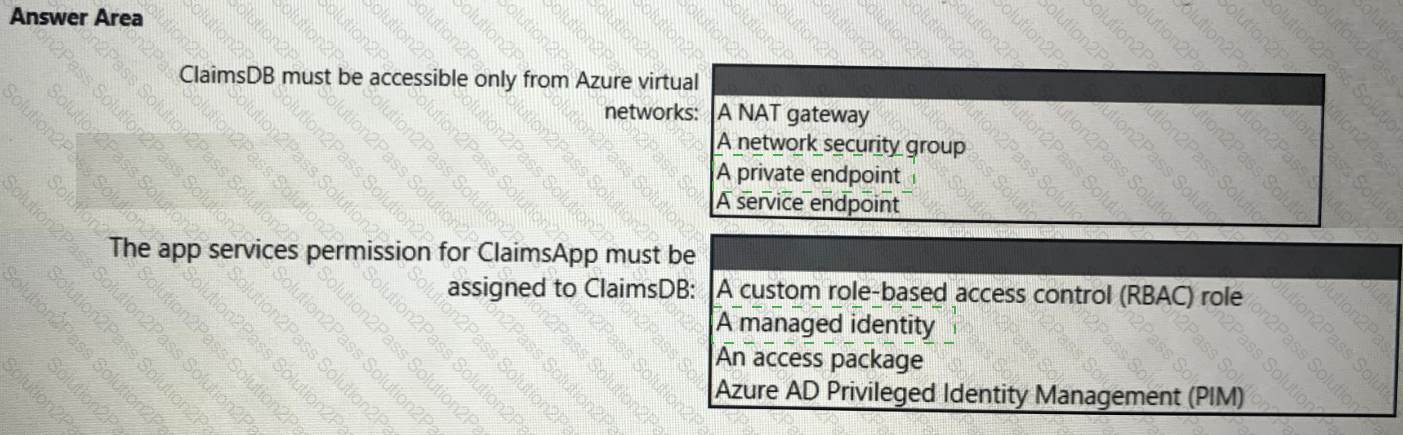
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to recommend a solution to meet the security requirements for the virtual machines.
What should you include in the recommendation?
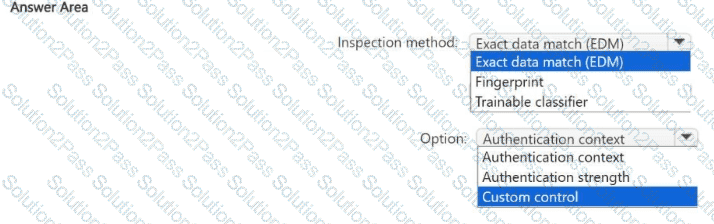
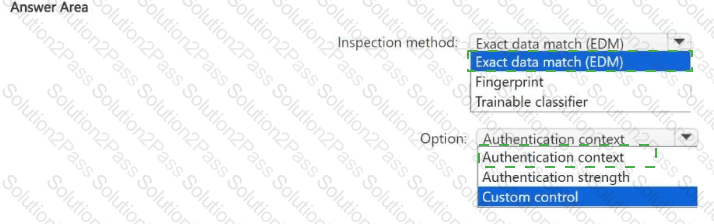
You have a Microsoft 365 subscription that contains a Microsoft SharePoint Online site named Site1. Site1 stores documents that are based on a predefined form and include confidential employee information.
You monitor access to Site1 by using a Microsoft Defender for Cloud Apps session policy.
You need to ensure that step-up authentication is triggered when a user downloads documents that are based on the predefined form. The solution must minimize administrative effort.
Which Microsoft Data Classification Service inspection method should you use, and which Conditional Access option should you add to the session policy? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
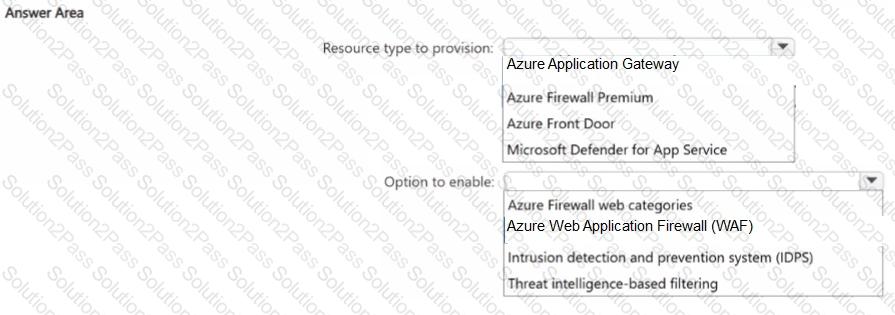
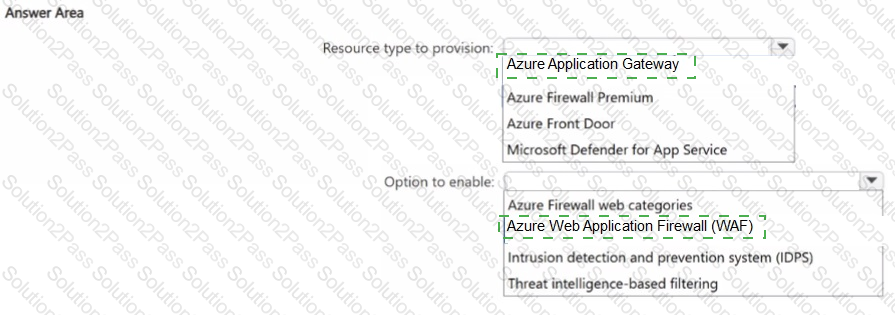
You have an Azure subscription that contains App Service web apps in four Azure regions. Users connect to the apps from the internet.
You plan to block requests to the apps if the requests contain security threats specified in the Core Rule Set (CRS) of the Open Web Application Security Project (OWASP).
You need to design a solution to block the requests. The solution must meet the following requirements:
• Maintain access to the apps in the event of a region outage.
• Minimize the number of resources required.
What should you include in the design? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You are designing a ransomware mitigation strategy
You perform a ransomware risk assessment and identify business-critical assets.
You need to recommend a solution to mitigate ransomware threats. The solution must follow Microsoft security best practices.
Which two actions should you include in the recommendation? Each correct answer presents a complete solution.
NOTE: Each correct answer is worth one point.
You have four Azure subscriptions named Sub1, Sub2, Sub3, and Sub4. Each subscription has a unique Microsoft Entra tenant that is linked to a Microsoft 365 subscription. Sub1 contains a user named User1.
You plan to implement Microsoft Sentinel.
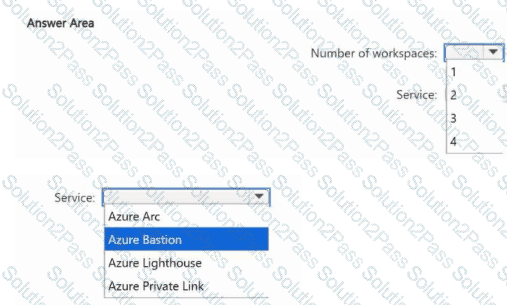
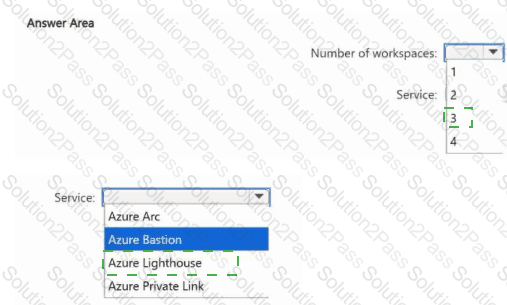
You need to ensure that User1 can monitor Microsoft Entra ID events and Microsoft 365 events for Sub2, Sub3, and Sub4 by using Microsoft Sentinel. The solution must minimize administrative effort.
What is the minimum number of Microsoft Sentinel workspaces you should create, and which Azure service should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an Azure subscription and a Microsoft 365 subscription.
Your company uses several software as a service (SaaS) applications.
To align with Microsoft cloud security benchmark (MCSB) and Microsoft Cybersecurity Reference Architectures (MCRA), you plan to design a solution to provide visibility into user activity across the applications and detect potentially risky behavior in real time.
Which service should you recommend?
A customer follows the Zero Trust model and explicitly verifies each attempt to access its corporate applications.
The customer discovers that several endpoints are infected with malware.
The customer suspends access attempts from the infected endpoints.
The malware is removed from the end point.
Which two conditions must be met before endpoint users can access the corporate applications again? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
You have a multicloud environment that contains an Azure subscription, an Amazon Web Services (AWS) subscription, and a Google Cloud Platform (GCP) subscription.
You plan to assess data security and compliance.
You need to design a Compliance Manager solution that meets the following requirements:
• Provides recommended improvement actions that include detailed implementation guidance
• Automatically monitors regulatory compliance
• Minimizes administrative effort
What should you include in the solution?
Your company plans to apply the Zero Trust Rapid Modernization Plan (RaMP) to its IT environment.
You need to recommend the top three modernization areas to prioritize as part of the plan.
Which three areas should you recommend based on RaMP? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
You plan to implement an Azure environment based on Microsoft Cloud Adoption Framework for enterprise-scale landing zone architecture principles .
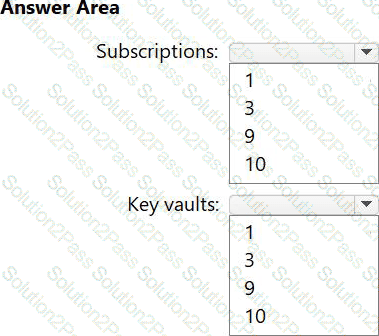
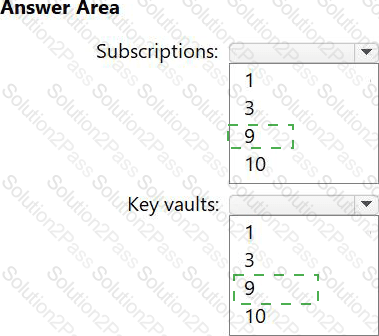
The environment will host three apps that have the following characteristics:
• Each app will have a development environment, a test environment, and a production environment.
• Each environment will be managed by a separate team.
• Each app will store its secrets in Azure Key Vault.
You need to recommend how many Azure subscriptions and key vaults to deploy to the application landing zones.
What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure DevOps organization that is used to manage the development and deployment of internal apps to multiple Azure subscriptions.
You are developing a DevSecOps strategy.
You need to apply DevSecOps controls for the secure code stage and the secure operations stage. The solution must be based on Microsoft Cloud Adoption Framework for Azure principles.
What should you apply for each stage? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
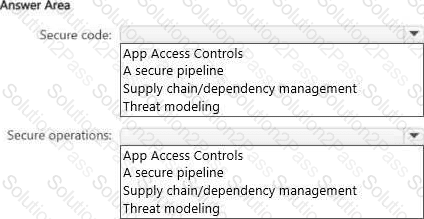
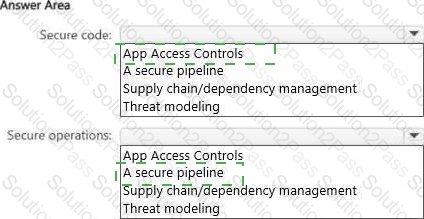
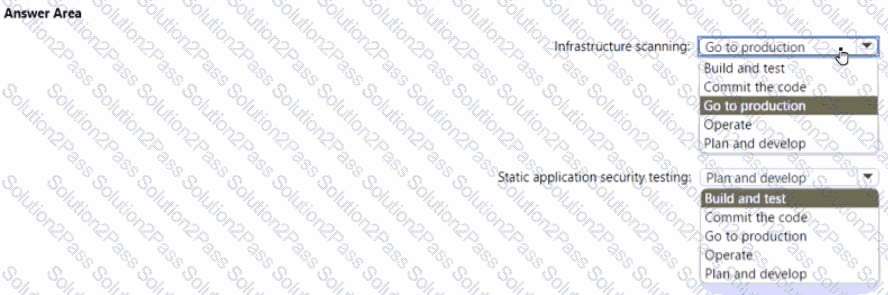
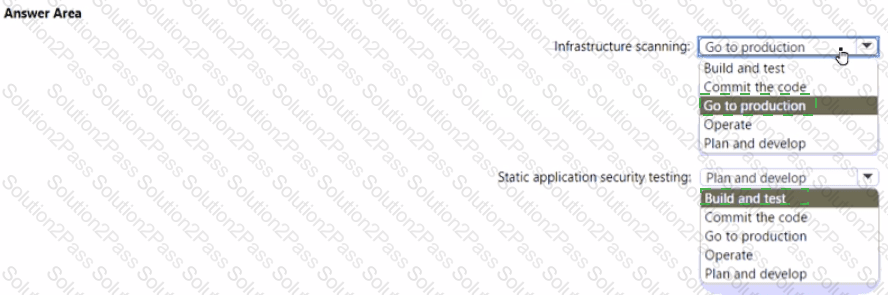
Your company plans to follow DevSecOps best practices of the Microsoft Cloud Adoption Framework for Azure to integrate DevSecOps processes into continuous integration and continuous deployment (Cl/CD) DevOps pipelines
You need to recommend which security-related tasks to integrate into each stage of the DevOps pipelines.
What should recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
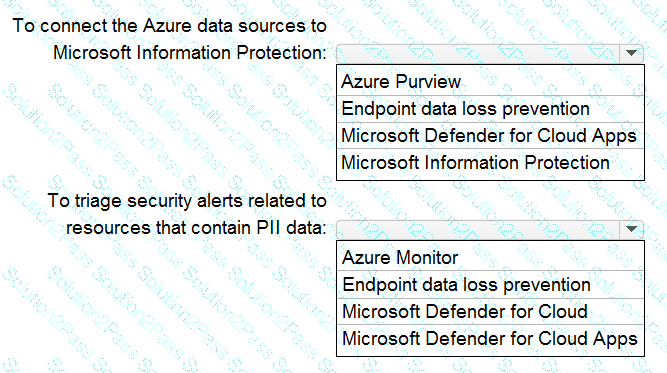
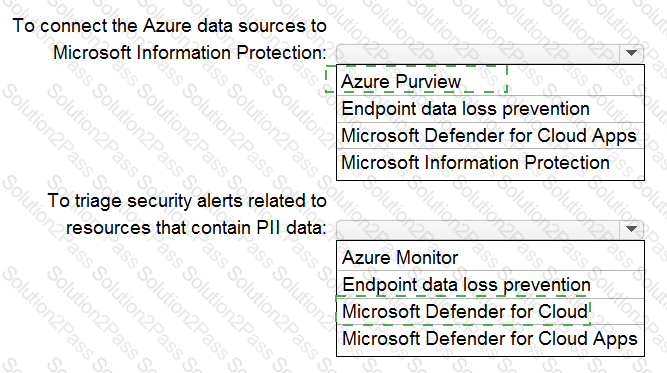
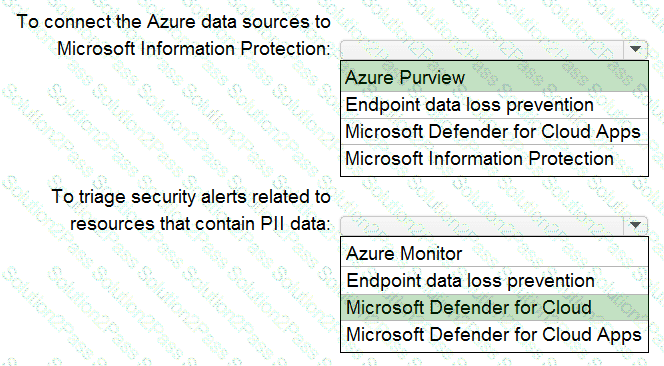
Your company is migrating data to Azure. The data contains Personally Identifiable Information (Pll). The company plans to use Microsoft Information Protection for the Pll data store in Azure. You need to recommend a solution to discover Pll data at risk in the Azure resources.
What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains multiple Azure Blob Storage accounts.
You need to recommend a solution to detect threats in files after the files are uploaded to a blob container.
What should you include in the recommendation?
Your company has a hybrid cloud infrastructure that contains an on-premises Active Directory Domain Services (AD DS) forest, a Microsoft B65 subscription, and an Azure subscription.
The company ' s on-premises network contains internal web apps that use Kerberos authentication. Currently, the web apps are accessible only from the network.
You have remote users who have personal devices that run Windows 11.
You need to recommend a solution to provide the remote users with the ability to access the web apps. The solution must meet the following requirements:
• Prevent the remote users from accessing any other resources on the network.
• Support Azure Active Directory (Azure AD) Conditional Access.
• Simplify the end-user experience.
What should you include in the recommendation?
You have an Azure subscription that has Microsoft Defender for Cloud enabled. You need to enforce ISO 2700V2013 standards for the subscription. The solution must ensure that noncompliant resources are remediated automatically
What should you use?
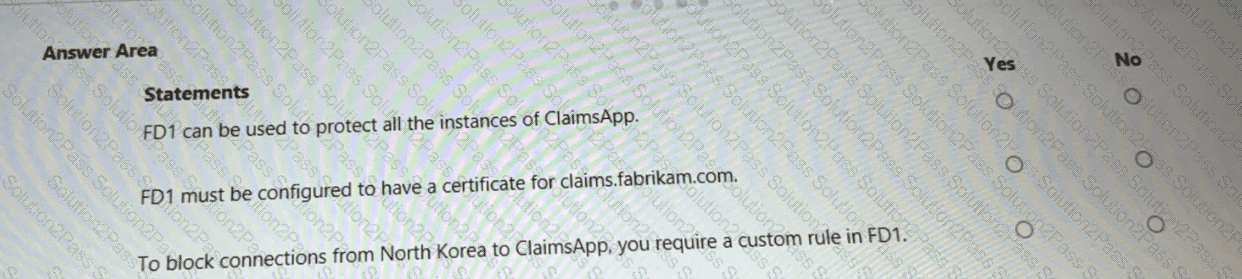
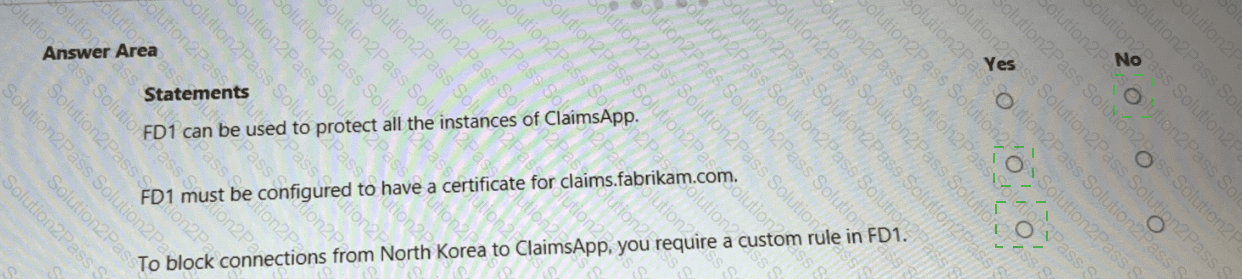
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
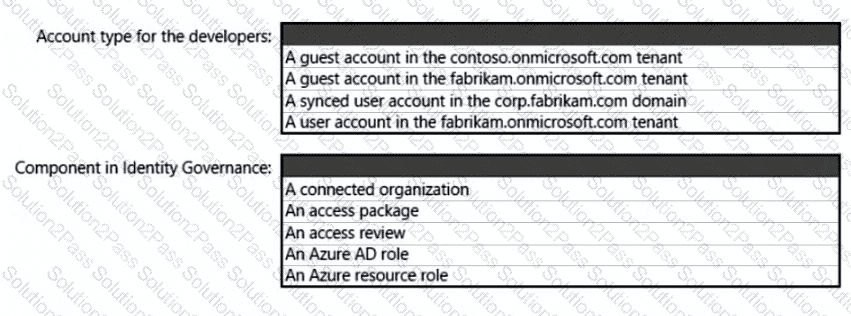
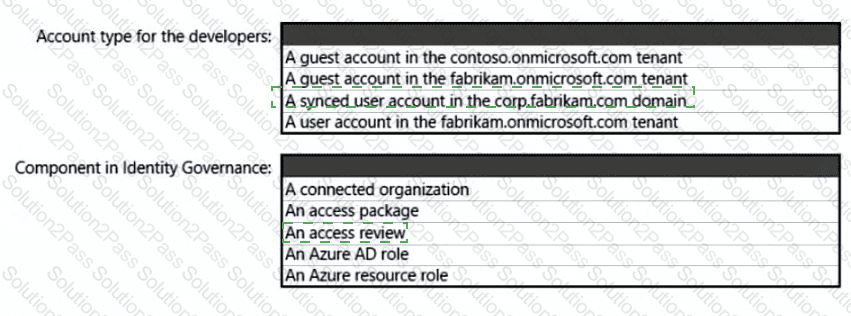
What should you create in Azure AD to meet the Contoso developer requirements?