Identity-Security-Administrator SailPoint Certified Identity Security Administrator Free Practice Exam Questions (2026 Updated)
Prepare effectively for your SailPoint Identity-Security-Administrator SailPoint Certified Identity Security Administrator certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Total 99 questions
Assuming an access item's approval type is set to "reviewer," does the following statement accurately describe the approval flow behavior?
Proposed Solution / Statement:
When a user requests access for themselves and they are also in the approval chain, the approval flow will route to their manager instead to prevent a conflict of interest.
Does this proposed solution meet the requirement / solve the scenario?
Is the following statement true about the characteristics of different connector types in Identity Security Cloud (ISC)?
Proposed Solution / Statement:
Active Directory (AD) connectors can handle both authentication and identity lifecycle management, including user provisioning.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement regarding the objects that represent access of systems managed by Identity Security Cloud?
Proposed Solution / Statement:
When criteria for automatic assignment of a Role are set to Identity List, the names of identities to include can be specified using wildcards, for example "John*".
Does this proposed solution meet the requirement / solve the scenario?
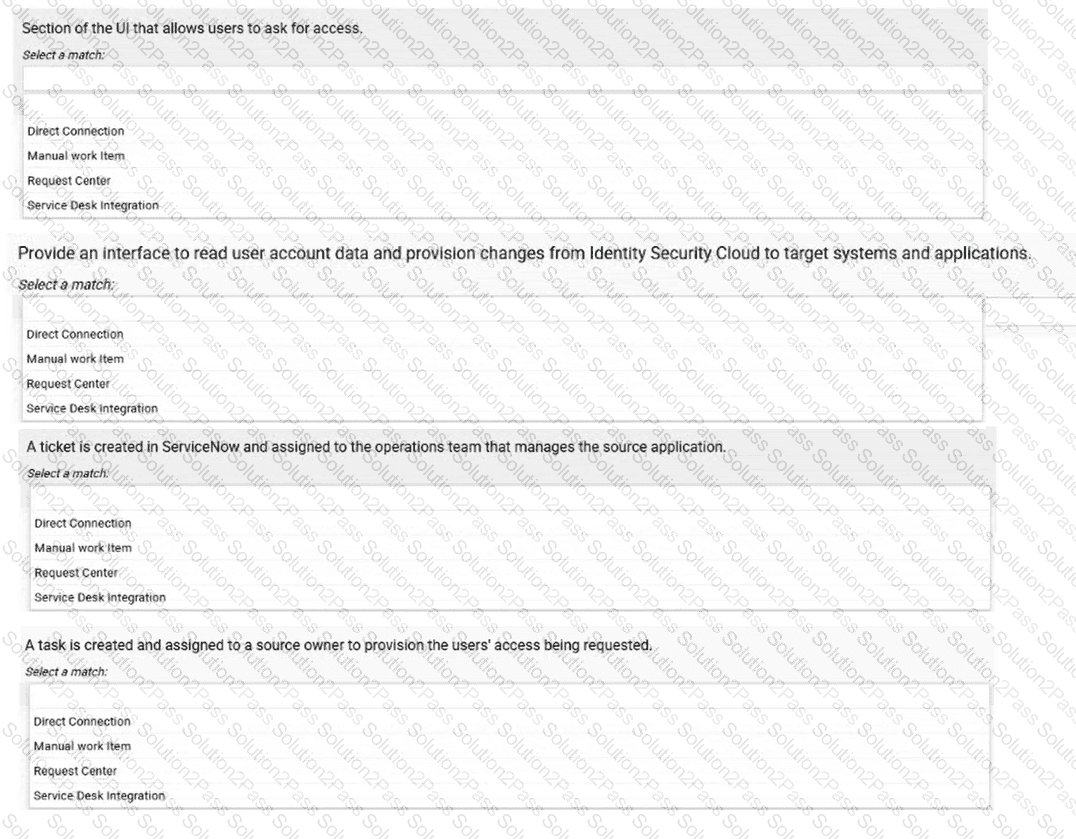
Match the following descriptions with their appropriate definition.

Assuming an access item's approval type is set to "reviewer," does the following statement accurately describe the approval flow behavior?
Proposed Solution / Statement:
When a governance group is set as an approver, the request is automatically approved if the requester is a member of that governance group.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement about sources?
Proposed Solution / Statement:
A Delimited File Source can automatically aggregate from a file share.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement regarding sources in Identity Security Cloud?
Proposed Solution / Statement:
Sources primarily serve as backup storage locations for identity data to ensure business continuity in case of system failures.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid way to set-up role assignment criteria?
Proposed Solution / Statement:
A list of Excluded Identities can be defined to prevent specific identities from receiving the role membership.
Does this proposed solution meet the requirement / solve the scenario?
Is the following true regarding User Levels and permissions?
Proposed Solution / Statement:
Role Admin and Source Sub-Admin can be granted to an identity at the same time.
Does this proposed solution meet the requirement / solve the scenario?
Users are complaining that they would like to request access to groups that have recently been added to the Corporate Directory system, but they are unable to see them. The system feature Enable Entitlement Requests has been enabled and access request segments have not been enabled.
Is this a valid step to debug the problem?
Proposed Solution / Statement:
Open the source configuration and navigate to the Access Profiles page to check if the group is included in it and thus hidden by any Access Profile.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement about how an administrator reviews provisioning activity?
Proposed Solution / Statement:
By default, account activity information is presented in a descending sequence based on the Last Modified Date. However, the administrator can sort ascending or descending by any column.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement regarding the objects that represent access of systems managed by Identity Security Cloud?
Proposed Solution / Statement:
Criteria for automatic assignment of a Role can be set to Standard Criteria or Identity List.
Does this proposed solution meet the requirement / solve the scenario?
Does this statement accurately describe the proper methods for creating and scheduling reports in Identity Security Cloud?
Proposed Solution / Statement:
All valid search queries can be scheduled as reports.
Does this proposed solution meet the requirement / solve the scenario?
Test connection for the Active Directory source fails when Transport Layer Security (TLS) is on:
java.lang.Exception: [s0100] Failed to connect to server ...
PKIX path validation failed
sun.security.provider.certpath.SunCertPathBuilderException: unable to find valid certification path to requested target
Is this a valid step towards analyzing and resolving this issue?
Proposed Solution / Statement:
Ensure that the correct AD certificate has been imported in the VA certificates folder.
Does this proposed solution meet the requirement / solve the scenario?
Below are the requirements for configuring user provisioning in an organization's Finance department.
Contractors in the organization MUST NOT be auto-provisioned with the default Office 365 license, as contractors in departments other than Finance have different license requirements.
Every Finance department user — whether employee or contractor — must be assigned one Office 365 E3 license.
No Finance employee or contractor should be provisioned more than one type of Office 365 license.
Is this a valid approach for the Identity Security Administrator to provide the necessary access?
Proposed Solution / Statement:
Create an ISC Role with membership criteria that includes all Finance department contractors. Assign an Access Profile associated with the default Office 365 license. Add these users to the Office 365 E3 license entitlement so they receive an account with the default Office 365 license and the required E3 license.
Does this proposed solution meet the requirement / solve the scenario?
An organization is considering purchasing an IGA tool. The manager asks the administrator to explain what compliance features the IGA tool provides for separation of duties, protecting personally identifying data and privileged access, and how the company can prove to the auditors that they comply with all laws and regulations.
Is this a good explanation of one of such features?
Proposed Solution / Statement:
"Separation of duties can be enforced using rules that can be configured in the system. These rules look for forbidden combinations of access owned by a single user. The rules can be used in a detective way, meaning actively searching for these forbidden combinations, or a preventative way, meaning that an extra validation step is made when a change in user access is requested."
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid statement about common authentication methods?
Proposed Solution / Statement:
The Identity Provider and Service Provider in a SAML setup trust each other based on public keys that have been exchanged as part of the configuration.
Does this proposed solution meet the requirement / solve the scenario?
On 4 February 2021, the following error occurred on source Control Central of type Active Directory for identity Clarence.Harper:
Failed to update attributes. There is no such object on the server.
Is this a valid place to look for more information about what caused the error?
Proposed Solution / Statement:
Search for the error message on SailPoint Compass or the SailPoint Developer Forums. Check for previous discussions or whitepapers.
Does this proposed solution meet the requirement / solve the scenario?
A certification campaign was created for manager review. However, the user's certification campaign was assigned to an admin instead of their manager.
Is this a valid reason for why the campaign could have been reassigned?
Proposed Solution / Statement:
User does not have a manager assigned from HR.
Does this proposed solution meet the requirement / solve the scenario?
A new employee's identity is not correctly created and shows in the Identity Exceptions report on the Identity Profile.
Is this a correct step towards analyzing and resolving the problem?
Proposed Solution / Statement:
Ensure the account attributes mapped to the identity attributes User Name (uid), Work Email (email), and Last Name are populated correctly.
Does this proposed solution meet the requirement / solve the scenario?
Total 99 questions