SPLK-5002 Splunk Certified Cybersecurity Defense Engineer Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Splunk SPLK-5002 Splunk Certified Cybersecurity Defense Engineer certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
How can you incorporate additional context into notable events generated by correlation searches?
What is Enterprise Security ' s default way of determining the urgency of a finding (notable event)?
An engineer notices that a detection is creating multiple Findings (notables) for the same potential incident. Which setting can be adjusted to reduce the number of generated findings (notables)?
What must be configured as a setting in a correlation search for a notable to be generated?
Based on the provided screenshot, it ' s discovered that different machines or accounts have been associated with the shown threat objects.
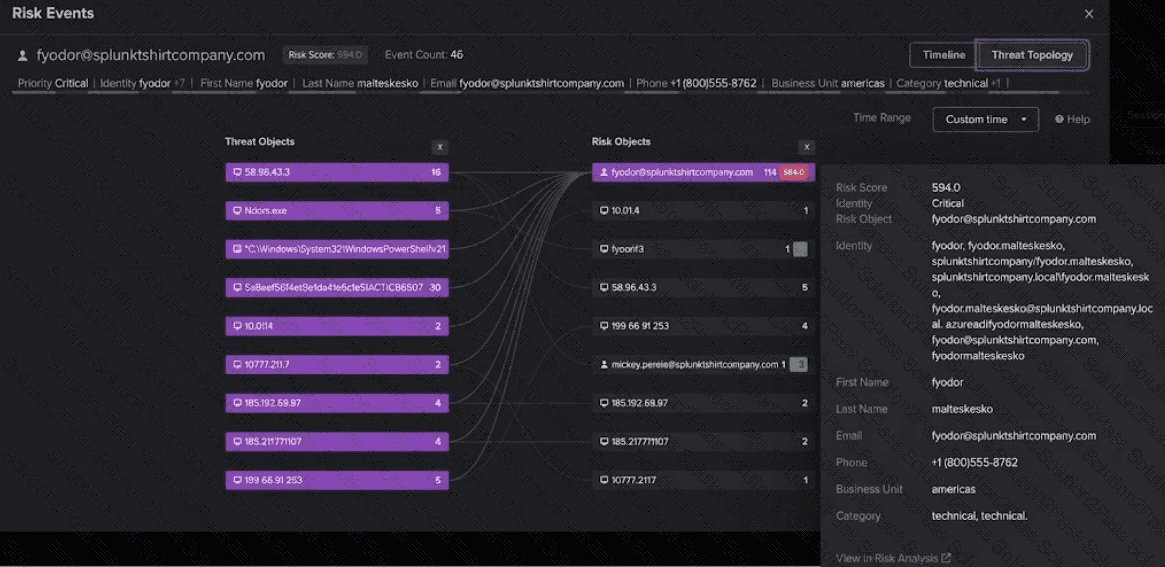
Enterprise Security has identified that these machines and accounts all point back to one owner - Fyodor. Which two frameworks in ES are responsible for programmatically associating this information together?
What is a key feature of effective security reports for stakeholders?
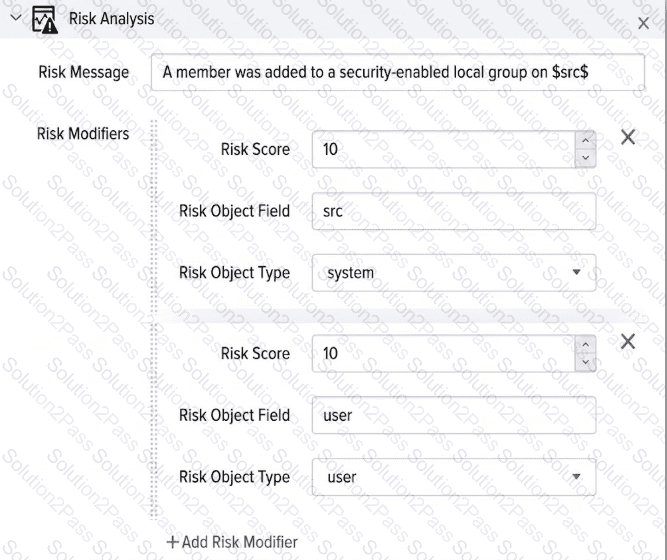
Based on this example image, if it is detected that a member has been added to a security-enabled local group, how many risk events will be created?
An engineer is writing a correlation search and needs to use T1059 from MITRE ATT & CK as a field in Incident Review. Assuming they are writing a correlation search that does not use the Risk data model, which example statement should be appended to the correlation search?
What document can be helpful in understanding the prioritization of risk when comparing entities in an organization?
Which of the following actions will allow access to a list of alert actions via the API?
The Director of Security would like to understand the operational efficiency of the SOC analysts at a high level. What is a metric that can be used to determine their efficiency?