SPLK-5003 Splunk Certified Cybersecurity Defense Architect Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Splunk SPLK-5003 Splunk Certified Cybersecurity Defense Architect certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Whovert’s CEO has said that the company’s top priority is to operate more efficiently and move faster.
As an architect, which solution can best help the SOC align with this priority?
Review the output shown below.
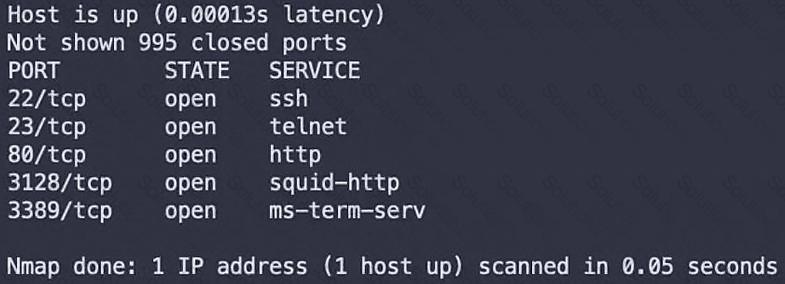
What should be the first action taken to harden this host?
An architect is advising an organization that must send data to multiple destination data stores according to a combination of criteria. This includes, but is not limited to, the presence of personally identifiable information (PII), particular key/value pairs in each event, and the required retention period for specific data sources.
Which type of technology would be most appropriate for meeting these requirements?
At which stage of the DevOps CI/CD pipeline is it most effective to create an SBOM?
Buttercup Games has implemented more than 100 detections in its SOC. These detections are mostly vendor-provided signatures and tuned field matching, with a few custom-built detections.
Which more advanced detection method should it deploy?
An architect is preparing for a net-new SIEM deployment.
Which of the following data sources provides the most immediate security value?
A U.S.-based company recently acquired a German company. The U.S. organization plans to consolidate its customer rewards program globally and start collecting purchasing information about German customers for transmission to its U.S. data center.
Which data privacy law would the organization violate if it did not update the German End User Agreement?
The cybersecurity team at a logistics management company plans to work with its software engineering practice in a “shift-left” approach to securing the software development life cycle (SDLC).
What improvement could the team recommend to enable early detection of software vulnerabilities?
Samuel is a security architect at a retail company headquartered in France. The company is developing a software product to track, store, and analyze clicks on its website. It plans to use this data to develop advertising tailored to each user and offer promotional items. Samuel is responsible for ensuring that the software satisfies the company’s compliance requirements.
Which feature must Samuel ensure is included?
Which type of data does OpenTelemetry supply that the security team can use during an investigation?
Which of the following describes the benefits of modern cybersecurity-defense data architectures that use technologies such as data fabric, data lakes, message bus, and federated search?
Which of the following is a principal benefit of incorporating machine learning into an organization’s security-detection capabilities?
AJ has been assigned to design controls for a new, low-latency and highly resilient application. The business requires no downtime if a device fails or while maintenance is performed.
Which of the following deployment options will satisfy these requirements?
Carter is an architect at an organization that is preparing design and support documentation for a net-new SOAR deployment.
What must Carter consider?
Choose three
How should the control network in a water treatment plant be segregated from other networks?
June has been hired as the first security architect for a U.S.-based public healthcare company. She needs to establish a baseline of controls that should be evaluated in the environment.
Which frameworks should she include as part of the baseline?
Choose three
Buttercup Games’ incident-response team has identified IOCs associated with the “Water Curse” campaign in its development environment. Suspicious activity indicates unauthorized access to developer workstations and possible manipulation of source code in its version-control software, GitLow. Given “Water Curse’s” known weaponization of open-source dependencies, a forensic investigation is necessary to establish the breach’s full scope, identify affected systems, and gather evidence.
To support a forensic investigation of the “Water Curse” compromise at Buttercup Games, which triage steps should be performed?
Choose three
Yokoco has engaged Helpime to conduct a penetration test. The test scope covers all web-facing internet applications. Helpime has completed the test and delivered its report to Yokoco.
What should be done with the report’s unremediated findings?
When obtaining forensic artifacts, which critical step helps ensure they are admissible in court?
Which of the following are commonly used criteria for evaluating threat-intelligence feeds?
Choose three