350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Refer to the exhibit.
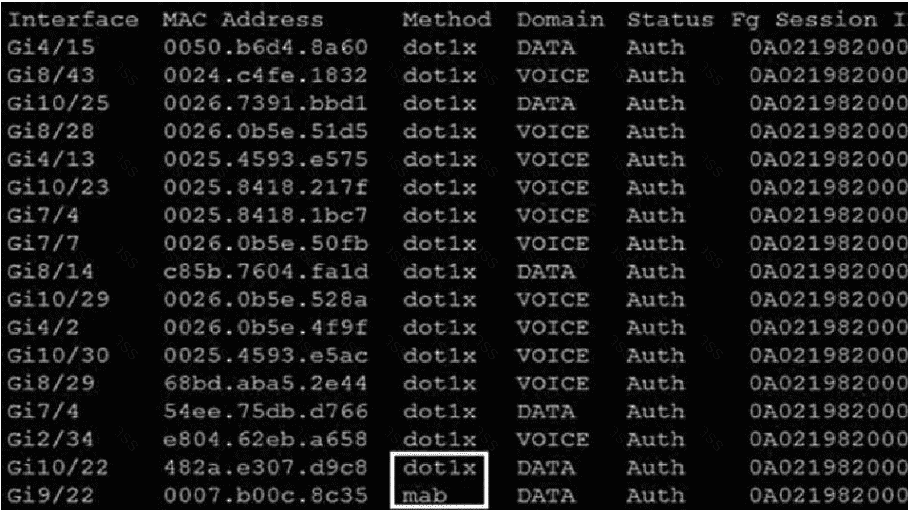
Which command was used to generate this output and to show which ports are
authenticating with dot1x or mab?
Refer to the exhibit.
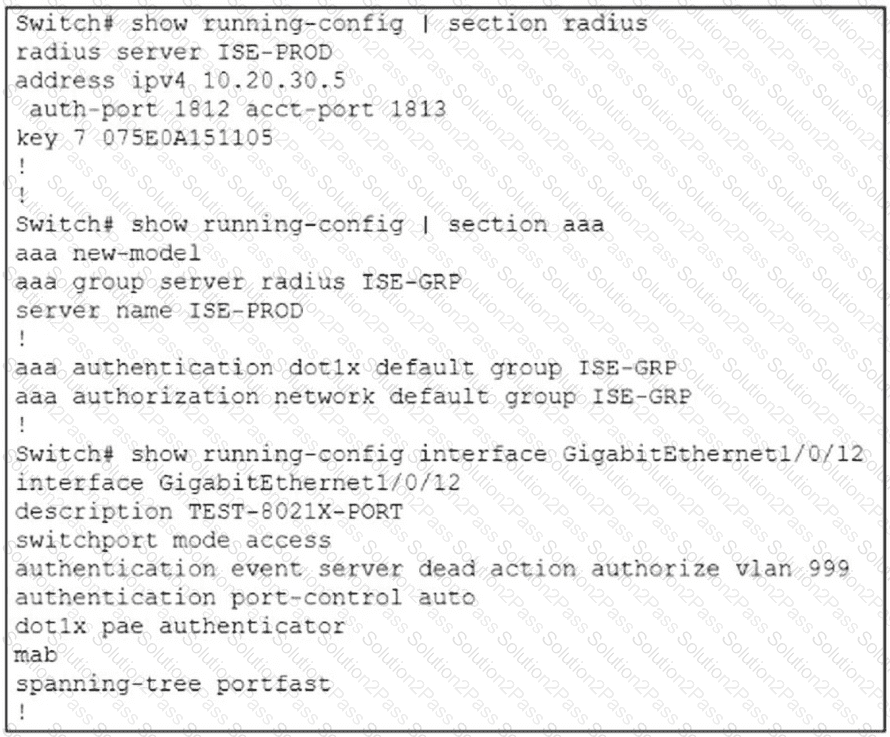
A newly installed stack of Cisco Catalyst switches has been integrated with Cisco ISE for 802.1X port control and downloadable access control list (dACL) enforcement. Test workstations authenticate successfully, but the expected dACL never appears in the port configuration, leaving all traffic unrestricted. Packet captures confirm that Cisco ISE transmits the correct attributes, yet the switches classify them as “unknown” and ignore the instructions. A review of the running configuration shows complete AAA and 802.1X configuration. Which configuration command must be added to resolve the issue?
An administrator has been tasked with configuring the Cisco Secure Email Gateway to ensure there are no viruses before quarantined emails are delivered. In addition, delivery of mail from known bad mail servers must be prevented. Which two actions must be taken in order to meet these requirements? (Choose two.)
A network administrator is configuring SNMPv3 on a new router. The users have already been created;
however, an additional configuration is needed to facilitate access to the SNMP views. What must the
administrator do to accomplish this?
Which encryption algorithm provides highly secure VPN communications?
The main function of northbound APIs in the SDN architecture is to enable communication between which two areas of a network?
Which type of DNS abuse exchanges data between two computers even when there is no direct connection?
Which method must be used to connect Cisco Secure Workload to external orchestrators at a client site when the client does not allow incoming connections?
A network administrator needs a solution to match traffic and allow or deny the traffic based on the type of application, not just the source or destination address and port used. Which kind of security product must the network administrator implement to meet this requirement?
Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?
An administrator configures a Cisco WSA to receive redirected traffic over ports 80 and 443. The organization requires that a network device with specific WSA integration capabilities be configured to send the traffic to the WSA to proxy the requests and increase visibility, while making this invisible to the users. What must be done on the Cisco WSA to support these requirements?
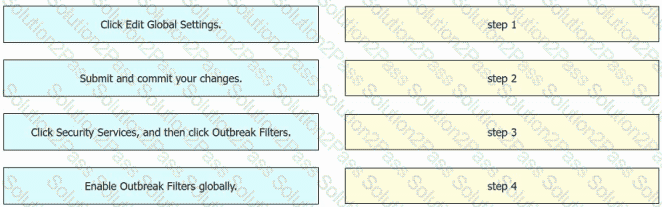
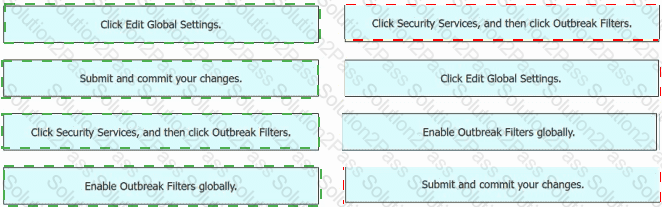
An engineer must enable Outbreak Filters globally on an AsyncOS for Cisco Secure Email Gateway to protect the network from large-scale malware attacks. Drag and drop the steps from the left into the sequence on the right to complete the configuration.
Which technology is used to improve web traffic performance by proxy caching?
A network engineer must configure a Cisco Secure Email Gateway to prompt users to enter two forms of information before gaining access. The Secure Email Gateway must also join a cluster machine using preshared keys. What must be configured to meet these requirements?
A network engineer must enable DHCP snooping on the corporate switches only for VLAN 2. Management requires DHCP traffic from unauthorized servers to be dropped. DHCP snooping is already enabled globally, and the uplink interface toward the authorized DHCP server is already trusted. Which configuration command must be applied to meet the requirement?
A network engineer is configuring DMVPN and entered the crypto isakmp key cisc0380739941 address 0.0.0.0 command on hostA. The tunnel is not being established to hostB. What action is needed to authenticate the VPN?
Which two parameters are used for device compliance checks? (Choose two.)
What is a characteristic of Dynamic ARP Inspection?
After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.
Which task can you perform to determine where each message was lost?
What is the difference between EPP and EDR?
An engineer is deploying a Cisco Secure Email Gateway and must ensure it reaches the Cisco update servers to retrieve new rules. The engineer must now manually configure the Outbreak Filter rules on an AsyncOS for Cisco Secure Email Gateway. Only outdated rules must be replaced. Up-to-date rules must be retained. Which action must the engineer take next to complete the configuration?
An administrator enables Cisco Threat Intelligence Director on a Cisco FMC. Which process uses STIX and allows uploads and downloads of block lists?
Which two activities can be done using Cisco DNA Center? (Choose two)
A company identified a phishing vulnerability during a pentest. What are two ways the company can protect employees from the attack? (Choose two.)
An engineer must implement an external application that authenticates against the Cisco Secure Email Threat Defense API to perform automated message searches. The application already presents a user bearer token, but the API requires an additional authentication header with each request. The engineer must configure the external application to include the required header alongside the bearer token so that the API calls are accepted. Which header must be configured?
A mall provides security services to customers with a shared appliance. The mall wants separation of
management on the shared appliance. Which ASA deployment mode meets these needs?
A security administrator must implement a network intrusion policy in Cisco Secure Firewall to block new potential threats without sacrificing network performance. The administrator plans to create a base policy with a broad rule set optimized to protect the environment without significantly affecting throughput. Which type of policy should the administrator create?
In which two ways does the Cisco Advanced Phishing Protection solution protect users? (Choose two.)
An organization must add new firewalls to its infrastructure and wants to use Cisco ASA or Cisco FTD.
The chosen firewalls must provide methods of blocking traffic that include offering the user the option to bypass the block for certain sites after displaying a warning page and to reset the connection. Which solution should the organization choose?
Which suspicious pattern enables the Cisco Tetration platform to learn the normal behavior of users?
