350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
A healthcare organization is deploying Cisco Secure Access to prevent protected health information from being shared with generative AI services. The security team requires real-time DLP inspection only for traffic destined for AI applications, with minimal false positives during general web browsing. The policy must permit tuning based on the proximity and match counts of PHI identifiers. Which configuration action must the engineer perform?
What is a characteristic of Cisco ASA Netflow v9 Secure Event Logging?
On Cisco Firepower Management Center, which policy is used to collect health modules alerts from managed
devices?
What is a difference between Cisco AMP for Endpoints and Cisco Umbrella?
Which information is required when adding a device to Firepower Management Center?
Refer to the exhibit.
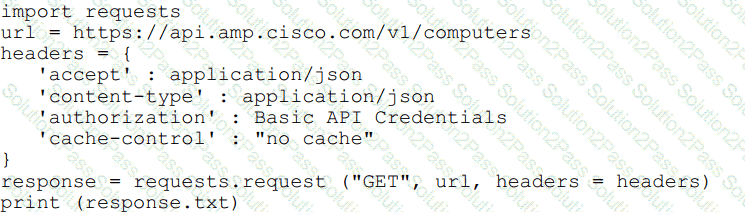
What will happen when this Python script is run?
Which two endpoint measures are used to minimize the chances of falling victim to phishing and social
engineering attacks? (Choose two)
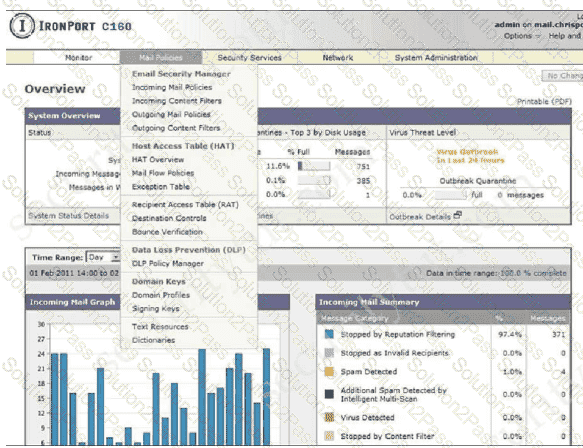
An organization received a large amount of SPAM messages over a short time period. In order to take action on the messages, it must be determined how harmful the messages are and this needs to happen dynamically.
What must be configured to accomplish this?
An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users,
data, and applications. There is a requirement to use the Cisco cloud native CASB and cloud cybersecurity
platform. What should be used to meet these requirements?
A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:
The test user is part of the Marketing Active Directory group.
The domain socialmediaexample.org belongs to the social media category.
The user is configured with the Umbrella Roaming Client for DNS redirection.
All other social media websites are properly blocked for the same user and match the correct policy.
Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?
An engineer configures new features within the Cisco Umbrella dashboard and wants to identify and proxy traffic that is categorized as risky domains and may contain safe and malicious content. Which action accomplishes these objectives?
Which method of attack is used by a hacker to send malicious code through a web application to an unsuspecting user to request that the victim ' s web browser executes the code?
Which term describes when the Cisco Secure Firewall downloads threat intelligence updates from Cisco Tables?
Which two deployment model configurations are supported for Cisco FTDv in AWS? (Choose two)
Which flaw does an attacker leverage when exploiting SQL injection vulnerabilities?
Which Cisco firewall solution supports configuration via Cisco Policy Language?
An engineer needs to detect and quarantine a file named abc424400664 zip based on the MD5 signature of the file using the Outbreak Control list feature within Cisco Advanced Malware Protection (AMP) for Endpoints The configured detection method must work on files of unknown disposition Which Outbreak Control list must be configured to provide this?
Which SNMPv3 configuration must be used to support the strongest security possible?
Refer to the exhibit.
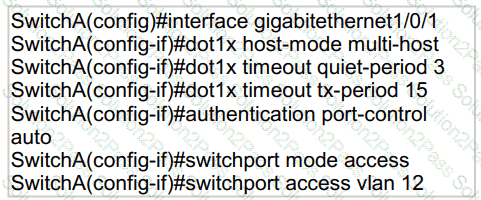
An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?
When configuring ISAKMP for IKEv1 Phase1 on a Cisco IOS router, an administrator needs to input the
command crypto isakmp key cisco address 0.0.0.0. The administrator is not sure what the IP addressing in this command issued for. What would be the effect of changing the IP address from 0.0.0.0 to 1.2.3.4?
What is a benefit of using Cisco CWS compared to an on-premises Cisco WSA?
Why is it important to have a patching strategy for endpoints?
Cisco SensorBase gaihers threat information from a variety of Cisco products and services and performs analytics to find patterns on threats Which term describes this process?
Which process is used to obtain a certificate from a CA?
Which two products are used to forecast capacity needs accurately in real time? (Choose two.)
Which two request of REST API are valid on the Cisco ASA Platform? (Choose two)
What is a functional difference between Cisco Secure Endpoint and Cisco Umbrella Roaming Client?
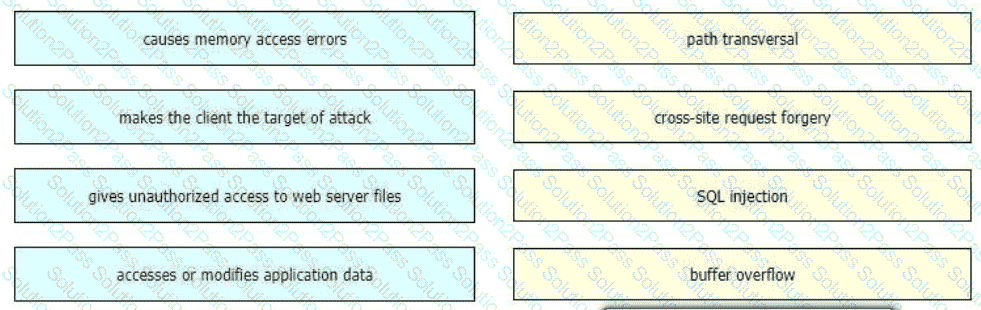
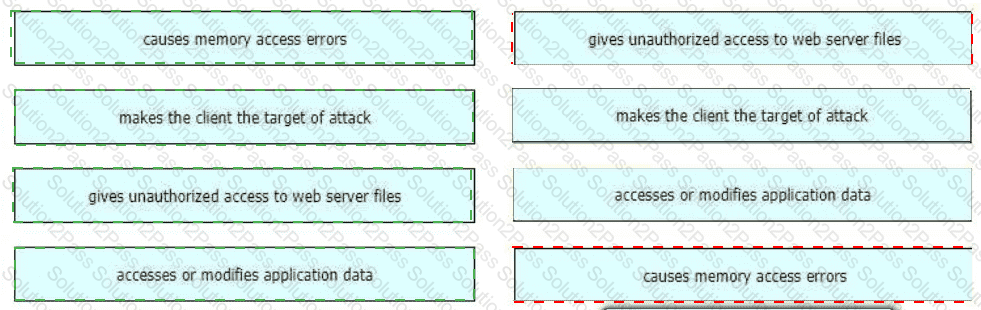
Drag and drop the exploits from the left onto the type of security vulnerability on the right.
Which Cisco AMP file disposition valid?
