Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 3 / 8
Total 801 questions

What is a prerequisite when integrating a Cisco ISE server and an AD domain?

A.

Place the Cisco ISE server and the AD server in the same subnet

B.

Configure a common administrator account

C.

Configure a common DNS server

D.

Synchronize the clocks of the Cisco ISE server and the AD server

What is a feature of the open platform capabilities of Cisco DNA Center?

A.

intent-based APIs

B.

automation adapters

C.

domain integration

D.

application adapters

With which components does a southbound API within a software-defined network architecture communicate?
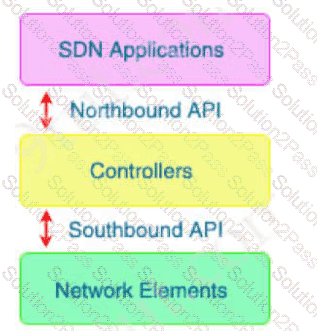
A.

controllers within the network

B.

applications

C.

appliances

D.

devices such as routers and switches

An engineer must modify an existing remote access VPN using a Cisco AnyConnect Secure Mobility client solution and a Cisco Secure Firewall. Currently, all the traffic generate by the user Is sent to the VPN tunnel and the engineer must now exclude some servers and access them directly instead. Which element must be modified to achieve this goat?

A.

NAT exemption

B.

encryption domain

C.

routing table

D.

group policy

Which compliance status is shown when a configured posture policy requirement is not met?

A.

compliant

B.

unknown

C.

authorized

D.

noncompliant

With Cisco AMP for Endpoints, which option shows a list of all files that have been executed in your

environment?

A.

Prevalence

B.

File analysis

C.

Detections

D.

Vulnerable software

E.

Threat root cause

Which security solution protects users leveraging DNS-layer security?

A.

Cisco ISE

B.

Cisco FTD

C.

Cisco Umbrella

D.

Cisco ASA

A network engineer is enabling RADIUS CoA on a fleet of Cisco Catalyst switches so that Cisco ISE can quarantine compromised endpoints in real time. To uniquely target an active session for disconnect or reauthorization, Cisco ISE must include IETF attribute 31 to identify the endpoint. Which configuration action must be performed on Cisco ISE to meet the requirement?

A.

Configure the Calling-Station-ID attribute for CoA session identification.

B.

Apply the Message-Authenticator attribute for endpoint session lookup.

C.

Implement the Acct-Session-ID attribute for matching the active session.

D.

Use the NAS-Port-ID attribute for the CoA disconnect request.

What are the components of endpoint protection against social engineering attacks?

A.

IPsec

B.

IDS

C.

Firewall

D.

Cisco Secure Email Gateway

An engineer is implementing NAC for LAN users on a segmented network. The engineer confirms that the device of each user is supported and the Cisco switch configuration is correct.

Which configuration should be made next to ensure there are no authentication issues?

A.

Disable the host firewall.

B.

Enable TACACS+ on the switch.

C.

Open TCP port 49.

D.

Permit UDP port 1812.

Which characteristic is unique to a Cisco WSAv as compared to a physical appliance?

A.

supports VMware vMotion on VMware ESXi

B.

requires an additional license

C.

performs transparent redirection

D.

supports SSL decryption

A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?

A.

a Network Discovery policy to receive data from the host

B.

a Threat Intelligence policy to download the data from the host

C.

a File Analysis policy to send file data into Cisco Firepower

D.

a Network Analysis policy to receive NetFlow data from the host

Which feature is supported when deploying Cisco ASAv within AWS public cloud?

A.

multiple context mode

B.

user deployment of Layer 3 networks

C.

IPv6

D.

clustering

A network engineer must enable SSH and SCP on a Cisco IOS router. The engineer has already generated the encryption keys and enabled SCP services on the router. Which configuration action must be performed next?

A.

Enable SSHv2 in the configuration.

B.

Restrict access to specific SSH commands.

C.

Enable SCP strict host-key checking.

D.

Add an ACL to deny access from the LAN.

What is the purpose of the Cisco Endpoint loC feature?

A.

It provides stealth threat prevention.

B.

lt is a signature-based engine.

C.

lt is an incident response tool

D.

It provides precompromise detection.

Which component of a Cisco IOS NetFlow solution enables the aggregation of data packets into flows?

A.

Analyzer

B.

Sampler

C.

Collector

D.

Exporter

What are two differences between a Cisco Secure Web Appliance that is running in transparent mode and one running in explicit mode? (Choose two.)

A.

The Cisco Secure Web Appliance responds with its own IP address only if it is running in transparent mode.

B.

When the Cisco Secure Web Appliance is running in transparent mode, it uses the Secure Web Appliance ' s own IP address as the HTTP request destination.

C.

The Cisco Secure Web Appliance responds with its own IP address only if it is running in explicit mode.

D.

The Cisco Secure Web Appliance is configured in a web browser only if it is running in transparent mode.

E.

The Cisco Secure Web Appliance uses a Layer 3 device to redirect traffic only if it is running in transparent mode.

Which protocol does the BYOD component in Cisco ISE use to obtain a unique device certificate from an internal CA?

A.

CMP

B.

SCEP

C.

SFTP

D.

OCSP

An engineer is configuring cloud logging on Cisco ASA and needs events to compress. Which component must be configured to accomplish this goal?

A.

CDO event viewer

B.

SWC service

C.

Cisco analytics

D.

SDC VM

What is the function of SDN southbound API protocols?

A.

to allow for the dynamic configuration of control plane applications

B.

to enable the controller to make changes

C.

to enable the controller to use REST

D.

to allow for the static configuration of control plane applications

How does Cisco Secure Endpoint provide next-generation protection?

A.

It integrates with Cisco FTD devices.

B.

It encrypts data on user endpoints to protect against ransomware.

C.

It leverages an endpoint protection platform and endpoint detection and response.

D.

It utilizes Cisco pxGrid, which allows Secure Endpoint to pull threat feeds from threat intelligence centers.

An administrator is configuring a DHCP server to better secure their environment. They need to be able to ratelimit the traffic and ensure that legitimate requests are not dropped. How would this be accomplished?
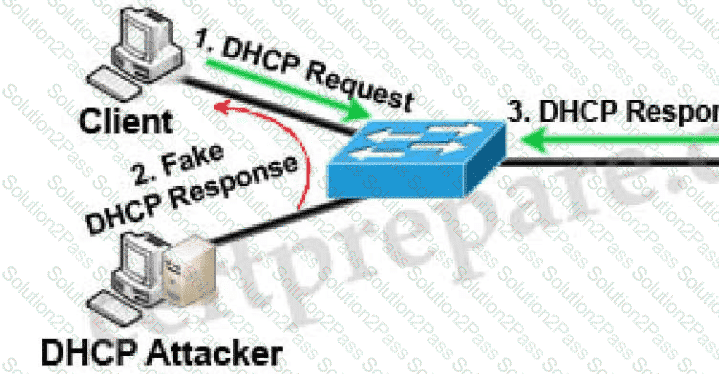
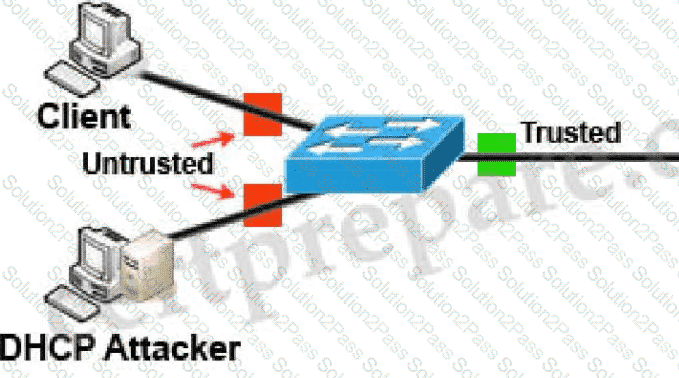
A.

Set a trusted interface for the DHCP server

B.

Set the DHCP snooping bit to 1

C.

Add entries in the DHCP snooping database

D.

Enable ARP inspection for the required VLAN

An organization is trying to improve their Defense in Depth by blocking malicious destinations prior to a

connection being established. The solution must be able to block certain applications from being used within the network. Which product should be used to accomplish this goal?

A.

Cisco Firepower

B.

Cisco Umbrella

C.

ISE

D.

AMP

Which Cisco network security device supports contextual awareness?

A.

Firepower

B.

CISCO ASA

C.

Cisco IOS

D.

ISE

Which Cisco Secure Client module is integrated with Splunk Enterprise to provide monitoring capabilities to administrators to allow them to view endpoint application usage?

A.

Umbrella Roaming Security

B.

Network Visibility

C.

AMP Enabler

D.

ISE Posture

What is the purpose of a denial-of-service attack?

A.

to disrupt the normal operation of a targeted system by overwhelming It

B.

to exploit a security vulnerability on a computer system to steal sensitive information

C.

to prevent or limit access to data on a computer system by encrypting It

D.

to spread throughout a computer system by self-replicating to additional hosts

Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize

applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?

A.

Cisco Security Intelligence

B.

Cisco Application Visibility and Control

C.

Cisco Model Driven Telemetry

D.

Cisco DNA Center

An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users.

A.

Upload the organization root CA to the Umbrella admin portal

B.

Modify the user ' s browser settings to suppress errors from Umbrella.

C.

Restrict access to only websites with trusted third-party signed certificates.

D.

Import the Umbrella root CA into the trusted root store on the user ' s device.

Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco ESA?

A.

webadvancedconfig

B.

websecurity advancedconfig

C.

outbreakconfig

D.

websecurity config

When using Cisco AMP for Networks which feature copies a file to the Cisco AMP cloud for analysis?

A.

Spero analysis

B.

dynamic analysis

C.

sandbox analysis

D.

malware analysis

Page: 3 / 8
Total 801 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved