350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
An administrator is implementing management plane protection and must configure an interface on a Cisco router to only terminate management packets that are destined for the router. Which set of IOS commands must be used to complete the implementation?
A switch with Dynamic ARP Inspection enabled has received a spoofed ARP response on a trusted interface.
How does the switch behave in this situation?
Which two fields are defined in the NetFlow flow? (Choose two)
Refer to the exhibit.
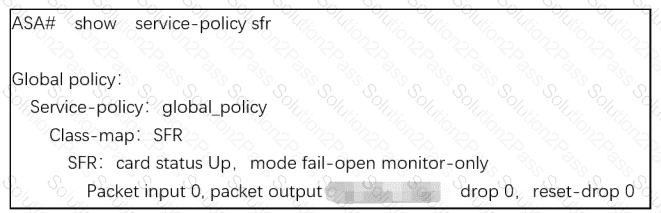
What are two indications of the Cisco Firepower Services Module configuration?
(Choose two.)
Email security has become a high priority task for a security engineer at a large multi-national organization due to ongoing phishing campaigns. To help control this, the engineer has deployed an Incoming Content Filter with a URL reputation of (-10 00 to -6 00) on the Cisco ESA Which action will the system perform to disable any links in messages that match the filter?
What is the difference between deceptive phishing and spear phishing?
What are two benefits of using Cisco Secure Access Secure Web Gateway in addition to DNS-layer protection? (Choose two.)
An organization has noticed an increase in malicious content downloads and wants to use Cisco Umbrella to prevent this activity for suspicious domains while allowing normal web traffic. Which action will accomplish this task?
An engineer adds a custom detection policy to a Cisco AMP deployment and encounters issues with the
configuration. The simple detection mechanism is configured, but the dashboard indicates that the hash is not 64 characters and is non-zero. What is the issue?
Refer to the exhibit.
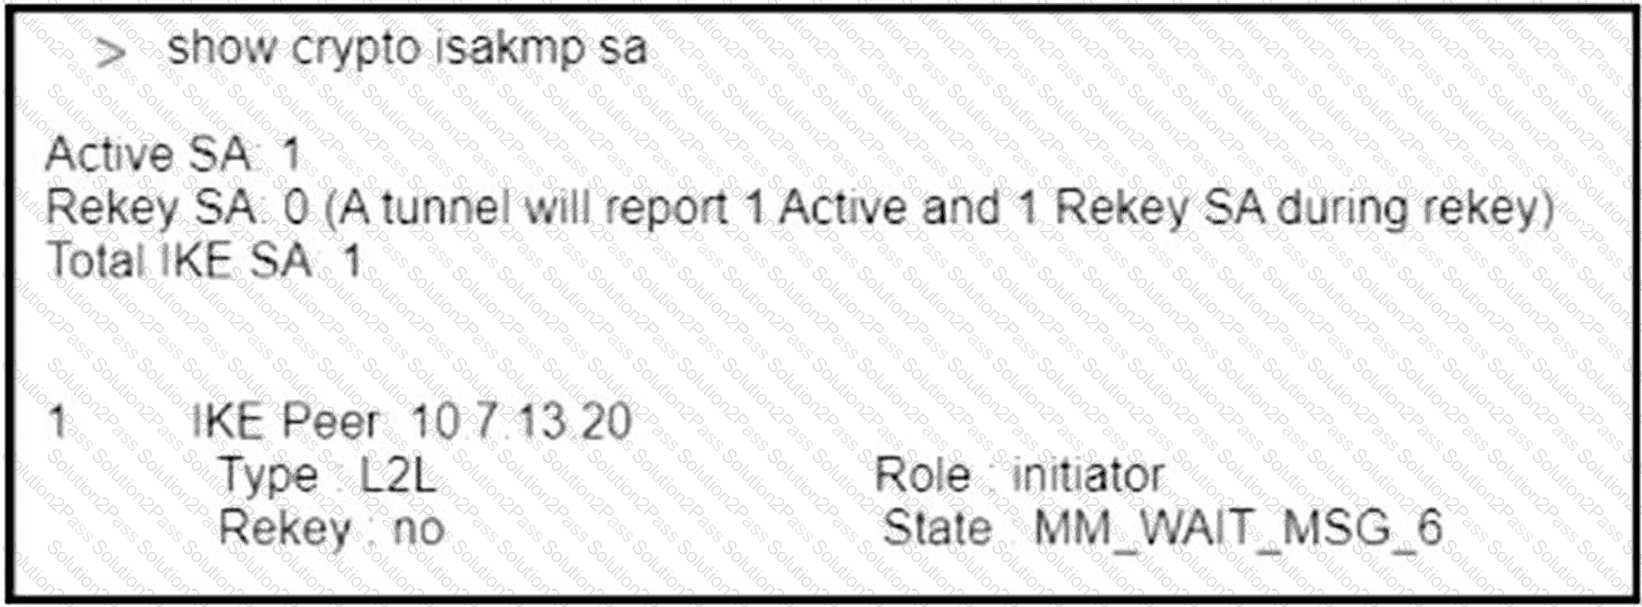
During the rollout of a new site-to-site VPN between a headquarters Cisco Secure Firewall Threat Defense device and a partner firewall, the tunnel never completes IKEv1 Phase 1 and remains in the MM_WAIT_MSG_6 state. Reachability between the firewalls over the Internet is verified, ISAKMP UDP port 500 is permitted end-to-end, and the IKE Phase 1 policy parameters—including encryption, hashing, DH group, and lifetime—match exactly on both ends. Which configuration action must be performed to resolve the issue?
Which Cisco solution does Cisco Umbrella integrate with to determine if a URL is malicious?
Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?
A company recently discovered an attack propagating throughout their Windows network via a file named abc428565580xyz exe The malicious file was uploaded to a Simple Custom Detection list in the AMP for Endpoints Portal and the currently applied policy for the Windows clients was updated to reference the detection list Verification testing scans on known infected systems shows that AMP for Endpoints is not detecting the presence of this file as an indicator of compromise What must be performed to ensure detection of the malicious file?
Which feature is leveraged by advanced antimalware capabilities to be an effective endpomt protection platform?
Which type of attack is social engineering?
A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?
What is provided by the Secure Hash Algorithm in a VPN?
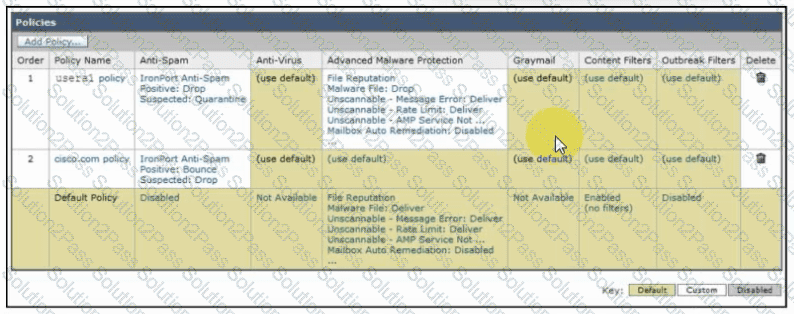
Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?
Which ID store requires that a shadow user be created on Cisco ISE for the admin login to work?
Which cryptographic process provides origin confidentiality, integrity, and origin authentication for packets?
Which two protocols must be configured to authenticate end users to the Web Security Appliance? (Choose two.)
What are two facts about WSA HTTP proxy configuration with a PAC file? (Choose two.)
Which IETF attribute is supported for the RADIUS CoA feature?
A network engineer must prevent endpoints from becoming infected by malicious files. The infrastructure includes Cisco Secure Endpoint, which must execute suspicious files in a cloud sandbox. Which feature must the engineer configure on Cisco Secure Endpoint to meet the requirement?
An engineer must modify a policy to block specific addresses using Cisco Umbrella. The policy is created already and is actively u: of the default policy elements. What else must be done to accomplish this task?
An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:
• Governance with role-based access control based on the principle of least privilege
• TLS 1.3 with signed certificates
• AES-256 with MD5
What must be configured to complete the secure implementation?
An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?
An administrator needs to configure the Cisco ASA via ASDM such that the network management system
can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?
(Choose two.)
Which telemetry data captures variations seen within the flow, such as the packets TTL, IP/TCP flags, and payload length?
What is the term for having information about threats and threat actors that helps mitigate harmful events that would otherwise compromise networks or systems?
