350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Which Cisco platform provides an agentless solution to provide visibility across the network including encrypted traffic analytics to detect malware in encrypted traffic without the need for decryption?
Which cloud model is a collaborative effort where infrastructure is shared and jointly accessed by several organizations from a specific group?
What are the two most commonly used authentication factors in multifactor authentication? (Choose two)
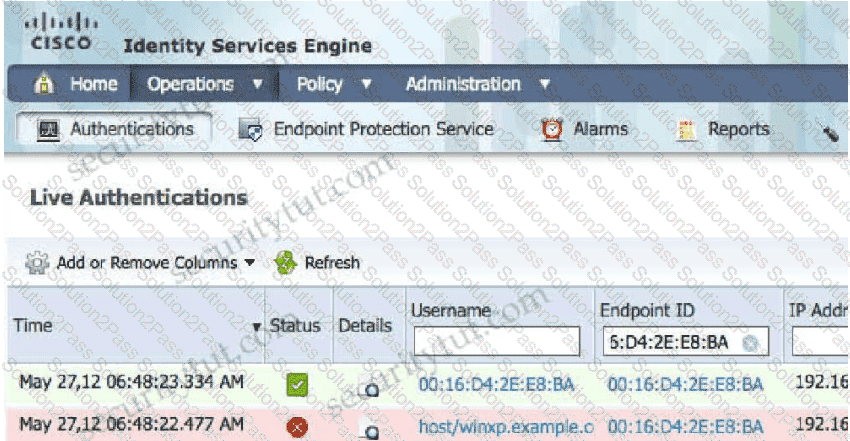
A network administrator is configuring a switch to use Cisco ISE for 802.1X. An endpoint is failing
authentication and is unable to access the network. Where should the administrator begin troubleshooting to verify the authentication details?
Which two risks is a company vulnerable to if it does not have a well-established patching solution for
endpoints? (Choose two)
What must be configured in Cisco ISE to enforce reauthentication of an endpoint session when an endpoint is
deleted from an identity group?
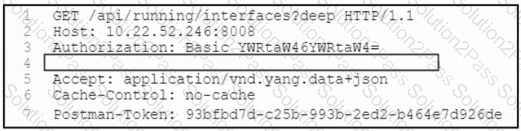
Refer to the exhibit. A network engineer must retrieve the interface configuration on a Cisco router by using the NETCONF API. The engineer uses a python script to automate the activity.
Which code snippet completes the script?
An organization configures Cisco Umbrella to be used for its DNS services. The organization must be able to block traffic based on the subnet that the endpoint is on but it sees only the requests from its public IP address instead of each internal IP address. What must be done to resolve this issue?
A customer has various external HTTP resources available including Intranet Extranet and Internet, with a
proxy configuration running in explicit mode. Which method allows the client desktop browsers to be configured
to select when to connect direct or when to use the proxy?
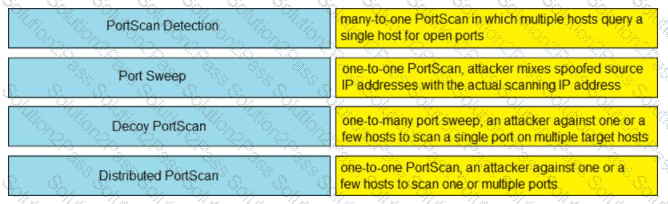
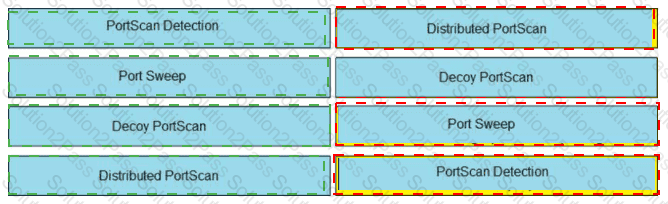
Drag and drop the Firepower Next Generation Intrusion Prevention System detectors from the left onto the correct definitions on the right.
Which benefit does endpoint security provide the overall security posture of an organization?
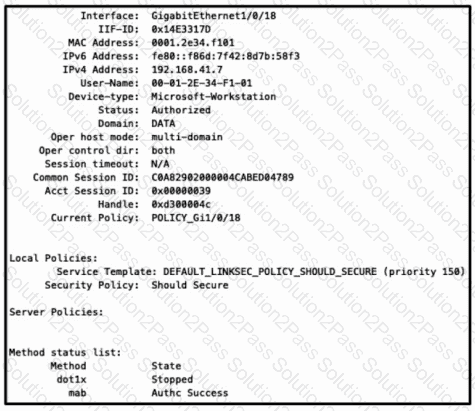
Refer to the exhibit. Which configuration item makes it possible to have the AAA session on the network?
Which solution stops unauthorized access to the system if a user ' s password is compromised?
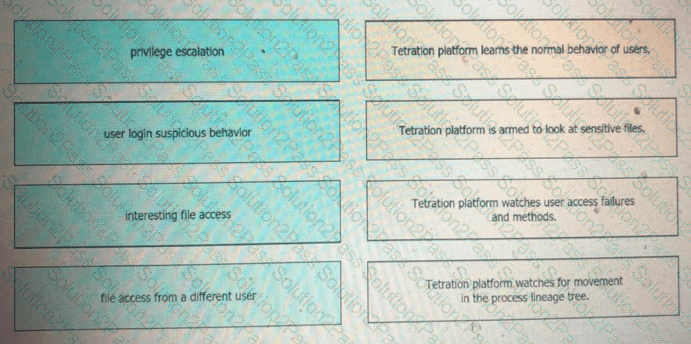
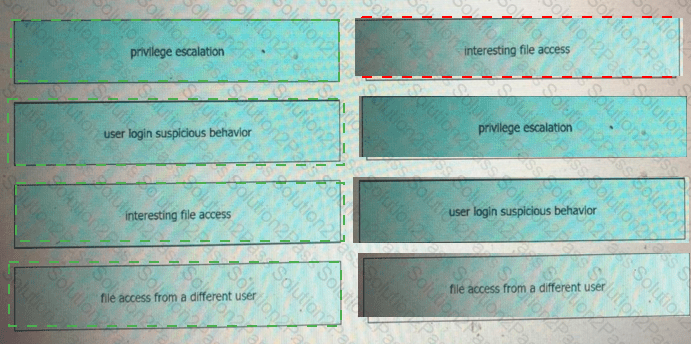
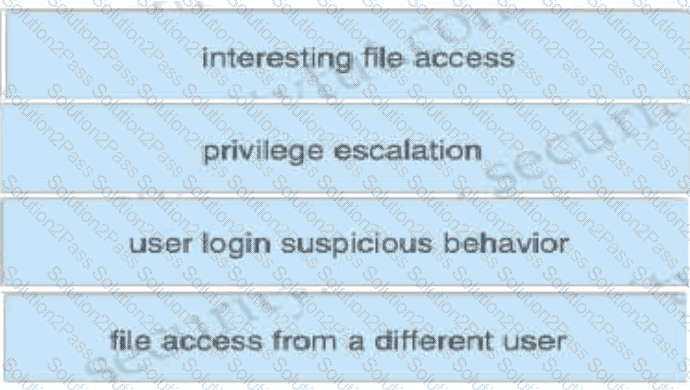
Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
Which solution should be leveraged for secure access of a CI/CD pipeline?
Which Splunk SOAR component automates multi-step security actions into a repeatable workflow?
What must be enabled to secure SaaS-based applications?
What does endpoint isolation in Cisco AMP for Endpoints security protect from?
A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?
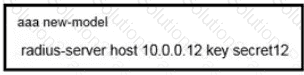
Refer to the exhibit. What is the result of using this authentication protocol in the configuration?
What are two functionalities of SDN Northbound APIs? (Choose two.)
Which action controls the amount of URI text that is stored in Cisco WSA logs files?
What is the most common type of data exfiltration that organizations currently experience?
Refer to the exhibit.
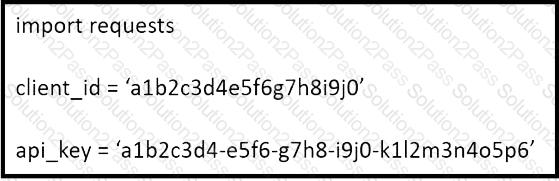
What does the API key do while working with https://api.amp.cisco.com/v1/computers?
Which Cisco AMP feature allows an engineer to look back to trace past activities, such as file and process
activity on an endpoint?
What can be integrated with Cisco Threat Intelligence Director to provide information about security threats,
which allows the SOC to proactively automate responses to those threats?
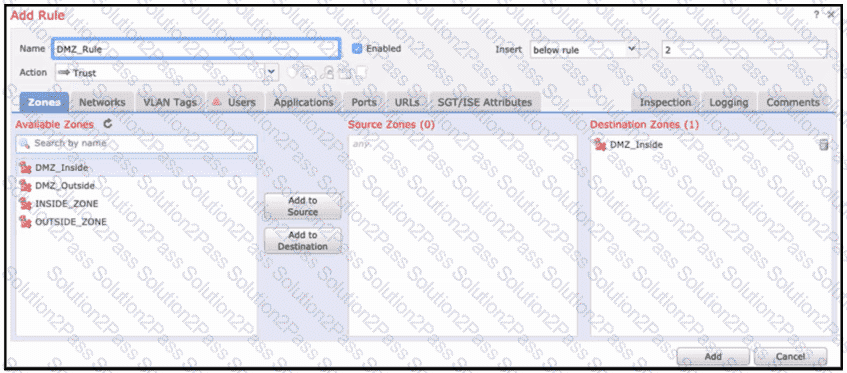
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?
An engineer must modify a policy to block specific addresses using Cisco Umbrella. The policy is created already and is actively used by devices, using many of the default policy elements.
What else must be done to accomplish this task?
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
Which security control is required for identifying and neutralizing malicious code that attempts to execute on an endpoint?
