Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 7 / 8
Total 801 questions

Which feature within Cisco Umbrella allows for the ability to inspect secure HTTP traffic?

A.

File Analysis

B.

SafeSearch

C.

SSL Decryption

D.

Destination Lists

An organization has a Cisco ESA set up with policies and would like to customize the action assigned for

violations. The organization wants a copy of the message to be delivered with a message added to flag it as a

DLP violation. Which actions must be performed in order to provide this capability?

A.

deliver and send copies to other recipients

B.

quarantine and send a DLP violation notification

C.

quarantine and alter the subject header with a DLP violation

D.

deliver and add disclaimer text

Which baseline form of telemetry is recommended for network infrastructure devices?

A.

SDNS

B.

NetFlow

C.

passive taps

D.

SNMP

A network engineer is deciding whether to use stateful or stateless failover when configuring two ASAs for high availability. What is the connection status in both cases?

A.

need to be reestablished with stateful failover and preserved with stateless failover

B.

preserved with stateful failover and need to be reestablished with stateless failover

C.

preserved with both stateful and stateless failover

D.

need to be reestablished with both stateful and stateless failover

Which security solution uses NetFlow to provide visibility across the network, data center, branch offices, and cloud?

A.

Cisco CTA

B.

Cisco Encrypted Traffic Analytics

C.

Cisco Umbrella

D.

Cisco Secure Network Analytics

An engineer is deploying Cisco Advanced Malware Protection (AMP) for Endpoints and wants to create a policy that prevents users from executing file named abc424952615.exe without quarantining that file What type of Outbreak Control list must the SHA.-256 hash value for the file be added to in order to accomplish this?

A.

Advanced Custom Detection

B.

Blocked Application

C.

Isolation

D.

Simple Custom Detection

How does Cisco Umbrella archive logs to an enterprise owned storage?

A.

by using the Application Programming Interface to fetch the logs

B.

by sending logs via syslog to an on-premises or cloud-based syslog server

C.

by the system administrator downloading the logs from the Cisco Umbrella web portal

D.

by being configured to send logs to a self-managed AWS S3 bucket

Which configuration method provides the options to prevent physical and virtual endpoint devices that are in the same base EPG or uSeg from being able to communicate with each other with Vmware VDS or Microsoft vSwitch?

A.

inter-EPG isolation

B.

inter-VLAN security

C.

intra-EPG isolation

D.

placement in separate EPGs

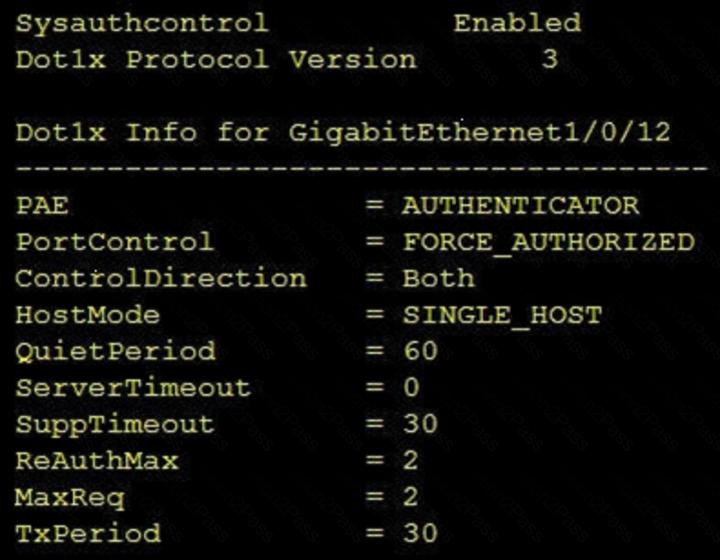
Refer to the exhibit.

Which command was used to display this output?

A.

show dot1x all

B.

show dot1x

C.

show dot1x all summary

D.

show dot1x interface gi1/0/12

Which threat intelligence standard contains malware hashes?

A.

structured threat information expression

B.

advanced persistent threat

C.

trusted automated exchange or indicator information

D.

open command and control

An engineer is implementing Cisco CES in an existing Microsoft Office 365 environment and must route inbound email to Cisco CE.. record must be modified to accomplish this task?

A.

CNAME

B.

MX

C.

SPF

D.

DKIM

A security administrator is designing an email protection solution for an onsite email server and must meet these requirements:

Remove malware from email before it reaches corporate premises

Drop emails with risky links automatically

Block access to newly infected sites with real-time URL analysis

Which solution must be used?

A.

Cisco Secure Email Cloud

B.

Cisco Security for Office 365

C.

Cisco Stealthwatch Cloud

D.

Cisco Secure Email and Web Manager Cloud

What are two list types within AMP for Endpoints Outbreak Control? (Choose two)

A.

blocked ports

B.

simple custom detections

C.

command and control

D.

allowed applications

E.

URL

Under which two circumstances is a CoA issued? (Choose two)

A.

A new authentication rule was added to the policy on the Policy Service node.

B.

An endpoint is deleted on the Identity Service Engine server.

C.

A new Identity Source Sequence is created and referenced in the authentication policy.

D.

An endpoint is profiled for the first time.

E.

A new Identity Service Engine server is added to the deployment with the Administration persona

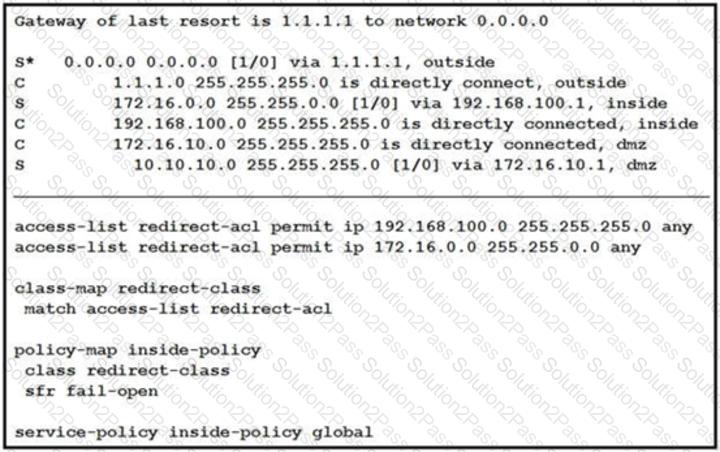
Refer to the exhibit.

What is a result of the configuration?

A.

Traffic from the DMZ network is redirected

B.

Traffic from the inside network is redirected

C.

All TCP traffic is redirected

D.

Traffic from the inside and DMZ networks is redirected

An engineer is configuring Cisco WSA and needs to enable a separated email transfer flow from the Internet and from the LAN. Which deployment mode must be used to accomplish this goal?

A.

single interface

B.

multi-context

C.

transparent

D.

two-interface

Which solution is made from a collection of secure development practices and guidelines that developers must follow to build secure applications?

A.

AFL

B.

Fuzzing Framework

C.

Radamsa

D.

OWASP

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites

but other sites are not accessible due to an error. Why is the error occurring?

A.

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.

IP-Layer Enforcement is not configured.

C.

Client computers do not have an SSL certificate deployed from an internal CA server.

D.

Intelligent proxy and SSL decryption is disabled in the policy

What is the difference between a vulnerability and an exploit?

A.

A vulnerability is a hypothetical event for an attacker to exploit

B.

A vulnerability is a weakness that can be exploited by an attacker

C.

An exploit is a weakness that can cause a vulnerability in the network

D.

An exploit is a hypothetical event that causes a vulnerability in the network

In a federated single sign-on environment, which protocol exchanges XML-based assertions between an identity provider and a service provider for authentication?

A.

SAML

B.

OAuth 2.0

C.

LDAP

D.

RADIUS

Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention

System?

A.

Correlation

B.

Intrusion

C.

Access Control

D.

Network Discovery

Which API method and required attribute are used to add a device into Cisco DNA Center with the native API?

A.

GET and serialNumber

B.

userSudiSerlalNos and deviceInfo

C.

POST and name

D.

lastSyncTime and pid

What is the role of an endpoint in protecting a user from a phishing attack?

A.

Use Cisco Stealthwatch and Cisco ISE Integration.

B.

Utilize 802.1X network security to ensure unauthorized access to resources.

C.

Use machine learning models to help identify anomalies and determine expected sending behavior.

D.

Ensure that antivirus and anti malware software is up to date

Which two tasks allow NetFlow on a Cisco ASA 5500 Series firewall? (Choose two)

A.

Enable NetFlow Version 9.

B.

Create an ACL to allow UDP traffic on port 9996.

C.

Apply NetFlow Exporter to the outside interface in the inbound direction.

D.

Create a class map to match interesting traffic.

E.

Define a NetFlow collector by using the flow-export command

A large enterprise is currently managing a hybrid environment consisting of a private data center and multiple public cloud providers. The security engineering team is concerned about “Shadow IT” and the lack of visibility into unauthorized cloud services being used by various departments. The architect must select a solution that provides comprehensive discovery of cloud application usage and assesses the risk of each service based on industry certifications. Which technical solution must be used to provide cross-environment visibility?

A.

EDR

B.

CASB

C.

Secure Firewall

D.

CWPP

Which parameter is required when configuring a Netflow exporter on a Cisco Router?

A.

DSCP value

B.

Source interface

C.

Exporter name

D.

Exporter description

What are two benefits of Flexible NetFlow records? (Choose two)

A.

They allow the user to configure flow information to perform customized traffic identification

B.

They provide attack prevention by dropping the traffic

C.

They provide accounting and billing enhancements

D.

They converge multiple accounting technologies into one accounting mechanism

E.

They provide monitoring of a wider range of IP packet information from Layer 2 to 4

What is the primary role of the Cisco Email Security Appliance?

A.

Mail Submission Agent

B.

Mail Transfer Agent

C.

Mail Delivery Agent

D.

Mail User Agent

What are two functions of secret key cryptography? (Choose two)

A.

key selection without integer factorization

B.

utilization of different keys for encryption and decryption

C.

utilization of large prime number iterations

D.

provides the capability to only know the key on one side

E.

utilization of less memory

Which feature enforces continuous connectivity by preventing users from disconnecting the Cisco Secure Client tunnel?

A.

Always-On

B.

Smart Tunnel

C.

Path MTU Discovery

D.

Allow Local LAN Access

Page: 7 / 8
Total 801 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved