350-701 Cisco Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Cisco 350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
After a recent breach, an organization determined that phishing was used to gain initial access to the network before regaining persistence. The information gained from the phishing attack was a result of users visiting known malicious websites. What must be done in order to prevent this from happening in the future?
Which type of algorithm provides the highest level of protection against brute-force attacks?
An administrator is trying to determine which applications are being used in the network but does not want the
network devices to send metadata to Cisco Firepower. Which feature should be used to accomplish this?
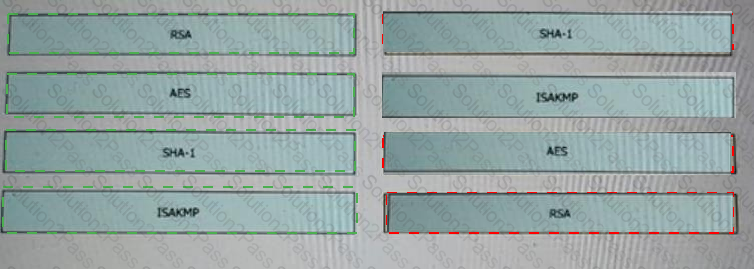
Drag and drop the VPN functions from the left onto the description on the right.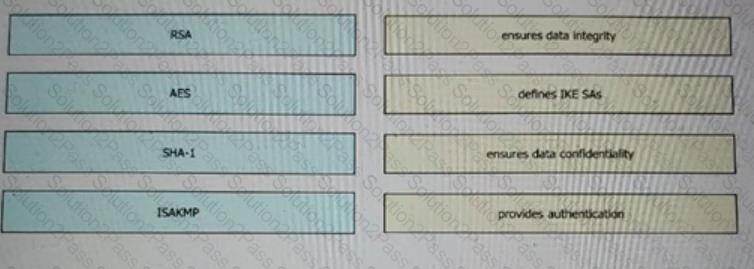
What are two rootkit types? (Choose two)
Which key feature of Cisco ZFW is unique among other Cisco IOS firewall solutions?
Which Cisco ASA Platform mode disables the threat detection features except for Advanced Threat Statistics?
A network administrator is modifying a remote access VPN on an FTD managed by an FMC. The administrator wants to offload traffic to certain trusted domains. The administrator wants this traffic to go out of the client ' s local internet and send other internet-bound traffic over the VPN Which feature must the administrator configure?
What is the most commonly used protocol for network telemetry?
What is a benefit of an endpoint patch management strategy?
Which solution detects threats across a private network, public clouds, and encrypted traffic?
Which VPN technology supports a multivendor environment and secure traffic between sites?
What is the recommendation in a zero-trust model before granting access to corporate applications and resources?
Which two solutions help combat social engineering and phishing at the endpoint level? (Choose two.)
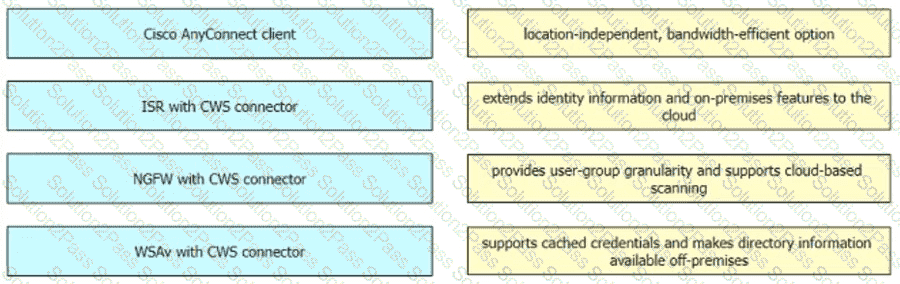
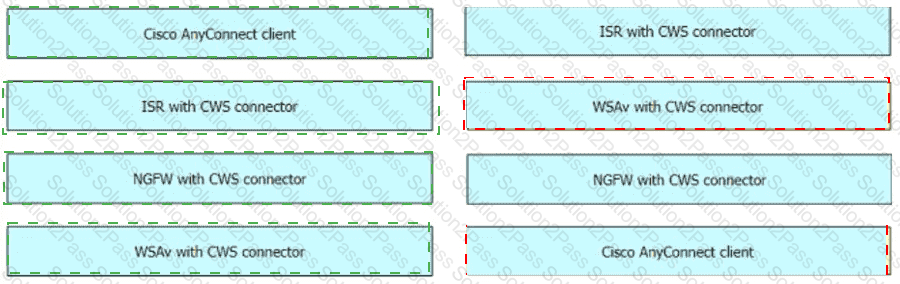
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256
cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?
Which type of dashboard does Cisco Catalyst Center provide for complete control of the network?
Refer to the exhibit.
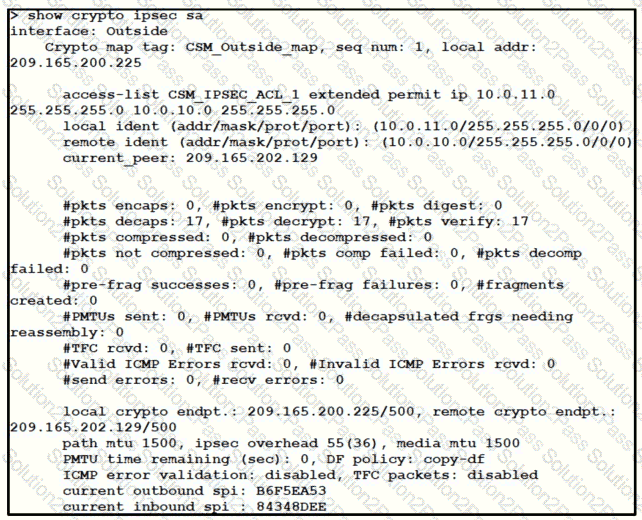
Traffic is not passing through IPsec site-to-site VPN on the Firepower Threat Defense appliance. What is causing this issue?
A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?
Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?
Which capability is provided by application visibility and control?
What are two characteristics of Cisco Catalyst Center APIs? (Choose two.)
Which RADIUS feature provides a mechanism to change the AAA attributes of a session after it is
authenticated?
Which Cisco solution extends network visibility, threat detection, and analytics to public cloud environments?
Which protocol does Cisco Duo use to transport authentication assertions for single sign-on?
Which Cisco security solution protects remote users against phishing attacks when they are not connected to
the VPN?
What are two recommended approaches to stop DNS tunneling for data exfiltration and command and control call backs? (Choose two.)
What are two benefits of using Cisco Duo as an MFA solution? (Choose two.)
What are the two types of managed Intercloud Fabric deployment models? (Choose two.)
What is the target in a phishing attack?
