Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Fortinet NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 2 / 2
Total 96 questions

Refer to Exhibit:

You are tasked with reviewing a new FortiAnalyzer deployment in a network with multiple registered logging devices. There is only one FortiAnalyzer in the topology.

Which potential problem do you observe?

A.

The disk space allocated is insufficient.

B.

The analytics-to-archive ratio is misconfigured.

C.

The analytics retention period is too long.

D.

The archive retention period is too long.

What are three capabilities of the built-in FortiSOAR Jinja editor? (Choose three answers)

A.

It renders output by combining Jinja expressions and JSON input.

B.

It checks the validity of a Jinja expression.

C.

It creates new records in bulk.

D.

It loads the environment JSON of a recently executed playbook.

E.

It defines conditions to trigger a playbook step.

Which two ways can you create an incident on FortiAnalyzer? (Choose two answers)

A.

Using a custom event handler

B.

Using a connector action

C.

Manually, on the Event Monitor page

D.

By running a playbook

You want to automate a workflow on FortiSOAR so that whenever an incident is moved to the Aftermath phase, it is automatically set to status Resolved and assigned to a purple team specialist as incident lead to write an incident report. In addition, a manual task, assigned to the same specialist, will be created so they are aware of the pending work. Which three steps will accomplish this task? Choose three answers.

A.

Create a Find Record step to find matching incidents.

B.

Create a Condition step to assign both the incident and task to the specialist.

C.

Create a Manual Task step to assign the task to the specialist.

D.

Create an Update Record step to set the incident lead.

E.

Create an On Update trigger with a trigger condition that matches the Aftermath phase.

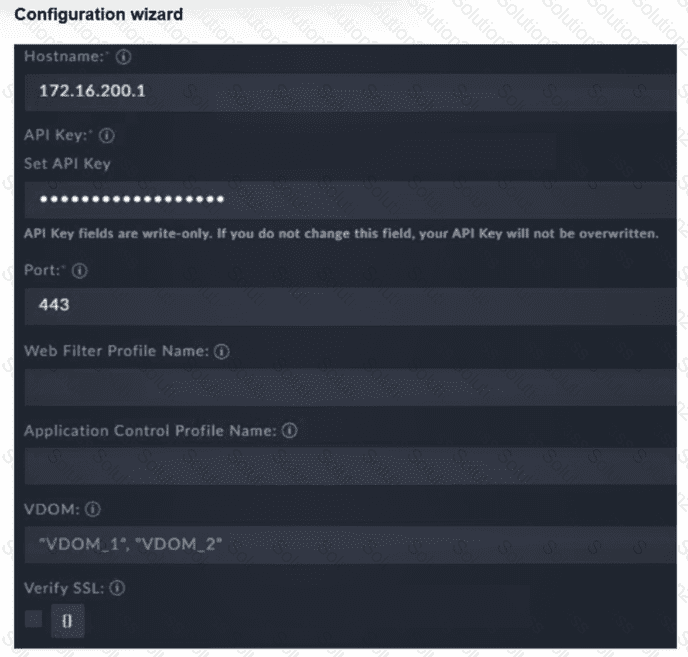
Refer to the exhibit.

You must configure the FortiGate connector to allow FortiSOAR to perform actions on a firewall. However, the connection fails. Which two configurations are required? (Choose two answers)

A.

Trusted hosts must be enabled and the FortiSOAR IP address must be permitted.

B.

The VDOM name must be specified, or set to VDOM_1, if VDOMs are not enabled on FortiGate.

C.

HTTPS must be enabled on the FortiGate interface that FortiSOAR will communicate with.

D.

An API administrator must be created on FortiGate with the appropriate profile, along with a generated API key to configure on the connector.

Based on the Pyramid of Pain model, which two statements accurately describe the value of an indicator and how difficult it is for an adversary to change? (Choose two answers)

A.

IP addresses are easy because adversaries can spoof them or move them to new resources.

B.

Tactics, techniques, and procedures are hard because adversaries must adapt their methods.

C.

Artifacts are easy because adversaries can alter file paths or registry keys.

D.

Tools are easy because often, multiple alternatives exist.

Refer to Exhibit:

A SOC analyst is creating the Malicious File Detected playbook to run when FortiAnalyzer generates a malicious file event. The playbook must also update the incident with the malicious file event data.

What must the next task in this playbook be?

A.

A local connector with the action Update Asset and Identity

B.

A local connector with the action Attach Data to Incident

C.

A local connector with the action Run Report

D.

A local connector with the action Update Incident

Which statement best describes the MITRE ATT & CK framework?

A.

It provides a high-level description of common adversary activities, but lacks technical details

B.

It covers tactics, techniques, and procedures, but does not provide information about mitigations.

C.

It describes attack vectors targeting network devices and servers, but not user endpoints.

D.

It contains some techniques or subtechniques that fall under more than one tactic.

Page: 2 / 2
Total 96 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved