Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: stp75

Easiest Solution 2 Pass Your Certification Exams

NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator Free Practice Exam Questions (2026 Updated)

Prepare effectively for your Fortinet NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.

Page: 2 / 2
Total 114 questions

Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)

A.

Enabling DHCP snooping on a FortiSwitch VLAN ensures requests and replies are seen by all DHCP servers.

B.

switch-controller-dhcp-snooping-verify-mac verifies the destination MAC address to protect against DHCP exhaustion attacks.

C.

By default, all FortiSwitch ports are set to forward client DHCP requests to untrusted ports.

D.

Settings related to DHCP option 82 are only configurable through the CLI

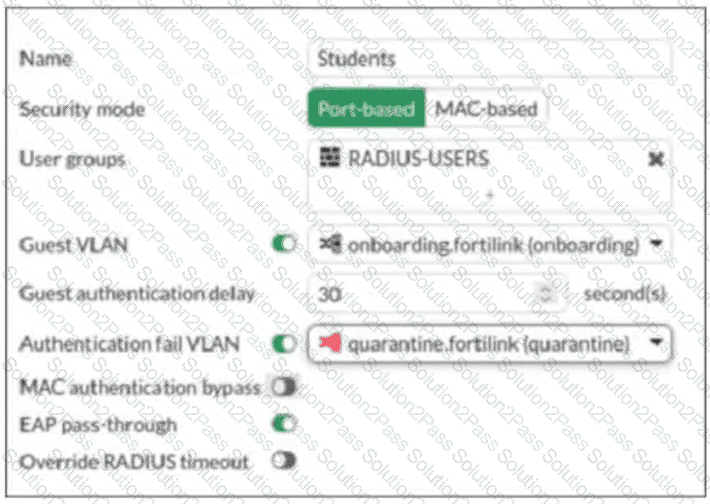
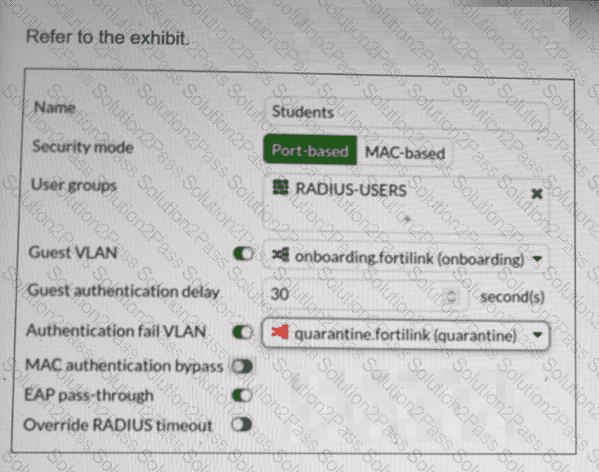
Refer to the exhibit.

The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X? (Choose one answer)

A.

The device is blocked from accessing the network.

B.

The device is placed into the onboarding VLAN.

C.

The device is placed into the quarantine VLAN.

D.

The device is assigned to the default management VLAN.

Exhibit.

You need to manage three FortiSwitch devices using a FortiGate device. Two of the FortiSwitch devices initiated a reboot after the authorization process. However, the FortiSwitch device with the configuration shown in the exhibit. did not reboot All three devices completed FortiLink manage-ment authorization successfully.

Why did the FortiSwitch device shown in the exhibit not reboot to complete the authorization pro-cess?

The management mode was set to use FortiLink mode.

A.

Switch auto-discovery is enabled.

B.

The management mode was set to use FortiLink mode.

C.

The FortiSwitch device is scheduled to reboot as part the authorization process

D.

The system time is not in-sync and is using a non-default value

What does the switchauto-networksetting control on FortiSwitch? (Choose one answer)

A.

The automatic VLAN assignment based on connected devices

B.

The automatic discovery of the FortiGate- > FortiLink interface

C.

The root bridge priority for Multiple Spanning Tree Protocol (MSTP)

D.

Whether the FortiSwitch can be managed by FortiManager

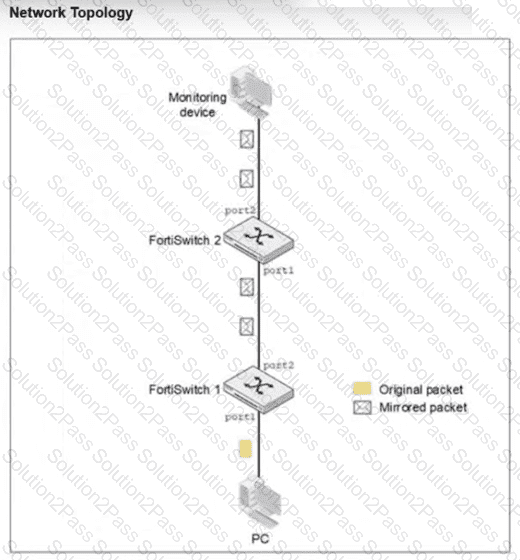
Refer to the exhibit.

You configured Switched Port Analyzer (SPAN) to monitor traffic from a source port on FortiSwitch 1, but the monitoring device is connected to FortiSwitch 2. After port mirroring configuration on FortiSwitch 1, the monitoring device is not receiving any mirrored traffic.

What is the most likely reason the mirrored traffic is not reaching the monitoring device? (Choose one answer)

A.

SPAN does not support forwarding mirrored traffic across multiple switches.

B.

SPAN traffic must be filtered with an access control list (ACL).

C.

The SPAN session must be restarted after configuration.

D.

The monitoring device must use a management IP in the same subnet.

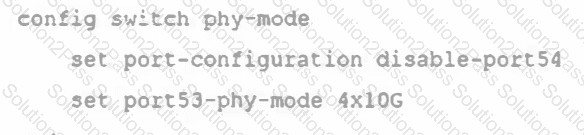
Exhibit.

What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces.

B.

The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.

C.

The port full speed prior the split was 100G SFP+

D.

The split port can be assigned to native VLAN

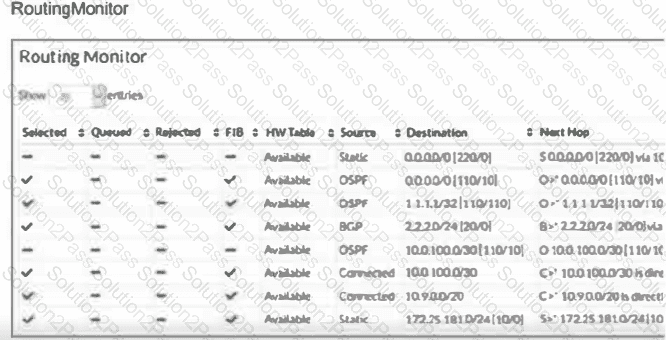
Exhibit.

Two routes are not installed in the forwarding information base (FIB) as shown in the exnibit. Which two statements about these two route entries are true? (Choose two.)

A.

These two routes have a higher administrative distance value available to the destination networks.

B.

These two routes will become primary, if the best routes are removed.

C.

These two routes will be used as load-balancing routes.

D.

These two routes are available in the hardware routing table.

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices

Which QoS mechanism maps packets with specific class of service (COS) or Differentiated Services Code Point (DSCP) markings to an egress queue? (Choose one answer)

A.

Classification for ingress traffic

B.

Queuing for egress traffic

C.

Policing for ingress traffic

D.

Shaping for egress traffic

(Full question statement start from here)

When you change FortiSwitch management mode fromstandalonetomanaged, what happens to the existing standalone configuration? (Choose one answer)

A.

FortiSwitch registers to FortiSwitch Cloud to save a copy before managing with FortiGate.

B.

FortiSwitch merges the existing standalone configuration with the default FortiLink configuration.

C.

FortiSwitch saves the standalone configuration and changes to the default FortiLink configuration.

D.

FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.

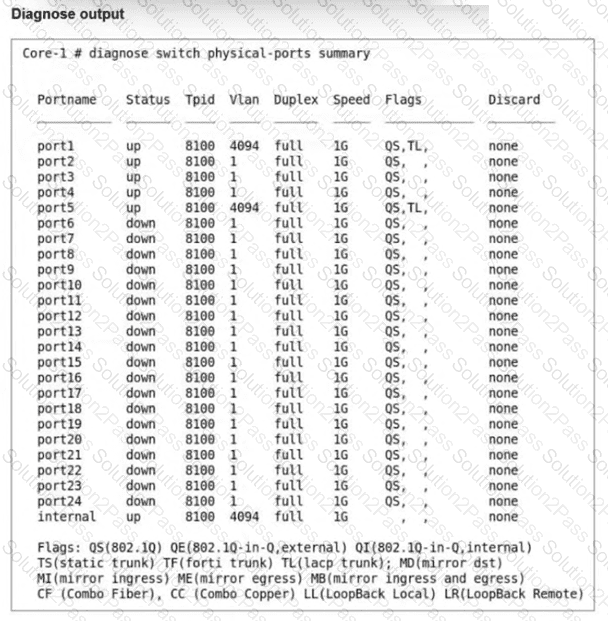
Refer to the exhibit.

The command diagnose switch physical-ports summary is executed on FortiSwitch.

Based on the VLAN assignments shown in the output, what is the most likely management configuration of this FortiSwitch? (Choose one answer)

A.

FortiSwitch is managed by FortiSwitch Cloud.

B.

FortiSwitch is managed by FortiGate.

C.

FortiSwitch is operating in standalone mode.

D.

FortiSwitch is operating in local mode.

Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)

A.

A FortiLink interface must be enabled on FortiGate.

B.

The switch controller feature must be enabled on FortiGate.

C.

Only a hardware-based FortiGate can manage a FortiSwitch stack.

D.

FortiSwitch must be operating in standalone mode before authorization.

(Full question statement start from here)

You are deploying a FortiSwitch virtual stack in a network that contains Cisco devices. You want the Cisco devices toautomatically discover the FortiSwitch devices and exchange device information. Which two protocols must be enabled on the FortiSwitch devices to achieve this? (Choose two answers)

A.

Unidirectional Link Detection

B.

Cisco Discovery Protocol

C.

Link Layer Discovery Protocol

D.

LLDP – Media Endpoint Discovery

Refer to the exhibit.

FortiSwitch 802.1X port security configuration is shown. A user connects their laptop to the port and attempts to authenticate using 802.1X, but enters the wrong credentials multiple times. What will the result to the device be? (Choose one answer)

A.

The device will be placed into the VLAN quarantine.

B.

The port will shut down for security reasons.

C.

The device will be placed into the VLAN onboarding.

D.

The device will be assigned to the default management VLAN.

Page: 2 / 2
Total 114 questions
Copyright © 2014-2026 Solution2Pass. All Rights Reserved