NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator Free Practice Exam Questions (2026 Updated)
Prepare effectively for your Fortinet NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator certification with our extensive collection of free, high-quality practice questions. Each question is designed to mirror the actual exam format and objectives, complete with comprehensive answers and detailed explanations. Our materials are regularly updated for 2026, ensuring you have the most current resources to build confidence and succeed on your first attempt.
Exhibit.
port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)
You are configuring VLANs on a FortiSwitch device managed by FortiGate. Which two statements accurately describe VLAN assignment requirements and behavior on FortiSwitch ports? (Choose two answers)
Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?
Refer to the exhibits.
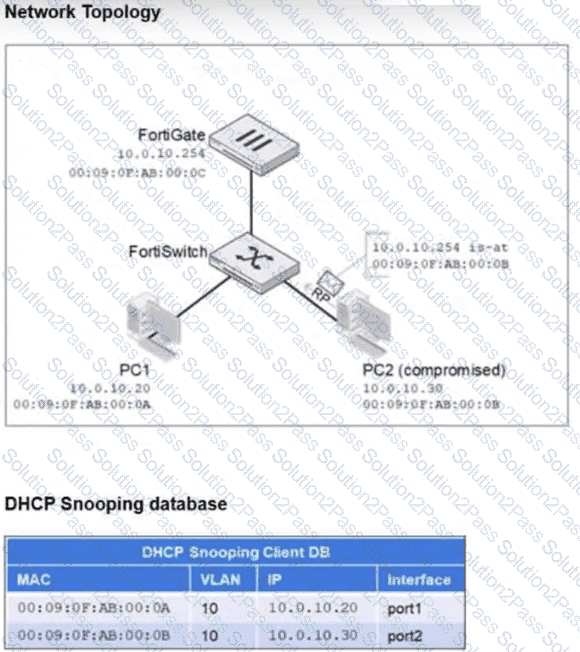
All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)
Refer to the exhibits. An IP phone is connected to port1 of FortiSwitch Access-1. The IP phone tags its traffic with VLAN ID 20. On FortiGate, VLAN IP_Phone (VLAN ID 20) has been configured, and port1 of Access-1 is set with VLAN 20 as the native VLAN. However, the IP phone cannot reach the network. The exhibit shows the partial VLAN configuration and the port1 configuration on Access-1.
Which configuration change must you make on FortiSwitch to allow ingress and egress traffic for the IP phone? (Choose one answer)
Which feature should you enable to reduce the number or unwanted IGMP reports processed by the IGMP querier?
Refer to the exhibit.
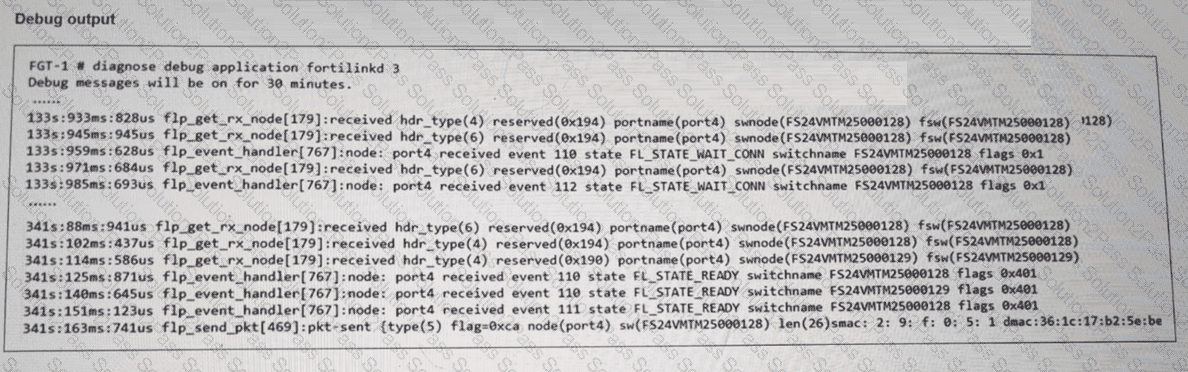
You have just authorized a new FortiSwitch on your FortiGate, and it appears online in the GUI. To verify that FortiLink connectivity is healthy, what should you check next? (Choose one answer)
(Full question statement start from here)
Refer to the exhibits.
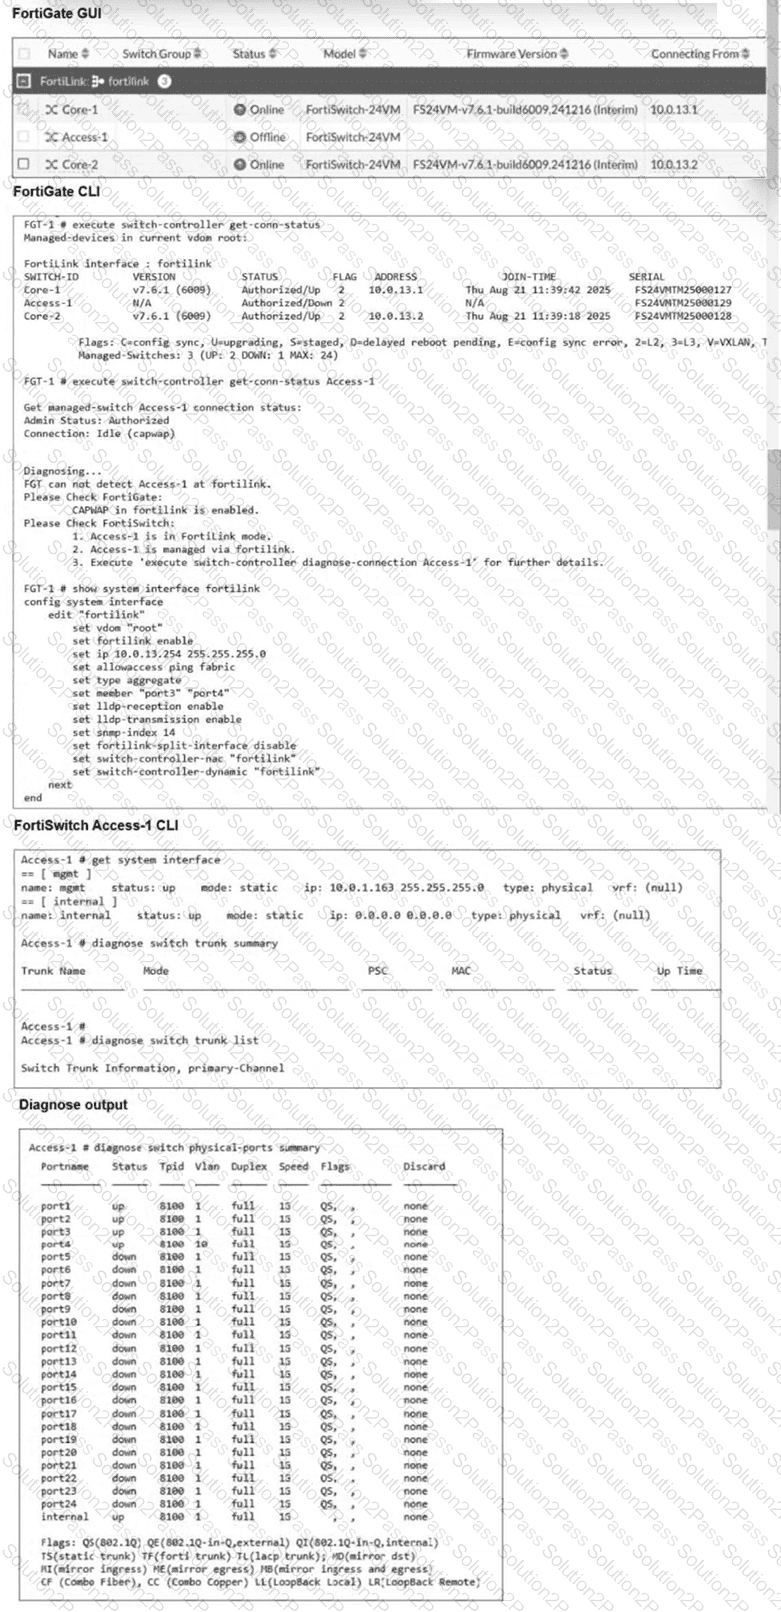
Three FortiSwitch devices were recently configured to be managed by FortiGate. Two are managed successfully, butFortiSwitch Access-1is not.
Based on the configuration output, whichinitial changeis required for FortiSwitch Access-1 to be managed? (Choose one answer)
Refer to the exhibit.
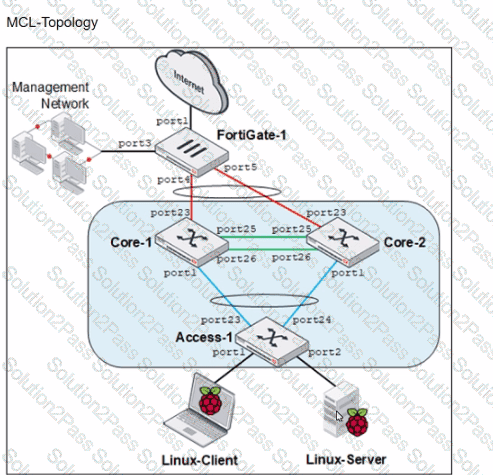
Core-1 and Access-1 are managed and authorized by FortiGate-1. which uses port4 as the FortiLink interface. After FortiGate authorizes and manages Core-2. Port1 status becomes STP discarding.
Why is port1 in the discarding state?
Refer to the exhibit.
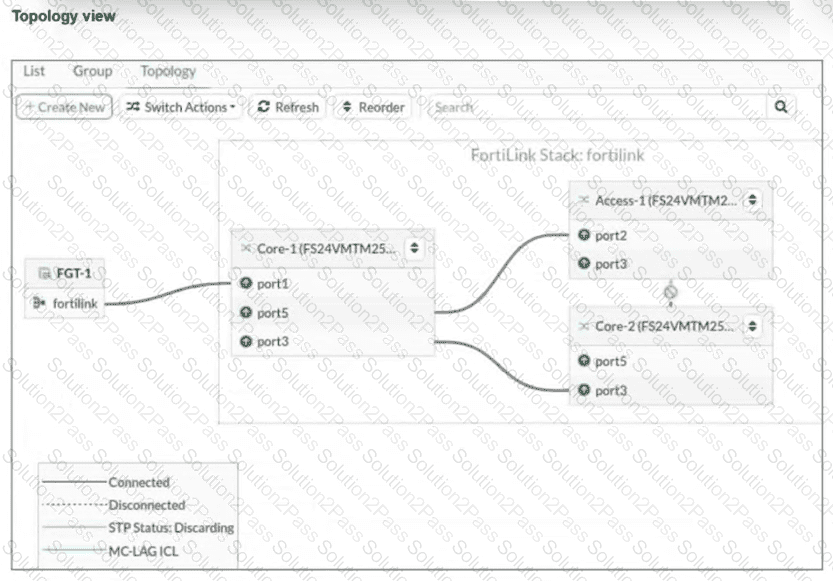
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)
What type of multimode transceiver can be used to split a 40G port?
You are designing a FortiSwitch backbone where every FortiSwitch device must connect to every other FortiSwitch for maximum redundancy. To maintain connectivity while preventing loops, which protocol or feature must you configure on the switches? (Choose one answer)
To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?
You need to mirror traffic from a source port on Switch A to a monitoring device on Switch C. For that purpose, you’re configuring Remote Switched Port Analyzer (RSPAN).1Due to the nature of RSPAN, what is the best practice when setting it up? (Choose one answer)
Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)
Refer to the diagnostic output:
What makes the use of the sniffer command on the FortiSwitch CLI unreliable on__port__23?
Refer to the exhibit.
What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)
You are designing a multi-tenant network using FortiSwitch devices in standalone mode. Security is a priority and each tenant’s servers must be completely isolated from one another, and from all other servers in the network, to prevent lateral communication. However, all servers must have access to the shared FortiGate firewall for internet access. Which type of private VLAN (PVLAN) configuration should you apply to meet these security requirements? (Choose one answer)
An administrator must deploy managed FortiSwitch devices in a remote location where multiple VLANs must be used to segment devices. No layer 3 switch or router is present at the site, and the only WAN connectivity is an ISP-provided router connected to the public internet. Which two components are required to enable VLAN segmentation across this remote site? (Choose two answers)
Which statement about the IGMP snooping querier when enabled on a VLAN is true?
